HTB PROFESSIONAL LABS

Professional Labs Directory

Explore HTB’s collection of Professional Labs, discover what each scenario offers, and find the right ones to develop and assess your team's cybersecurity skills.

Cloud Labs

Build hands-on cloud offensive security skills across AWS, Azure, and GCP, covering cloud enumeration, misconfigurations, serverless exploitation, and web and API vulnerabilities. Designed for cloud professionals and aspiring security practitioners, these labs develop practical penetration testing skills across cloud environments, including lateral movement, privilege escalation, and security mitigations.

Blacksky Hailstorm lab avatar
HTB CLOUD LAB

Blacksky Hailstorm (AWS)

DIFFICULTY Medium
RESOURCES 14
FLAGS 15
NETWORK TOPOLOGY LAB ENVIRONMENT
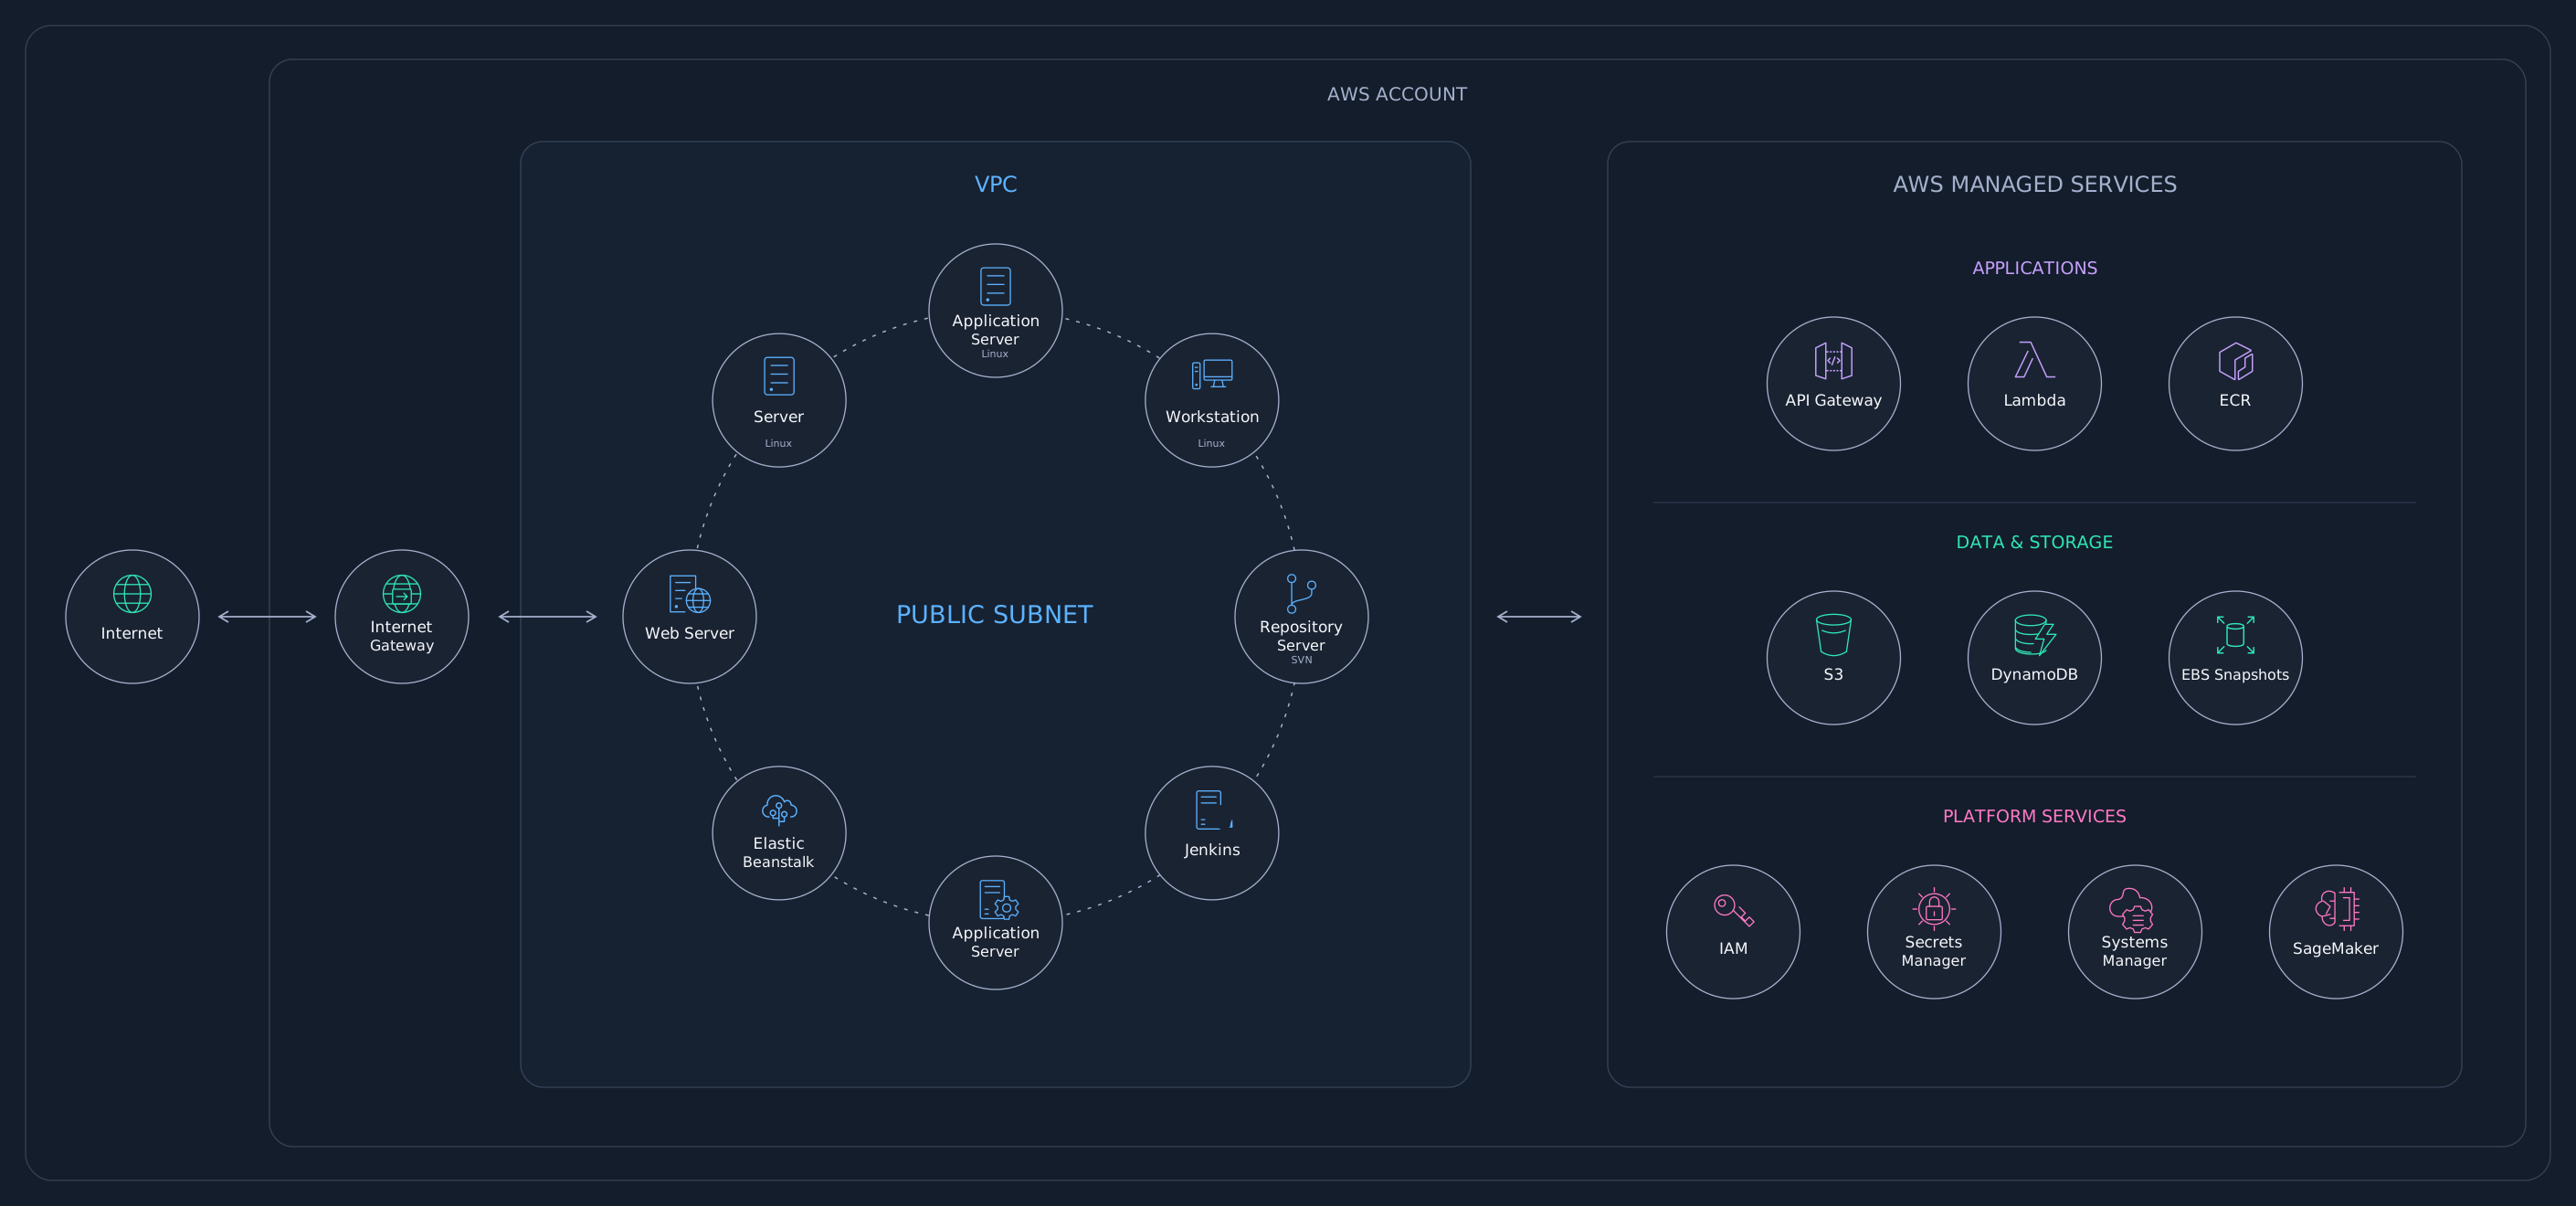
Blacksky Hailstorm lab network topology diagram
ABOUT THE LAB

BlackSky Hailstorm is a cloud penetration testing labs that features a wide-range of misconfigurations, common privilege escalation techniques, and attack paths seen in real engagements in AWS. It covers how to exploit the vulnerabilities, and importantly, how they can be mitigated.

THE SCENARIO

Mega Multinational is a global leader in the Freight Logistics industry. They are not cloud native, but are looking to transition more infrastructure to AWS, in order to mitigate the perceived risks of hosting their own infrastructure. They have enlisted your services to perform an assessment of their cloud infrastructure, starting with the external IP address provided.

Prerequisites

  • ✓Cloud infrastructure
  • ✓Linux OS
  • ✓Web and Network exploitation

Learning outcomes

  • ✓AWS enumeration
  • ✓Exploitation of serverless applications
  • ✓Exploiting misconfigurations
  • ✓Lateral movement
  • ✓Local privilege escalation
  • ✓Mitigation and best practices
  • ✓Web application and API exploitation
Blacksky Blizzard lab avatar
HTB CLOUD LAB

Blacksky Blizzard (GCP)

DIFFICULTY Medium
RESOURCES 9
FLAGS 15
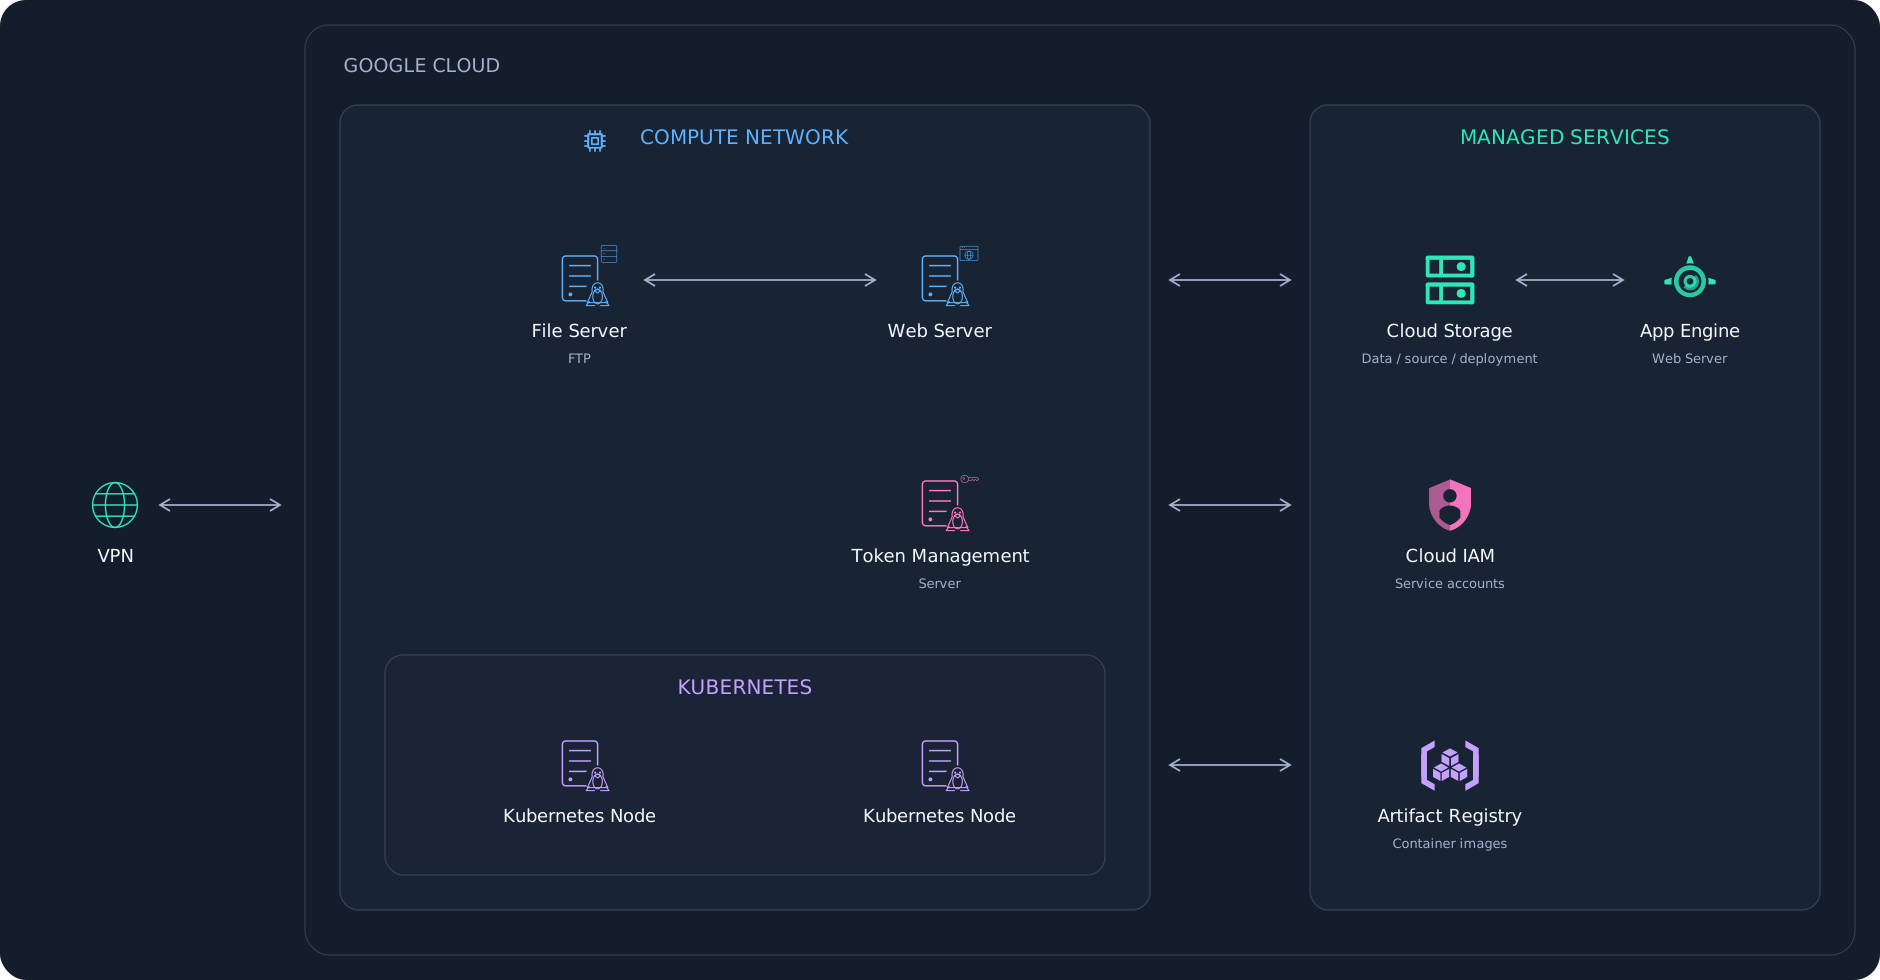
NETWORK TOPOLOGY LAB ENVIRONMENT
Blacksky Blizzard lab network topology diagram
ABOUT THE LAB

BlackSky Hailstorm is a cloud penetration testing labs that features a wide-range of misconfigurations, common privilege escalation techniques, and attack paths seen in real engagements in GCP. It covers how to exploit the vulnerabilities, and importantly, how they can be mitigated.

THE SCENARIO

Mega Multinational is a global leader in the Freight Logistics industry. They are not cloud native, but are looking to transition more infrastructure to GCP, in order to mitigate the perceived risks of hosting their own infrastructure. They have enlisted your services to perform an assessment of their cloud infrastructure, starting with the external IP address provided.

Prerequisites

  • ✓Cloud infrastructure
  • ✓Linux OS
  • ✓Web and Network exploitation

Learning outcomes

  • ✓GCP enumeration
  • ✓Exploitation of serverless applications
  • ✓Exploiting misconfigurations
  • ✓Lateral movement
  • ✓Local privilege escalation
  • ✓Mitigation and best practices
  • ✓Web application and API exploitation
Blacksky Cyclone lab avatar
HTB CLOUD LAB

Blacksky Cyclone (Azure)

DIFFICULTY Medium
RESOURCES 17
FLAGS 15
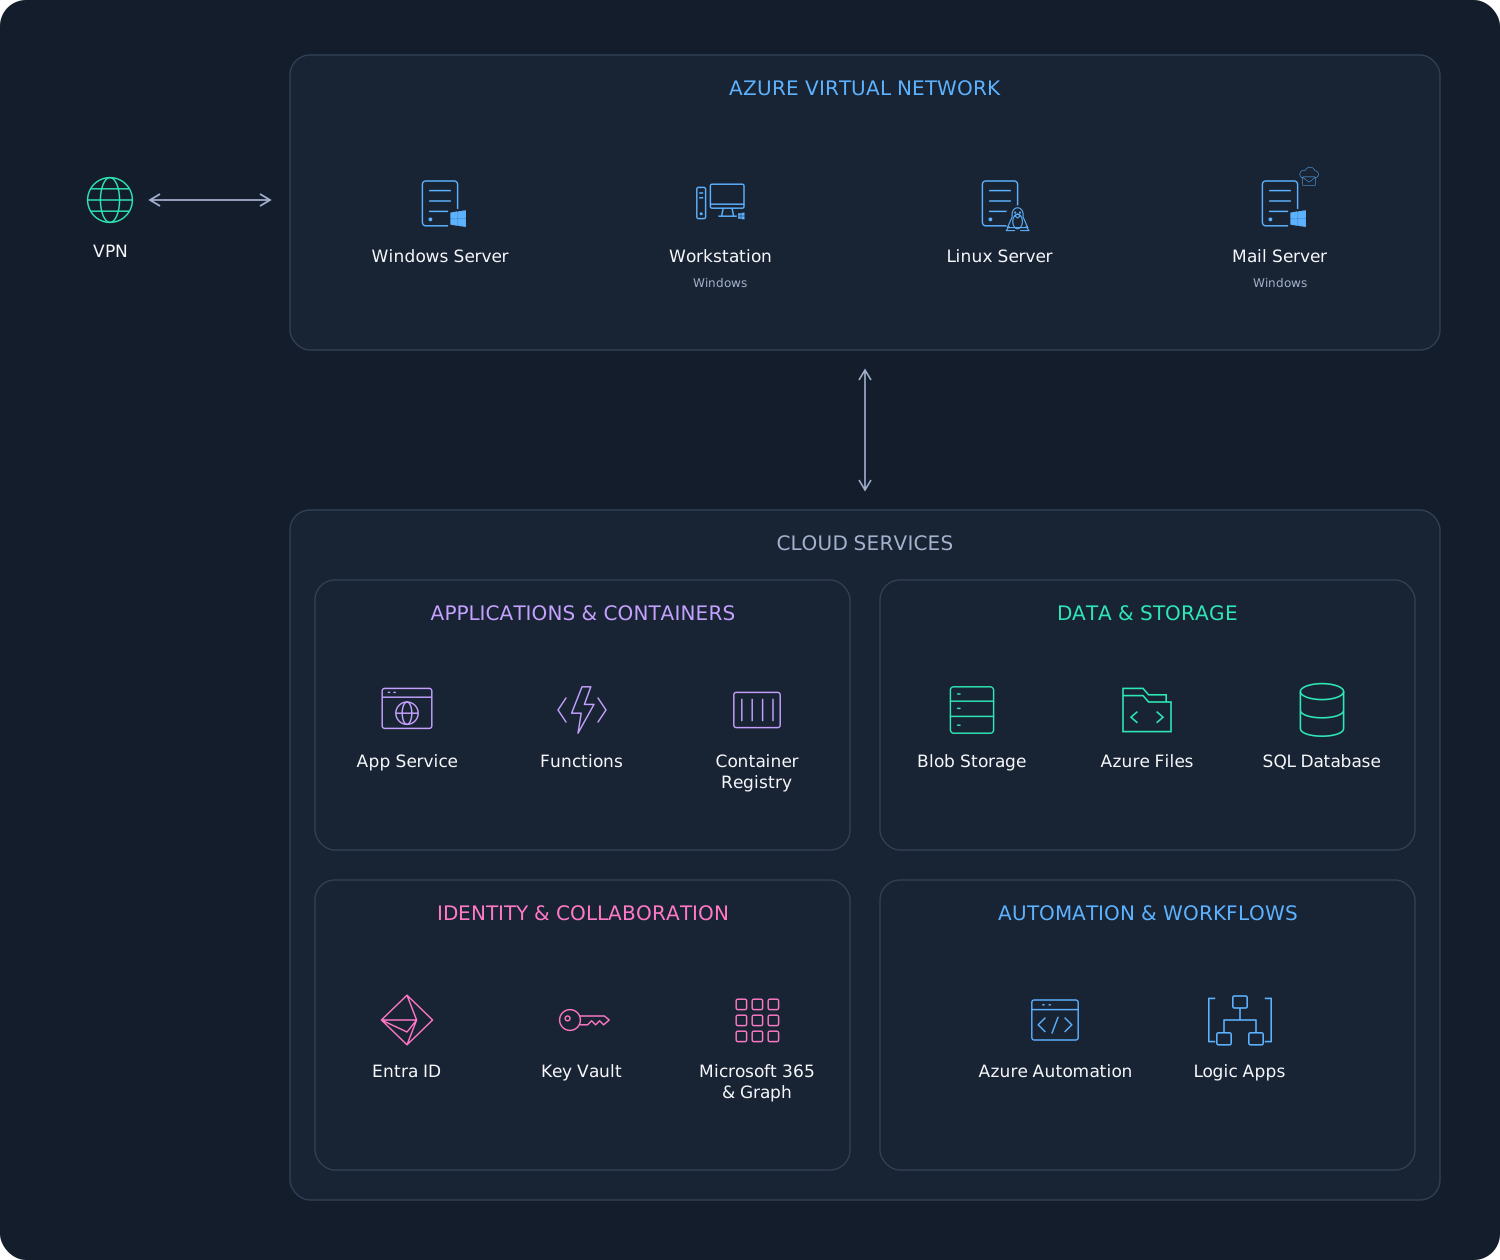
NETWORK TOPOLOGY LAB ENVIRONMENT
Blacksky Cyclone lab network topology diagram
ABOUT THE LAB

BlackSky Hailstorm is a cloud penetration testing labs that features a wide-range of misconfigurations, common privilege escalation techniques, and attack paths seen in real engagements in Azure. It covers how to exploit the vulnerabilities, and importantly, how they can be mitigated.

THE SCENARIO

Mega Multinational is a global leader in the Freight Logistics industry. They are not cloud native, but are looking to transition more infrastructure to Azure, in order to mitigate the perceived risks of hosting their own infrastructure. They have enlisted your services to perform an assessment of their cloud infrastructure, starting with the external IP address provided.

Prerequisites

  • ✓Cloud infrastructure
  • ✓Windows OS
  • ✓Scripting knowledge

Learning outcomes

  • ✓Azure enumeration
  • ✓Exploitation of serverless applications
  • ✓Exploiting misconfigurations
  • ✓Lateral movement
  • ✓Local privilege escalation
  • ✓Mitigation and best practices
  • ✓Web application and API exploitation
  • ✓Phishing
Altairus lab avatar
HTB CLOUD LAB

Altairus (Azure)

DIFFICULTY Hard
RESOURCES 12
FLAGS 15
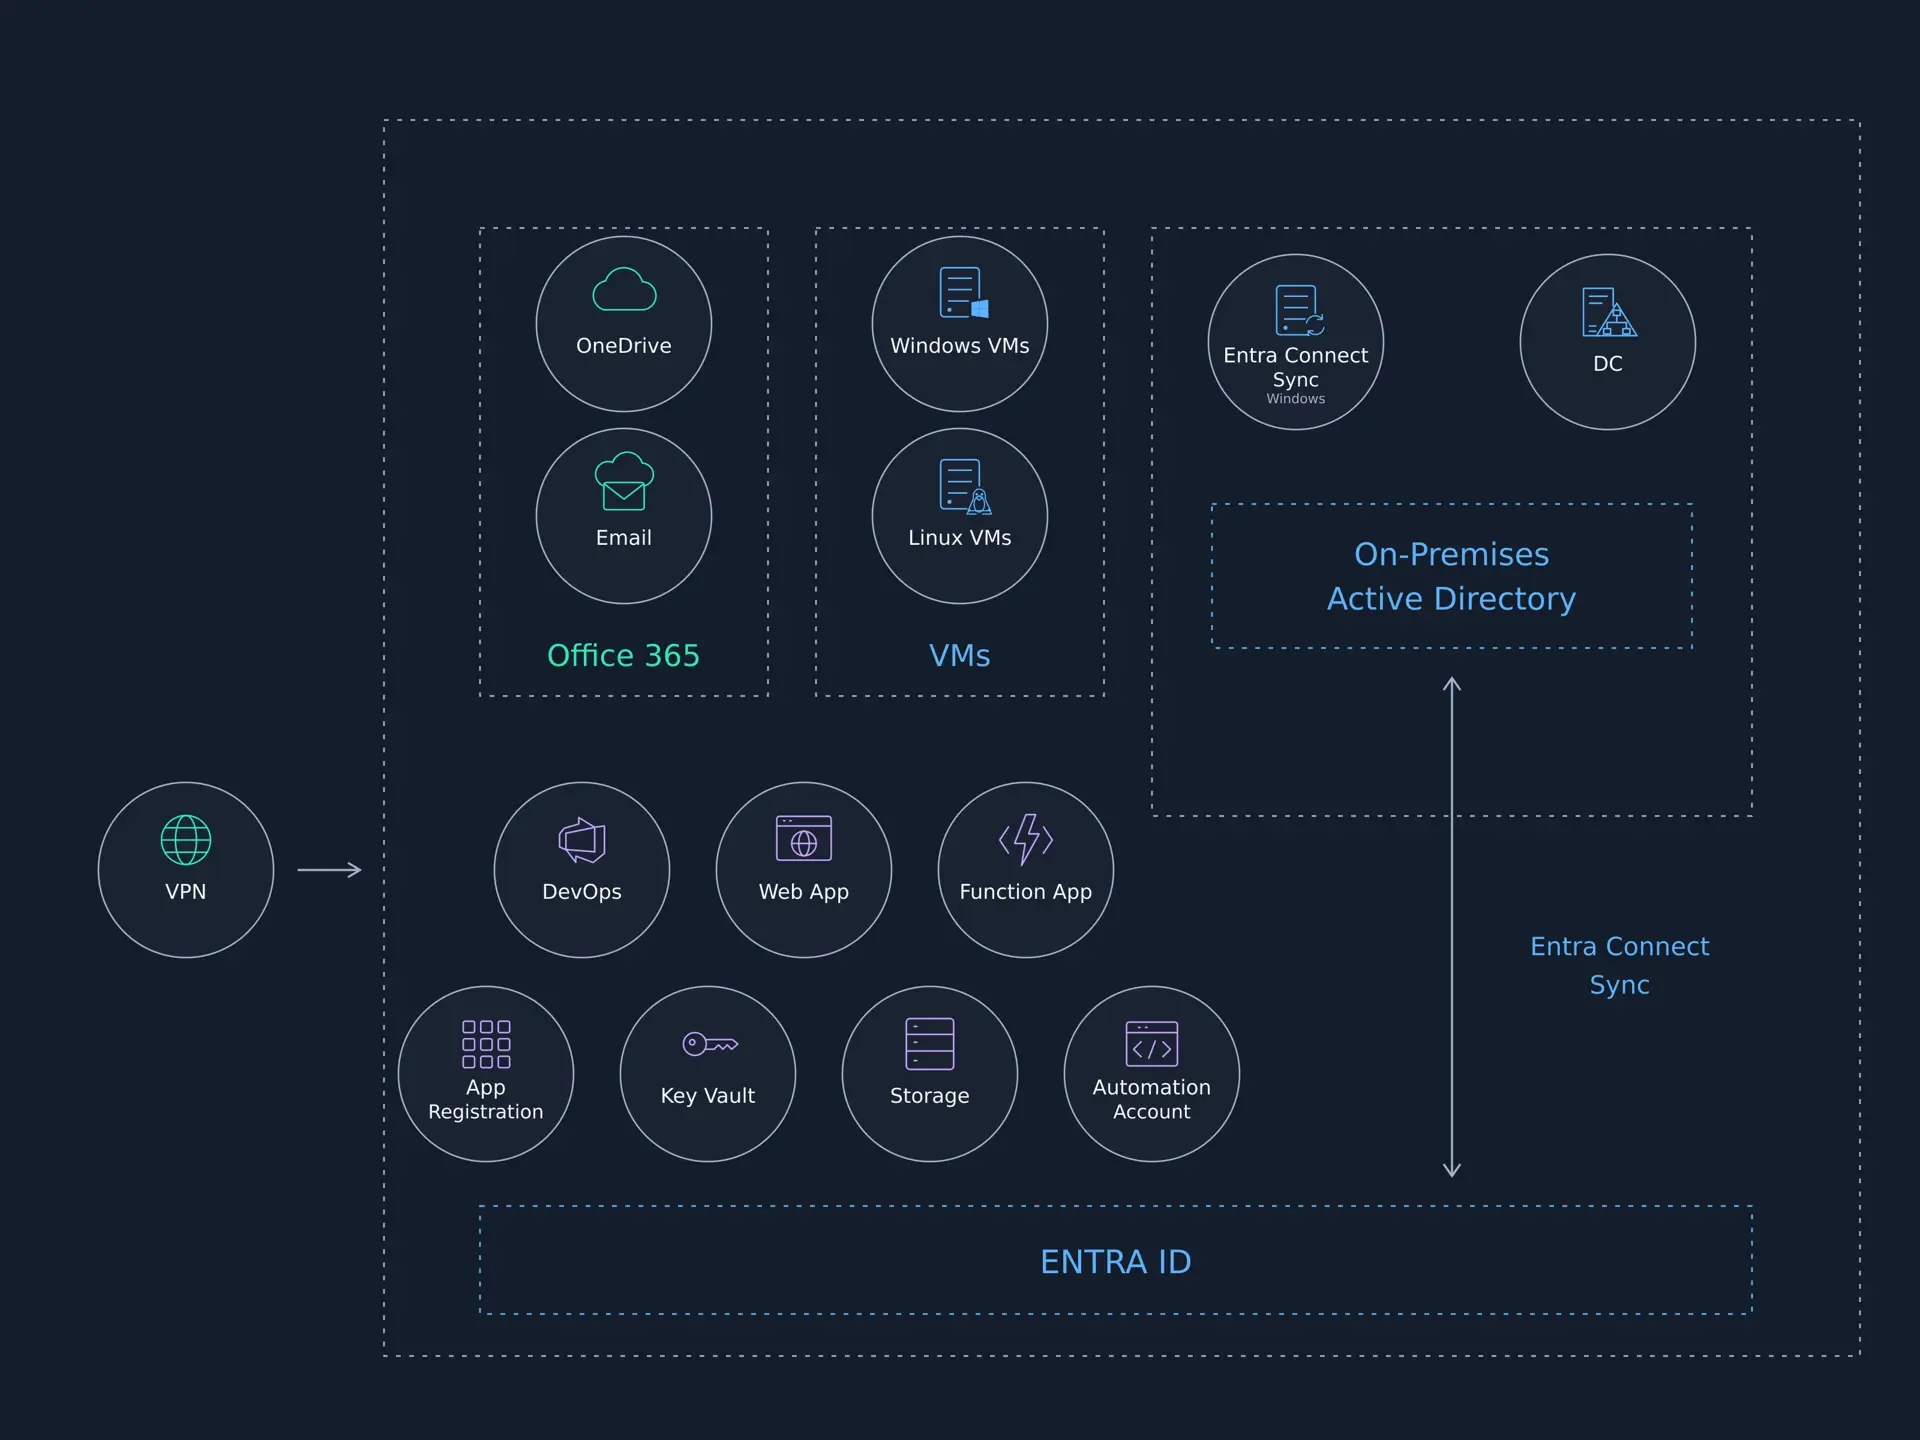
NETWORK TOPOLOGY LAB ENVIRONMENT
Altairus lab network topology diagram
ABOUT THE LAB

Altairus is an advanced red team simulation focused on compromising a hybrid Microsoft Azure environment. The goal is to progress through a multi-stage attack chain spanning 15 objectives, moving between cloud and on-premises infrastructure while exploiting weaknesses in identity, access controls, and trust relationships.

THE SCENARIO

Omni Multinational is a global leader in the Trade Management sector with a mature, cloud-first infrastructure built on Microsoft Azure. Following concerns around identity hygiene, secret management, and the trust boundaries between its Azure and on-premises AD, Omni has hired you to conduct a black-box security assessment of the omnimultinational.com infrastructure. Your task is to explore the environment, pivot across trust boundaries, and ultimately attempt to compromise all Omni Multinational entities.

Prerequisites

  • ✓Microsoft, Azure, Entra ID, and Azure BRAC
  • ✓Service principals, managed identities, and application registrations
  • ✓AD and Kerberos
  • ✓OAuth 2.o flows
  • ✓Powershell, the Az and Microsoft Graph modules, and the Azure Rest APIs

Learning outcomes

  • ✓Azure enumeration
  • ✓Cloud identity and access management
  • ✓Authentication & credential security
  • ✓Cloud application and serverless security
  • ✓Secrets and data protection
  • ✓Azure automation and DevOps security
  • ✓Hybrid identity and AD security
  • ✓Privilege escalation & Lateral movement
  • ✓Phishing and social engineering
  • ✓Exploiting misconfigurations
  • ✓Mitigations and best practices
Ymir lab avatar
HTB CLOUD LAB

Ymir (GCP)

DIFFICULTY Hard
RESOURCES 14
FLAGS 14
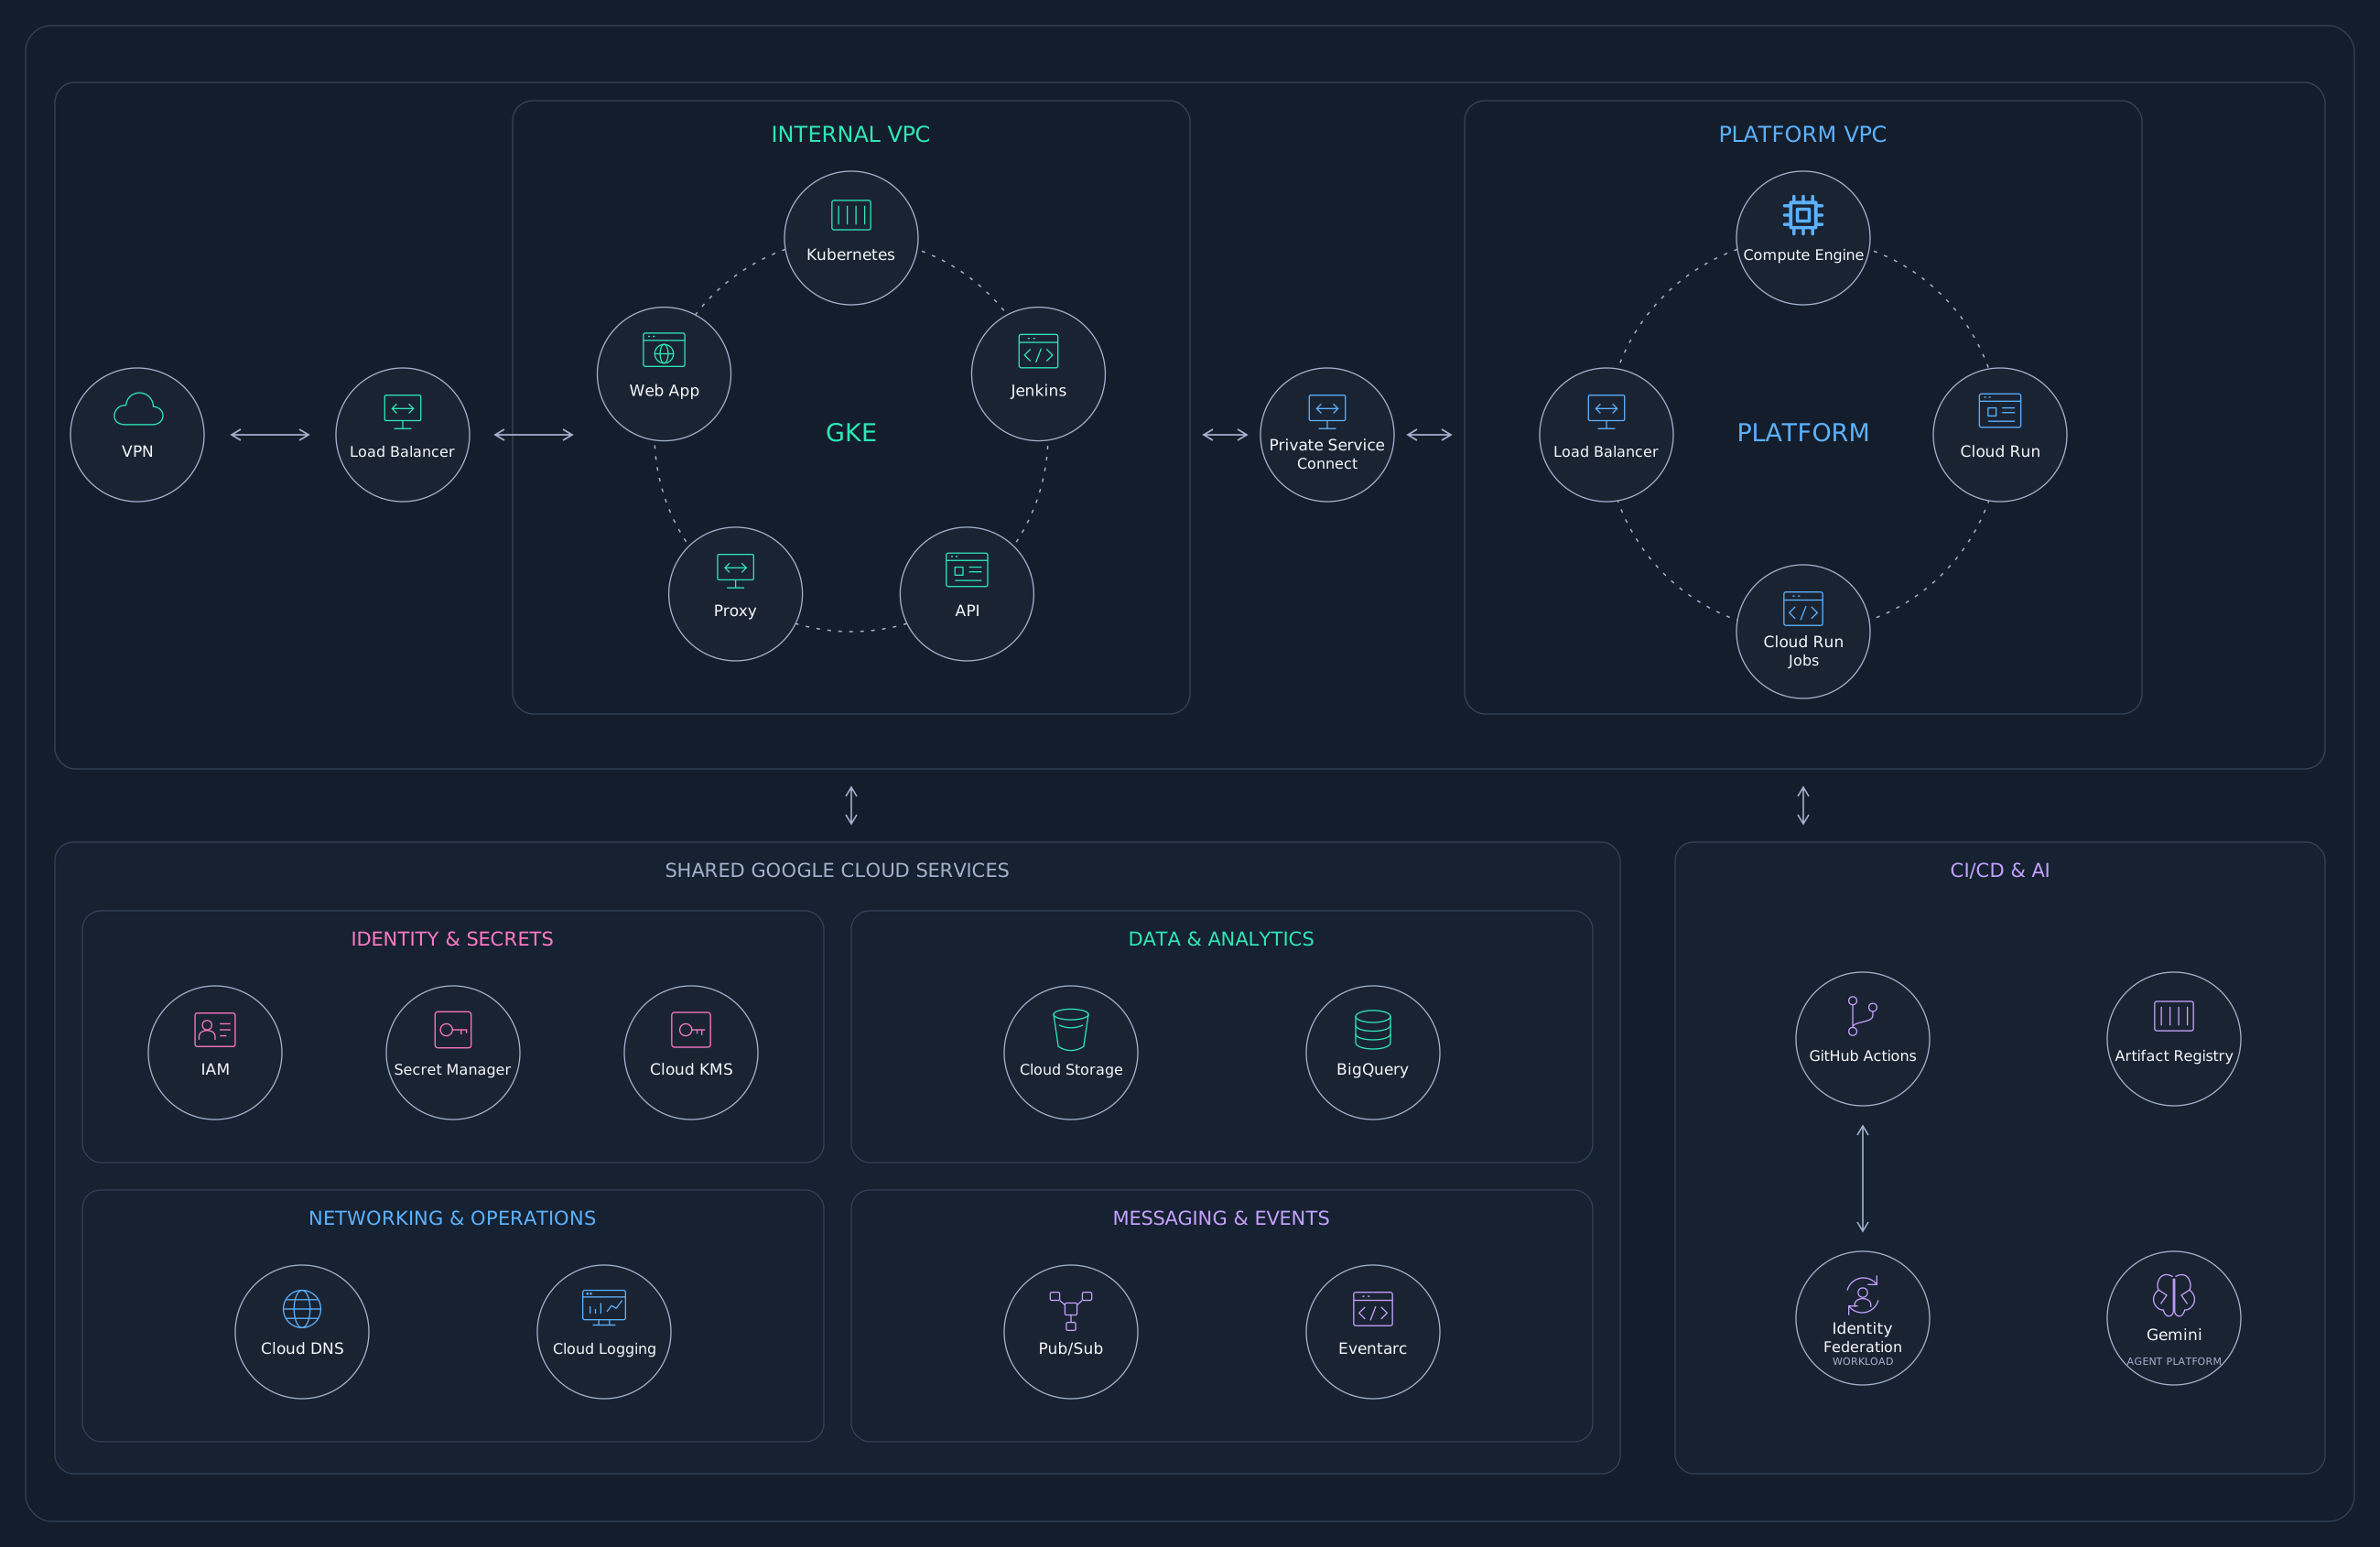
NETWORK TOPOLOGY LAB ENVIRONMENT
Ymir lab network topology diagram
ABOUT THE LAB

Ymir is an advanced red team simulation set in a Google Cloud environment. Players navigate interconnected cloud services, identify misconfigurations and security weaknesses, and chain multiple attacks to gain deeper access. Designed to reflect real-world cloud engagements, the lab challenges players to apply advanced cloud attack techniques across multi-stage exploitation paths.

THE SCENARIO

Omni Multinational is a global trade management company that has migrated core services and automation to Google Cloud. As part of an adversary-emulation assessment, your mission is to identify and chain vulnerabilities that could allow an external attacker to access Omni’s proprietary trading algorithms and expose its critical intellectual property.

Prerequisites

  • ✓Cloud infrastructure and Google cloud concepts
  • ✓Linux OS
  • ✓Web application and API security fundamentals
  • ✓Identity and access management concepts
  • ✓Scripting
  • ✓Containerization & Kubernetes
  • ✓Reverse engineering concepts
  • ✓Source code and CI/CD workflows

Learning outcomes

  • ✓GCP enumeration
  • ✓Cloud misconfiguration exploitation
  • ✓GCP IAM & identity abuse
  • ✓GKE / Kubernetes exploitation in cloud environments
  • ✓Workload identity & federation security
  • ✓Serverless & managed runtime exploitation
  • ✓Event-driven architecture attacks
  • ✓Web application & API exploitation
  • ✓JWT/Token boundary attacks
  • ✓Software supply chain and artifact trust bypass
  • ✓Cloud cryptography and signing-oracles
  • ✓Cloud logging, monitoring & detection blind spots
  • ✓Data-plane exploitation
  • ✓AI agent platform & MLOps security concepts
  • ✓Network boundary bypass in GCP
Atlas lab avatar
HTB CLOUD LAB

Atlas (AWS)

DIFFICULTY Hard
RESOURCES 17
FLAGS 16
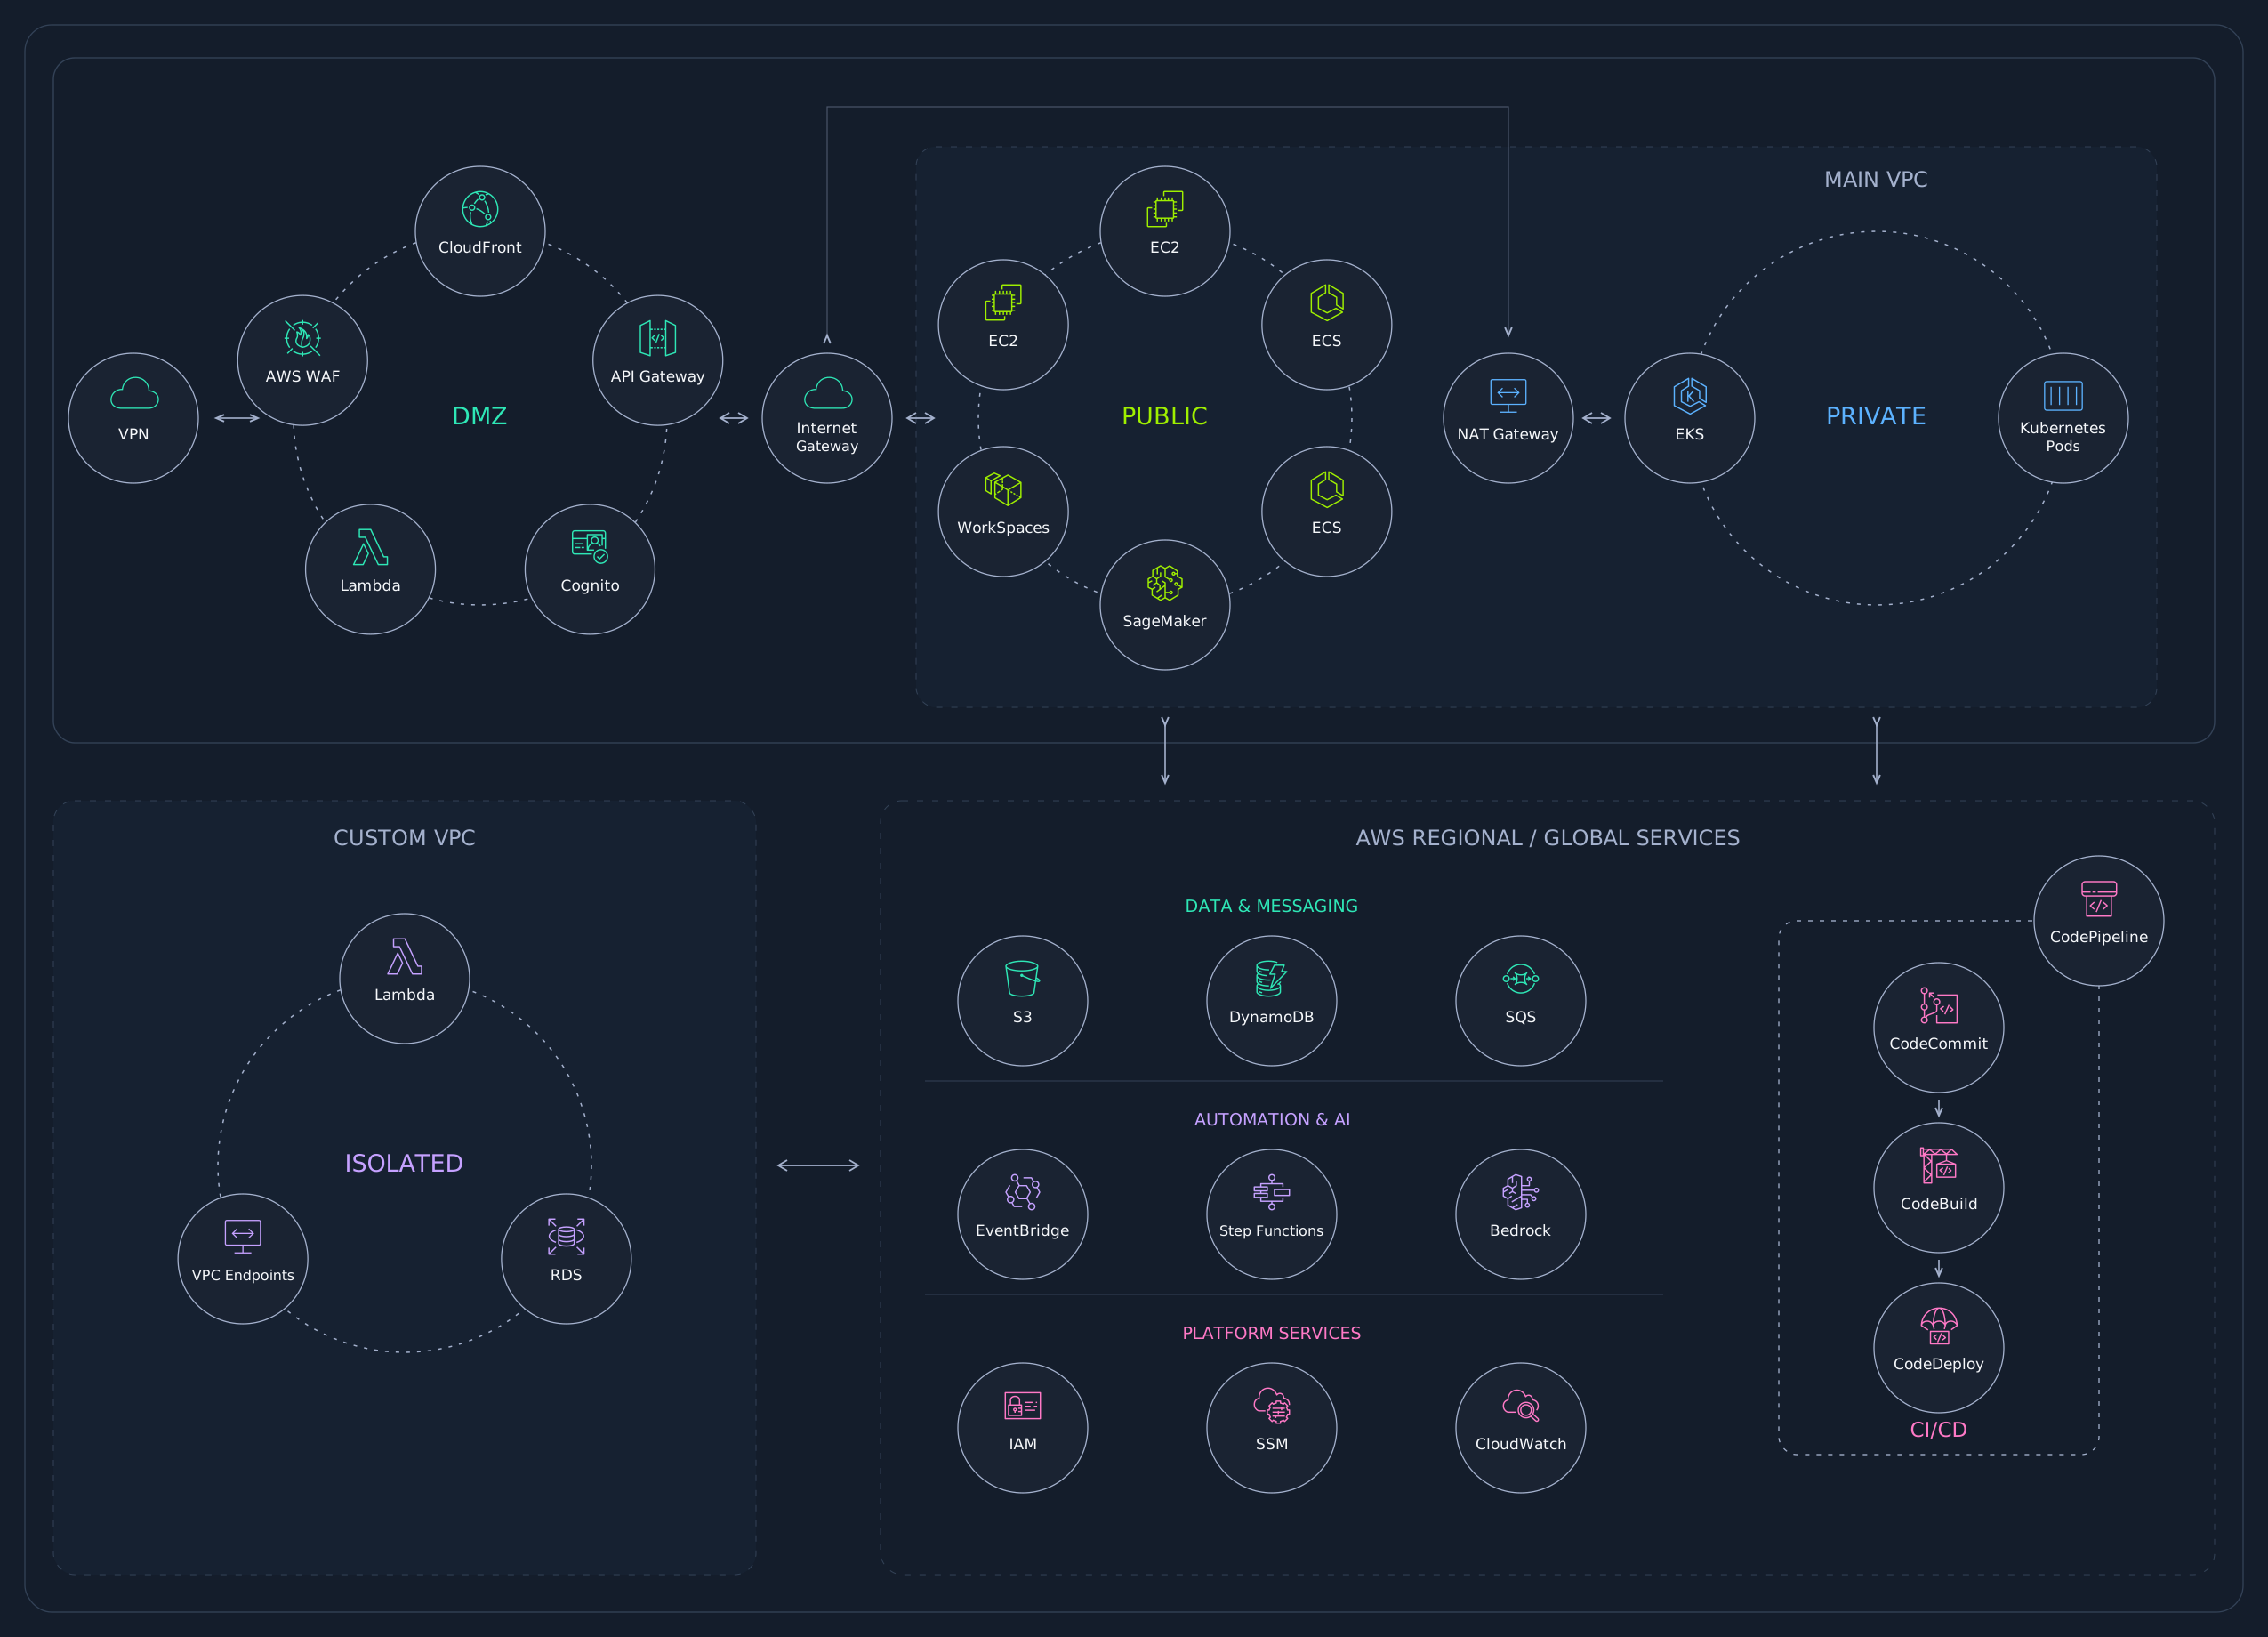
NETWORK TOPOLOGY LAB ENVIRONMENT
Atlas lab network topology diagram
ABOUT THE LAB

Atlas is an advanced red team simulation set in an Amazon Web Services (AWS) environment. Players navigate interconnected AWS services, identify misconfigurations and security weaknesses, and chain multiple attacks to gain deeper access. Designed to reflect real-world cloud engagements, the lab challenges players to apply advanced cloud attack techniques across multi-stage exploitation paths.

THE SCENARIO

Omni Multinational is a global trade management company that relies on AWS to support its growing digital operations. Your mission is to assess its cloud environment from an external attacker’s perspective, identifying exposed services, misconfigurations, and privilege escalation paths that could lead to deeper access.

Prerequisites

  • ✓Cloud infrastructure and AWS concepts
  • ✓Windows/Linux OS
  • ✓Web application and API security fundamentals
  • ✓Identity and access management concepts
  • ✓Containerization & Kubernetes
  • ✓Source code and CI/CD workflows

Learning outcomes

  • ✓AWS enumeration
  • ✓Cloud misconfiguration exploitation
  • ✓Cloud identity & access management abuse
  • ✓Serverless application exploitation
  • ✓AI & LLM security
  • ✓MLOps security
  • ✓Web application & API exploitation
  • ✓Software supply chain attacks
  • ✓Container and Kubernetes exploitation
  • ✓Cloud forensics
  • ✓AD exploitation
  • ✓Hybrid cloud attack paths