HTB PROFESSIONAL LABS

Professional Labs Directory

Explore HTB’s collection of Professional Labs, discover what each scenario offers, and find the right ones to develop and assess your team's cybersecurity skills.

Hard Professional Labs

Progress in offensive tradecraft through advanced Active Directory attacks, lateral movement, persistence, and post-exploitation in sophisticated enterprise environments. Designed for experienced penetration testers, these labs focus on advanced Red Team TTPs, custom exploitation, and abuse of complex infrastructure such as SCCM, SCOM, and PKI.

Cybernetics lab avatar
HTB PRO LAB

Cybernetics

DIFFICULTY Hard
MACHINES 23
FLAGS 20
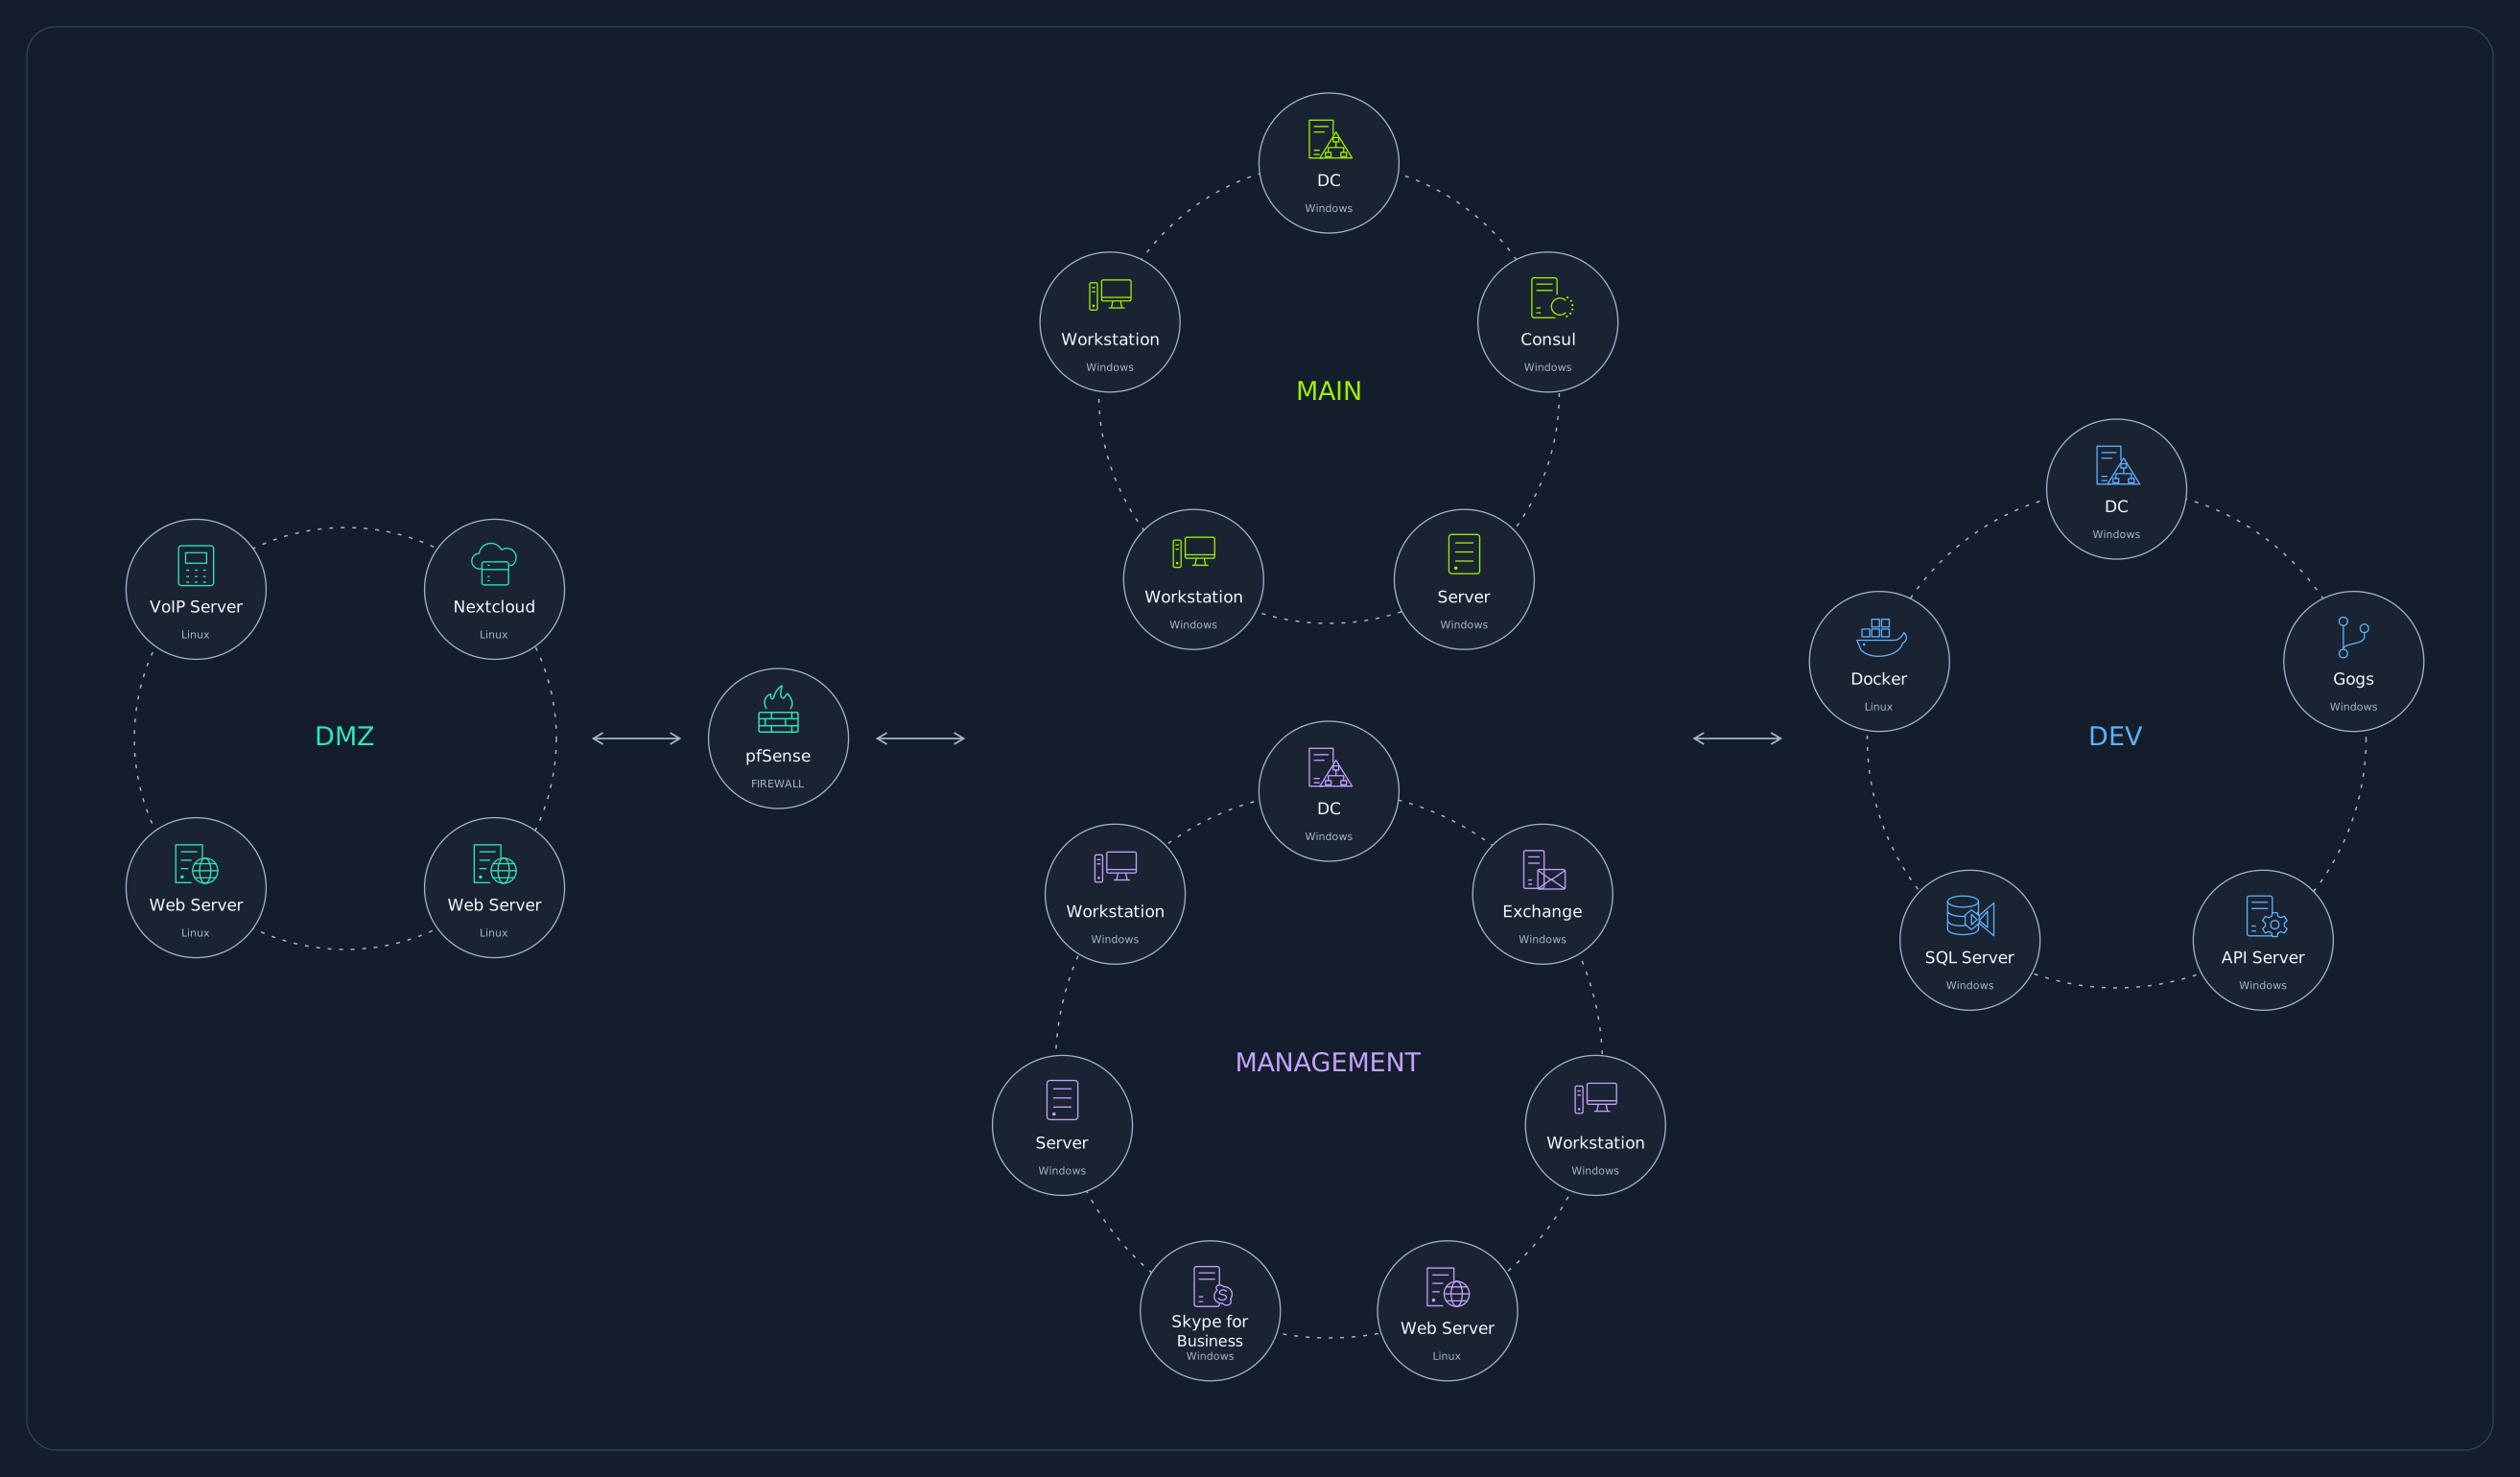
NETWORK TOPOLOGY LAB ENVIRONMENT
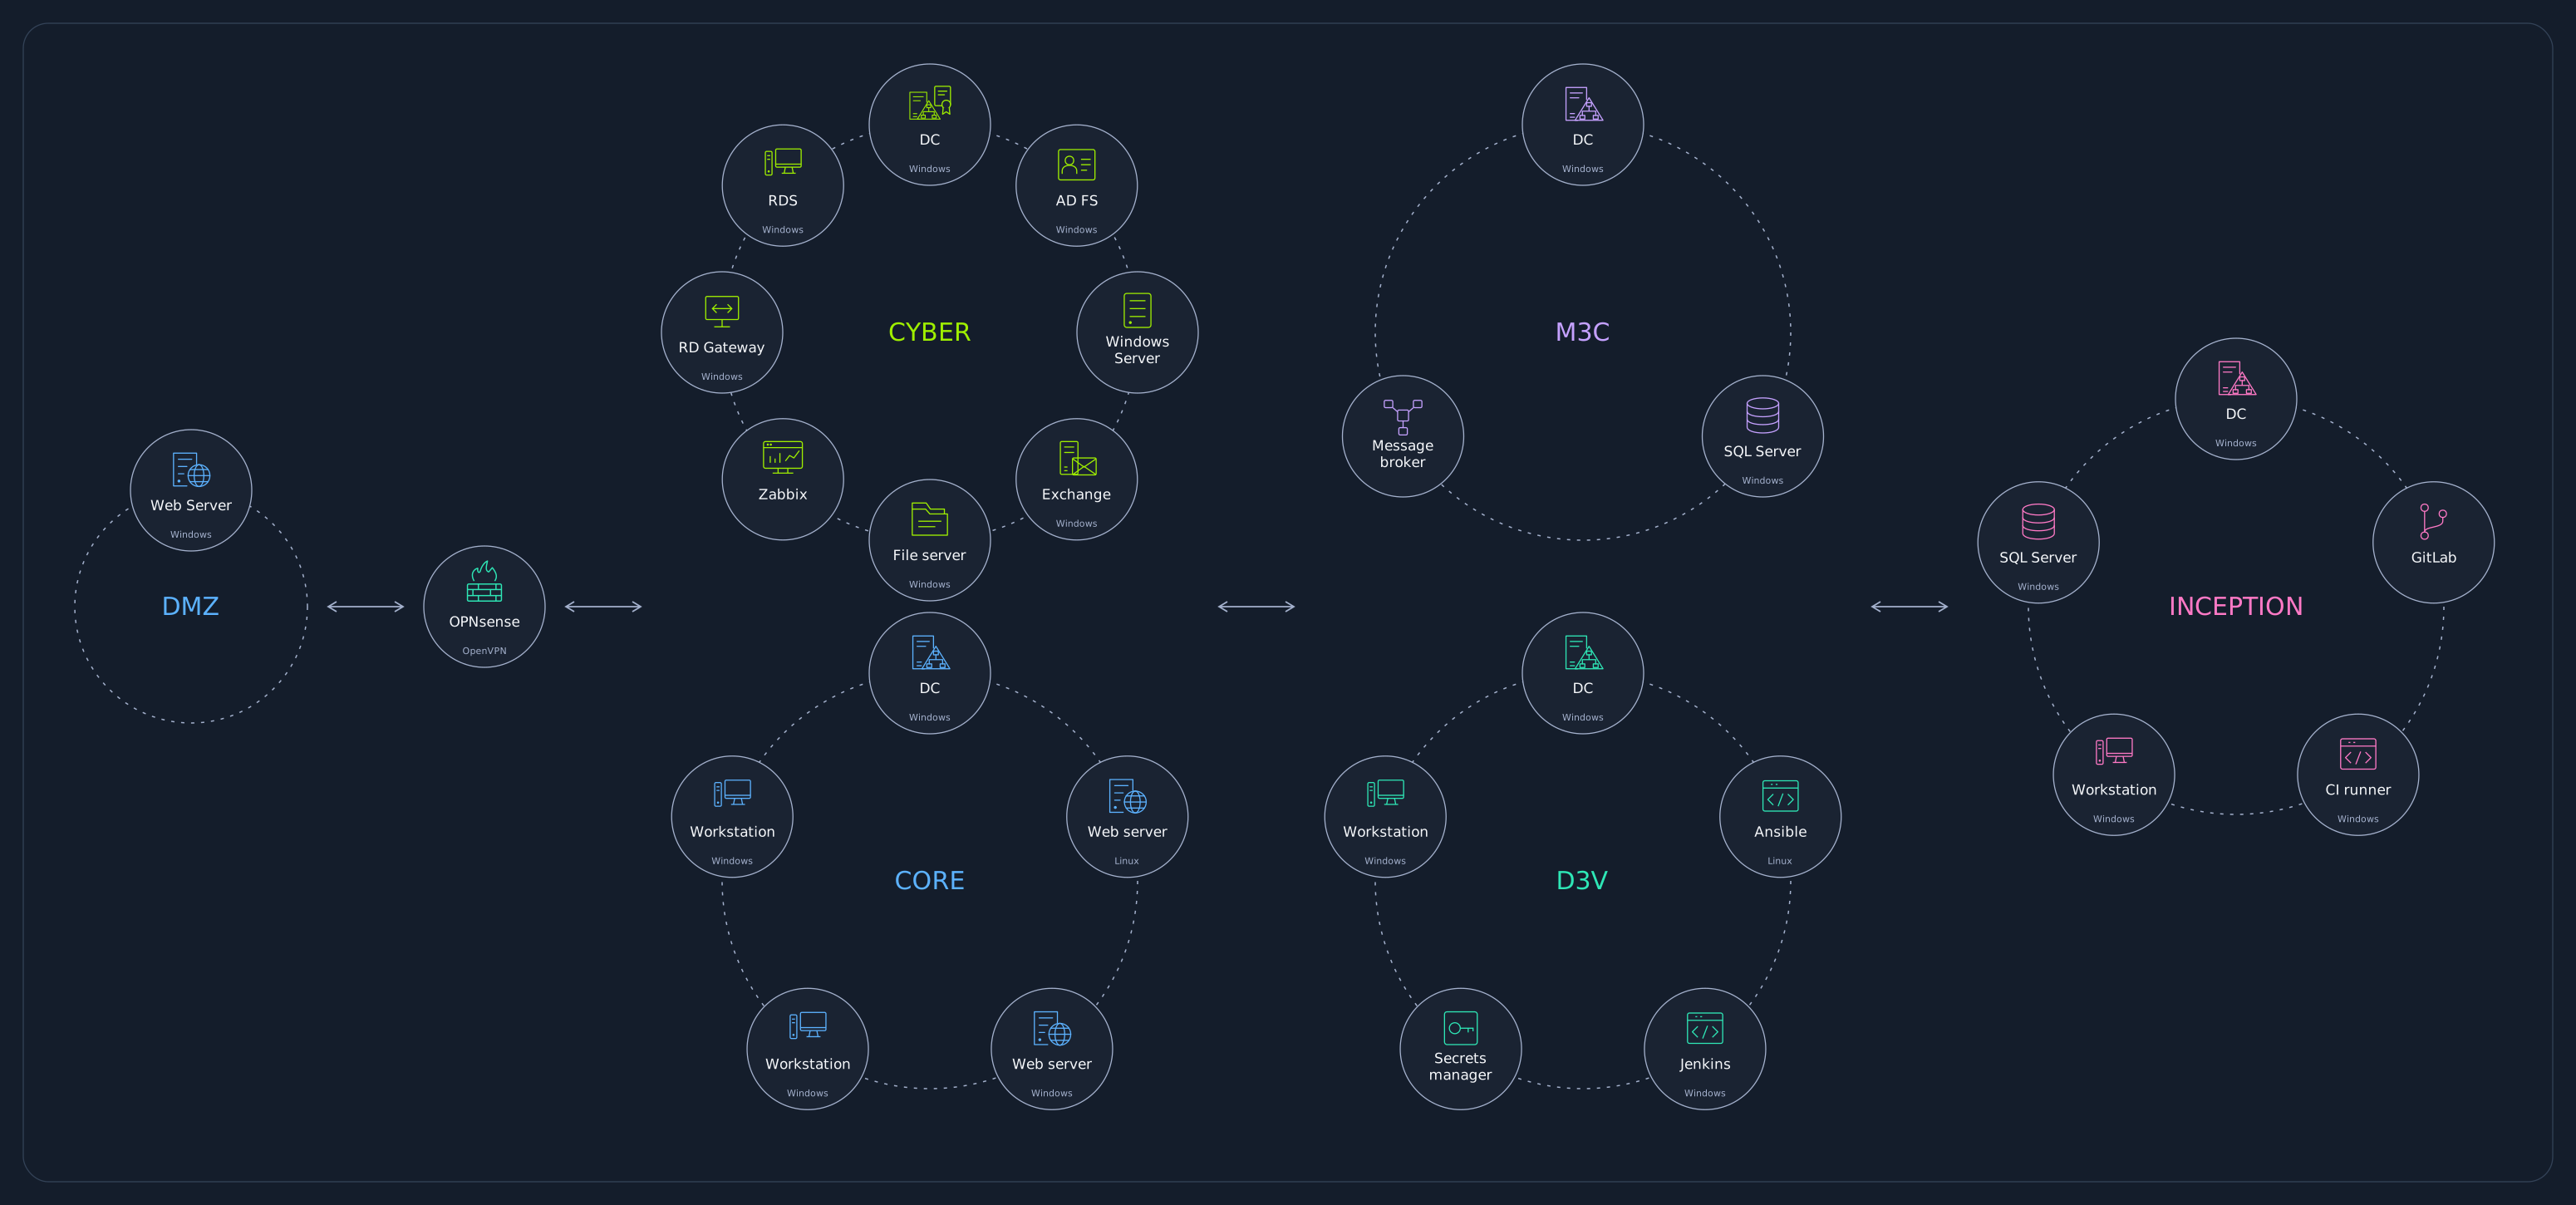
Cybernetics lab network topology diagram
ABOUT THE LAB

Cybernetics is designed to simulate a real-life corporate environment, based heavily on Microsoft Windows systems. Elements include Active Directory (with a Server 2016 functional domain level), Exchange, Internet Information Services, and SQL Server. Machines are also segregated across multiple subnets.

THE SCENARIO

Cybernetics have gone through multiple pentest engagements, iteratively hardening their environment each time, and therefore have a more mature security posture. Many protection technologies are present and the modern operating systems are fully updated. The goal of this challenging lab is to gain a foothold, elevate privileges, establish persistence and move laterally, in order to reach the goal of domain admin.

Prerequisites

  • ✓AD penetration testing
  • ✓Microsoft infrastructure design concepts
  • ✓Microsoft security controls
  • ✓Public Key Infrastructure (PKI)
  • ✓DevOPS CI/CD

Learning outcomes

  • ✓Advanced phishing techniques
  • ✓AD enumeration and exploitation
  • ✓DevOPS security controls
  • ✓Evading endpoint protections
  • ✓Lateral movement
  • ✓Local privilege escalation
Breakpoint lab avatar
HTB PRO LAB

Breakpoint

DIFFICULTY Hard
MACHINES 22
FLAGS 20
NETWORK TOPOLOGY LAB ENVIRONMENT
Breakpoint lab network topology diagram
ABOUT THE LAB

Breakpoint is a red team simulation environment, designed to be attacked as a means of learning and honing your engagement skills.

THE SCENARIO

Breakpoint focuses on a software development startup, who take security seriously. They have enlisted your services to perform a red team assessment of their environment. The goal of this challenging lab is to gain a foothold, elevate privileges, establish persistence and move laterally, in order to reach the goal of domain admin.

Prerequisites

  • ✓Assess AD environments
  • ✓Microsoft infrastructure design concepts
  • ✓Microsoft security controls
  • ✓Common administrative configurations
  • ✓Development tools & workflows

Learning outcomes

  • ✓AD enumeration and exploitation
  • ✓Code review
  • ✓Evading endpoint protections
  • ✓Lateral movement
  • ✓Local privilege escalation
  • ✓Phishing techniques
  • ✓VoIP exploitation
Mythical lab avatar
HTB MINI PRO LAB

Mythical

DIFFICULTY Hard
MACHINES 3
FLAGS 3
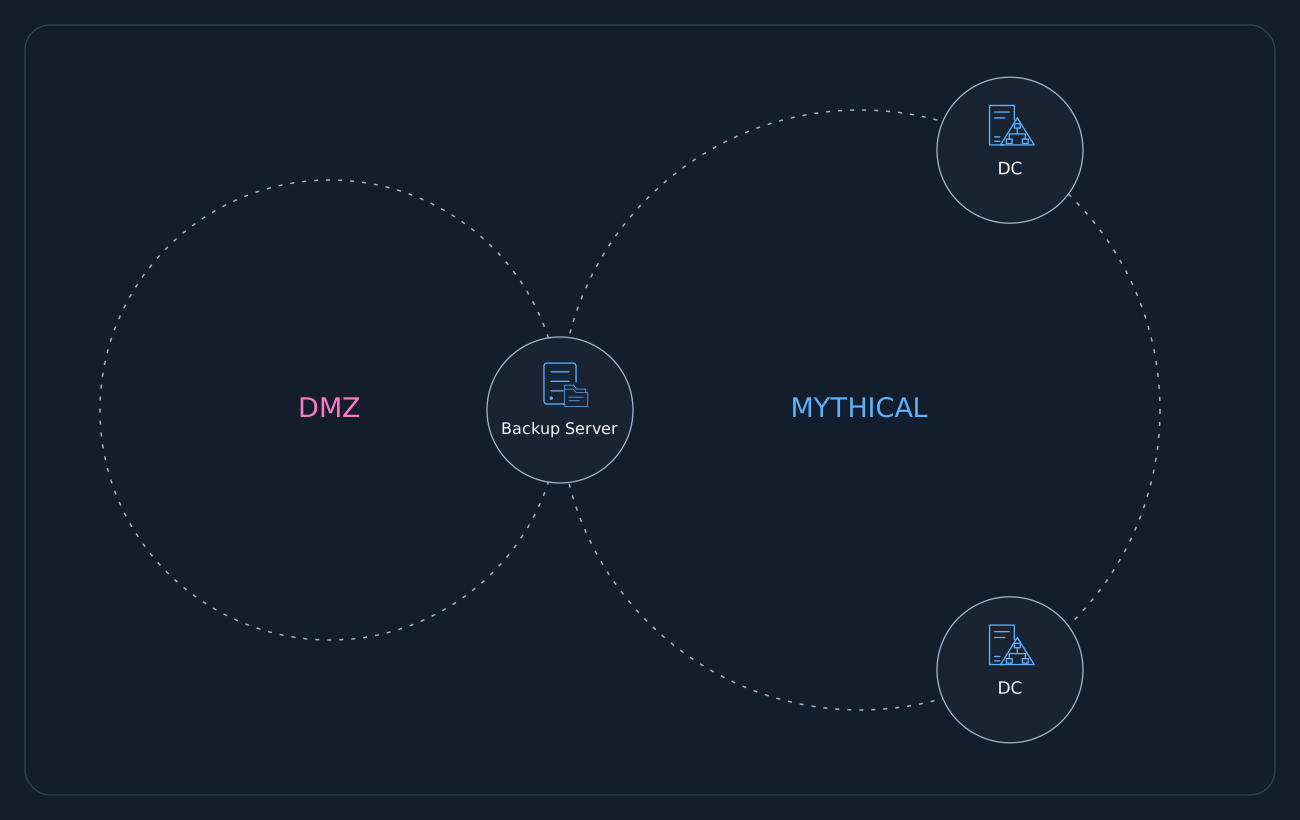
NETWORK TOPOLOGY LAB ENVIRONMENT
Mythical lab network topology diagram
ABOUT THE LAB

Mythical simulates an assumed-breach scenario within a restricted AD environment. You begin with an active Mythic command and control (C2) beacon on an internal system and must navigate the network despite external network egress being blocked. The goal is to exploit trust relationships, abuse Active Directory Certificate Services (AD CS), and leverage Microsoft SQL Server (MSSQL) to escalate privileges and ultimately achieve full domain compromise.

THE SCENARIO

You are tasked with performing a red team engagement on Mythical Inc. The company does not allow data to leave the internal network, so a C2 server has been set up internally, and an employee executed a payload in order to simulate a successful social engineering attack.

Prerequisites

  • ✓Penetration testing methods
  • ✓AD
  • ✓C2

Learning outcomes

  • ✓Enumeration
  • ✓AD enumeration and attacks
  • ✓AD Certificate Services
  • ✓Lateral movement
  • ✓Local privilege escalation
  • ✓MSSQL attacks
  • ✓C2 Operations
Vigilant lab avatar
HTB MINI PRO LAB

Vigilant

DIFFICULTY Hard
MACHINES 2
FLAGS 2
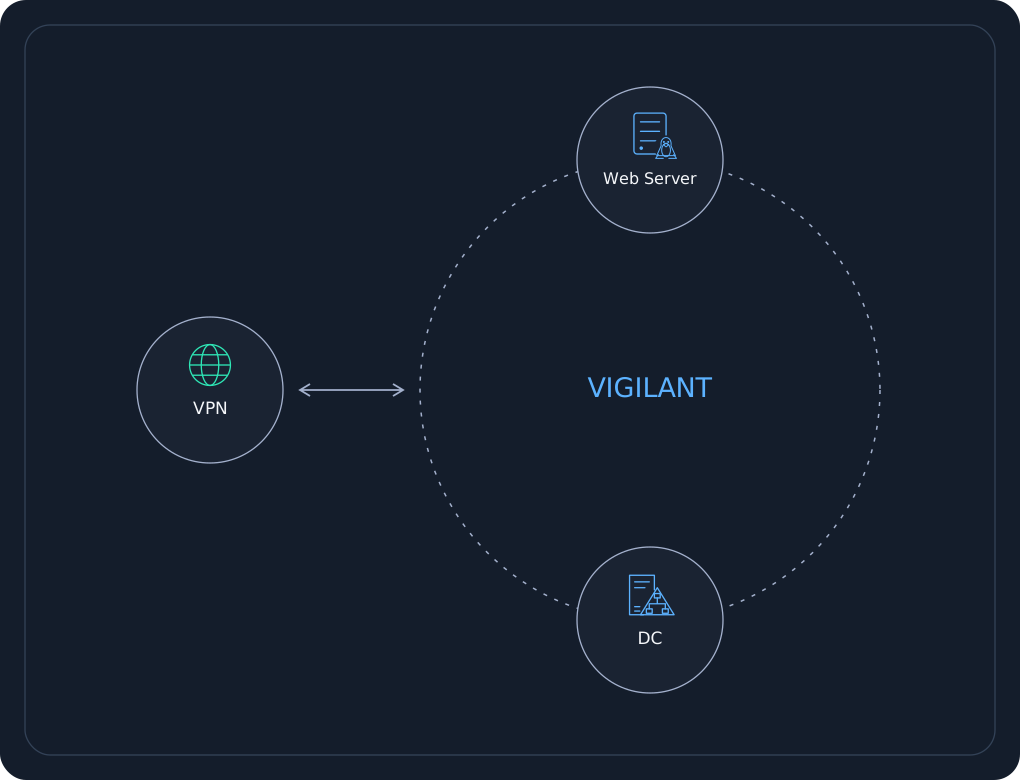
NETWORK TOPOLOGY LAB ENVIRONMENT
Vigilant lab network topology diagram
ABOUT THE LAB

Vigilant is an advanced-level AD attack chain designed to evaluate penetration testing capabilities in hybrid Windows-Linux environments. The goal is to compromise the domain from a position of no initial access by systematically enumerating the environment, escalating privileges, and ultimately obtaining Domain Administrator access.

THE SCENARIO

This penetration testing engagement simulates a comprehensive security assessment of Vigilant’s hybrid Active Directory infrastructure. The environment consists of a domain-joined Linux system and a Windows Domain Controller, presenting a realistic enterprise attack surface.

Prerequisites

  • ✓Penetration testing methods & frameworks
  • ✓Container technologies (Docker) and associated attack vectors
  • ✓AD concepts & security principles
  • ✓Authentication & privilege escalation techniques on domain-joined Linux systems
  • ✓ADCS exploitation methods
  • ✓DLL reverse engineering

Learning outcomes

  • ✓Enterprise enumeration & misconfiguration discovery
  • ✓Lateral movement techniques
  • ✓Container security & escape techniques
  • ✓Active Directory Certificate Services (ADCS) exploitation
  • ✓Custom DLL analysis & exploitation
  • ✓Domain-joined Linux system compromise
  • ✓Privilege escalation in hybrid environments
Argon lab avatar
HTB MINI PRO LAB

Argon

DIFFICULTY Hard
MACHINES 5
FLAGS 4
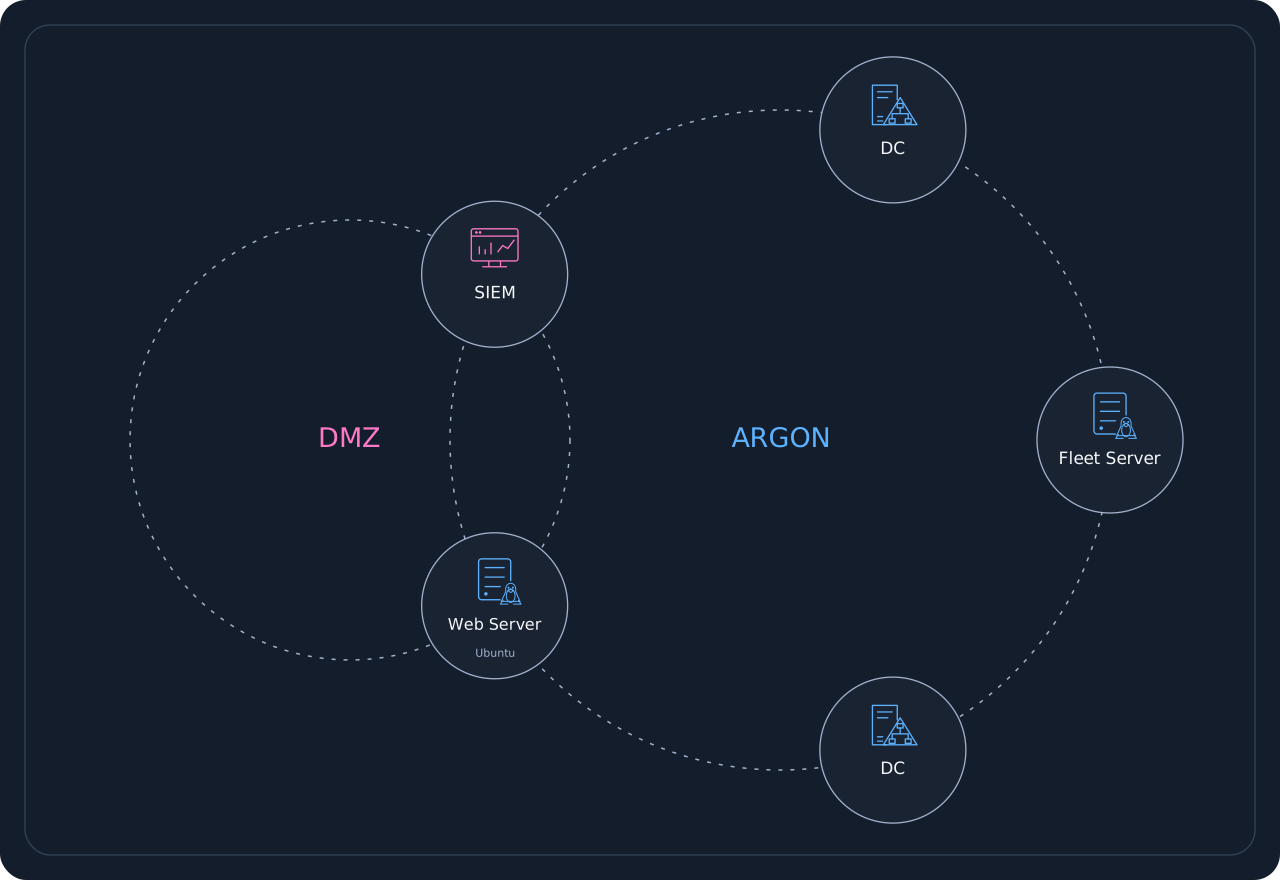
NETWORK TOPOLOGY LAB ENVIRONMENT
Argon lab network topology diagram
ABOUT THE LAB

Argon simulates a challenging AD environment that combines traditional enterprise infrastructure with maritime operational technologies. The goal is to assess both the external and internal networks of Argon, a global maritime cargo and vessel transportation company, explore the environment, pivot across trust boundaries, and evaluate the security of both its enterprise and maritime operational infrastructure.

THE SCENARIO

Argon is a global maritime cargo and vessel transportation company responsible for managing overseas shipping routes, port operations, and fleet logistics. As the organisation expanded, its infrastructure evolved into a hybrid environment combining AD based corporate systems with vessel tracking platforms and operational services used across international waters. The environment includes interconnected domains with trust relationships between shore offices and production systems, alongside web applications for cargo management and maritime coordination. You have been assigned to assess both the external and internal networks of Argon, explore the environment, pivot across trust boundaries, and evaluate the security of its enterprise and maritime operational infrastructure.

Prerequisites

  • ✓Penetration testing tools
  • ✓Windows/Linux OS
  • ✓Windows AD
  • ✓Maritime navigation protocols
  • ✓Web application penetration testing
  • ✓Injection techniques
  • ✓BloodHound usage

Learning outcomes

  • ✓Enumeration
  • ✓Basic injection attacks
  • ✓Maritime operation abuse & exploitation
  • ✓Lateral movement and crossing trust boundaries
  • ✓Privilege escalation
  • ✓Cross-forest abuse
Hades lab avatar
HTB MINI PRO LAB

Hades

DIFFICULTY Hard
MACHINES 3
FLAGS 7
NETWORK TOPOLOGY LAB ENVIRONMENT
Hades lab network topology diagram
ABOUT THE LAB

Hades is designed to test your skills in AD enumeration, lateral movement, and privilege escalation within a small enterprise network. The goal is to gain a foothold on the internal network, escalate privileges, and ultimately compromise the domain, collecting several flags along the way.

THE SCENARIO

Gigantic Hosting is a leading website hosting and SSL certificate provider. Concerned about potential breaches, they have hired a penetration testing firm to assess their security.

Prerequisites

  • ✓Penetration testing methods
  • ✓Linux/Windows OS
  • ✓AD
  • ✓Web application attacks

Learning outcomes

  • ✓Enumeration
  • ✓AD enumeration and attacks
  • ✓Lateral movement
  • ✓Network pivoting
  • ✓Privilege escalation
  • ✓Web application attacks
  • ✓Password cracking
  • ✓Disc backup forensics
  • ✓Network sniffing
RPG lab avatar
HTB MINI PRO LAB

RPG

DIFFICULTY Hard
MACHINES 4
FLAGS 6
NETWORK TOPOLOGY LAB ENVIRONMENT
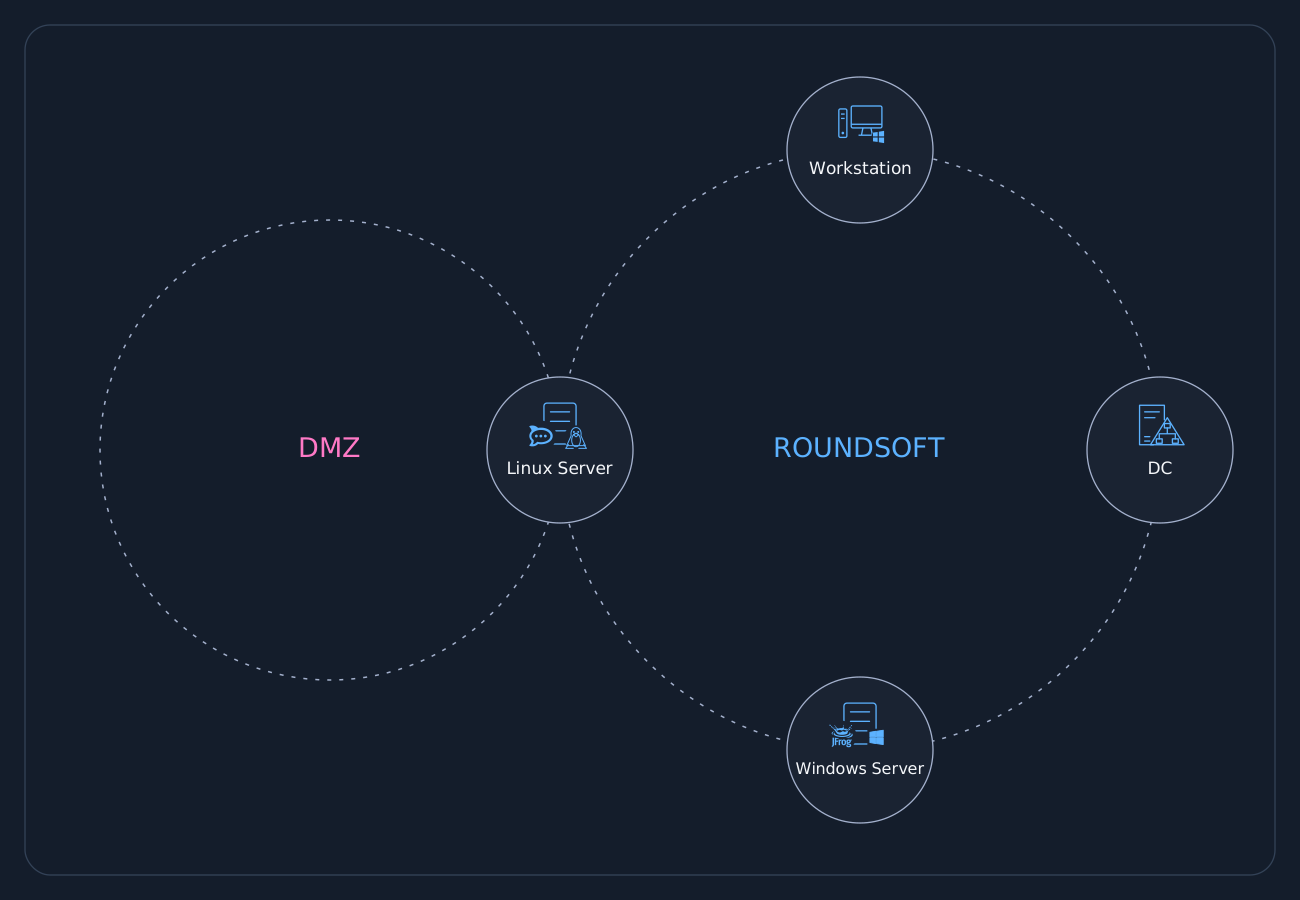
RPG lab network topology diagram
ABOUT THE LAB

RPG is designed to test your skills in Active Directory enumeration, lateral movement, and privilege escalation within a small enterprise network. The goal is to gain a foothold, escalate privileges, and compromise the domain while collecting several flags along the way.

THE SCENARIO

Roundsoft, Inc., a startup developing video games, has hired a penetration testing firm to determine whether their perimeter can be breached, leading to a compromise of their domain.

Prerequisites

  • ✓Penetration testing methods
  • ✓Linux/Windows OS
  • ✓AD
  • ✓Web application attacks

Learning outcomes

  • ✓Enumeration
  • ✓Web application attacks
  • ✓AD enumeration and attacks
  • ✓Reverse engineering
  • ✓Network pivoting
  • ✓Privilege escalation
  • ✓Phishing techniques
  • ✓Evading endpoint protections
Solar lab avatar
HTB MINI PRO LAB

Solar

DIFFICULTY Hard
MACHINES 3
FLAGS 7
NETWORK TOPOLOGY LAB ENVIRONMENT
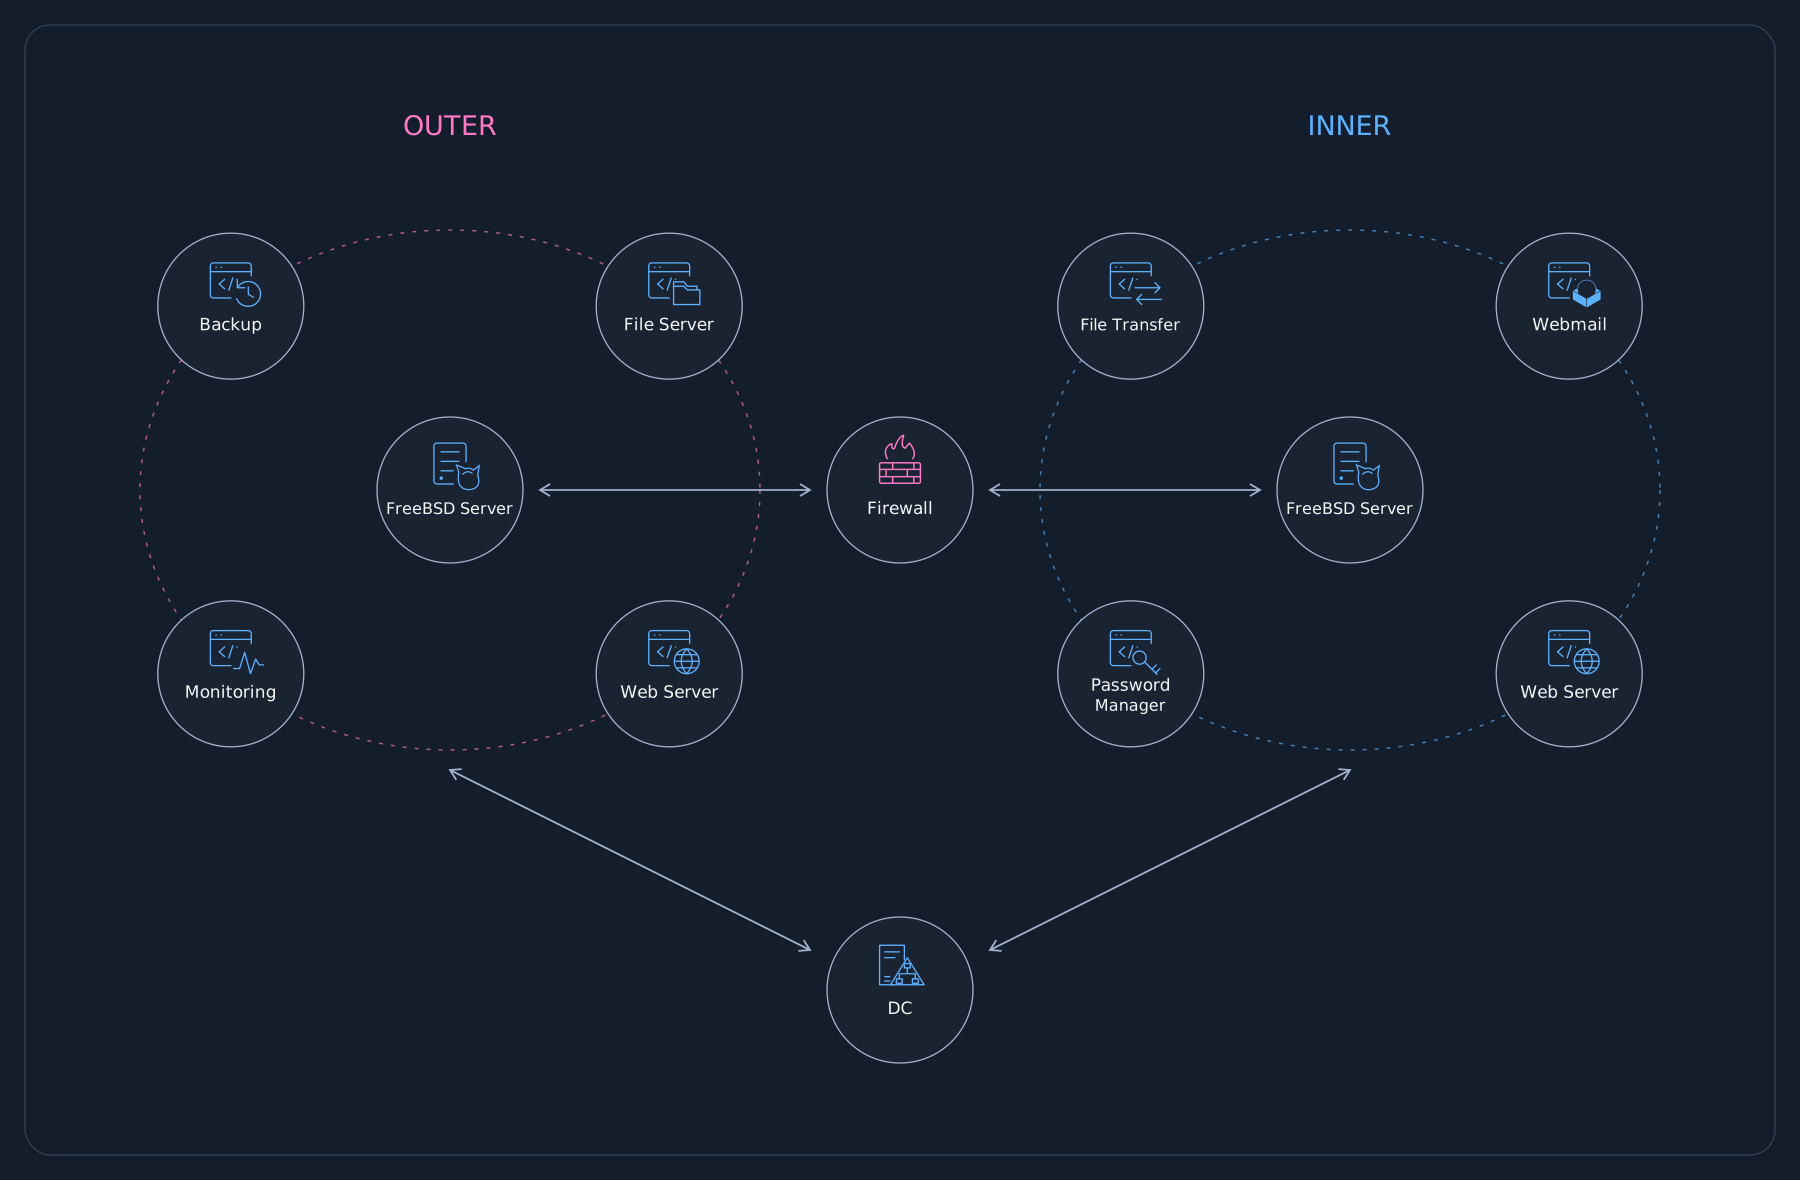
Solar lab network topology diagram
ABOUT THE LAB

Solar is designed to test your skills in enumeration, code review, pivoting, and web exploitation. The goal is to gain a foothold on the internal network, escalate privileges, and compromise the entire infrastructure while collecting several flags along the way.

THE SCENARIO

SolarSystem Space Prospection, an innovative company focusing on space exploration, wants you to assess the security of their Earth-based infrastructure.

Prerequisites

  • ✓Penetration testing methods
  • ✓Linux/Windows OS
  • ✓AD
  • ✓Web application attacks

Learning outcomes

  • ✓Enumeration
  • ✓FreeBSD exploitation
  • ✓Exploit chaining
  • ✓Out-of-band data exfiltration
  • ✓Web application attacks
  • ✓Source code review
Ascension lab avatar
HTB MINI PRO LAB

Ascension

DIFFICULTY Hard
MACHINES 4
FLAGS 7
NETWORK TOPOLOGY LAB ENVIRONMENT
Ascension lab network topology diagram
ABOUT THE LAB

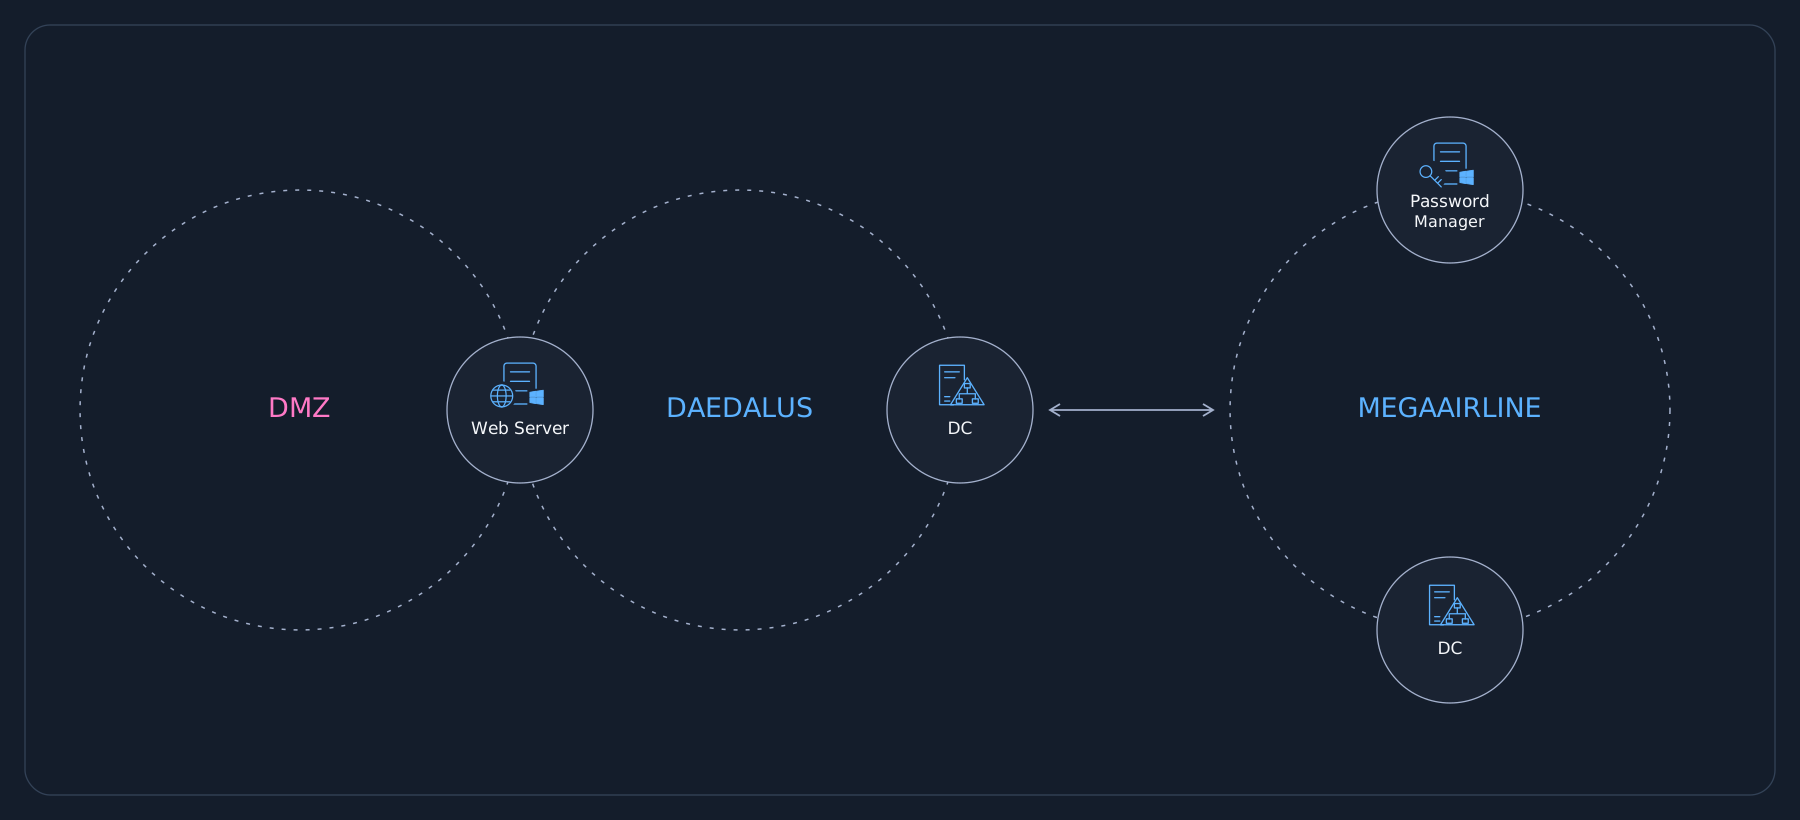
Ascension tests your skills in enumeration, exploitation, pivoting, forest traversal, and privilege escalation in two small AD networks. The goal of this scenario is to gain access to the trusted partner, pivot through the network, and compromise two AD forests.

THE SCENARIO

Daedalus Airlines is quickly becoming a major player in global aviation! However, the pace of growth has meant that the company has accumulated a lot of technical debt. To avoid a data breach, Daedalus has hired your cybersecurity firm to test its systems.

Prerequisites

  • ✓Penetration testing tools
  • ✓Windows OS
  • ✓AD
  • ✓Networking

Learning outcomes

  • ✓Enumeration
  • ✓Web application attacks
  • ✓AD exploitation
  • ✓Credential harvesting and abuse
  • ✓Network pivoting & lateral movement
  • ✓Privilege escalation strategies
  • ✓Persistence & post exploitation tactics
Odyssey lab avatar
HTB MINI PRO LAB

Odyssey

DIFFICULTY Hard
MACHINES 4
FLAGS 7
NETWORK TOPOLOGY LAB ENVIRONMENT
Odyssey lab network topology diagram
ABOUT THE LAB

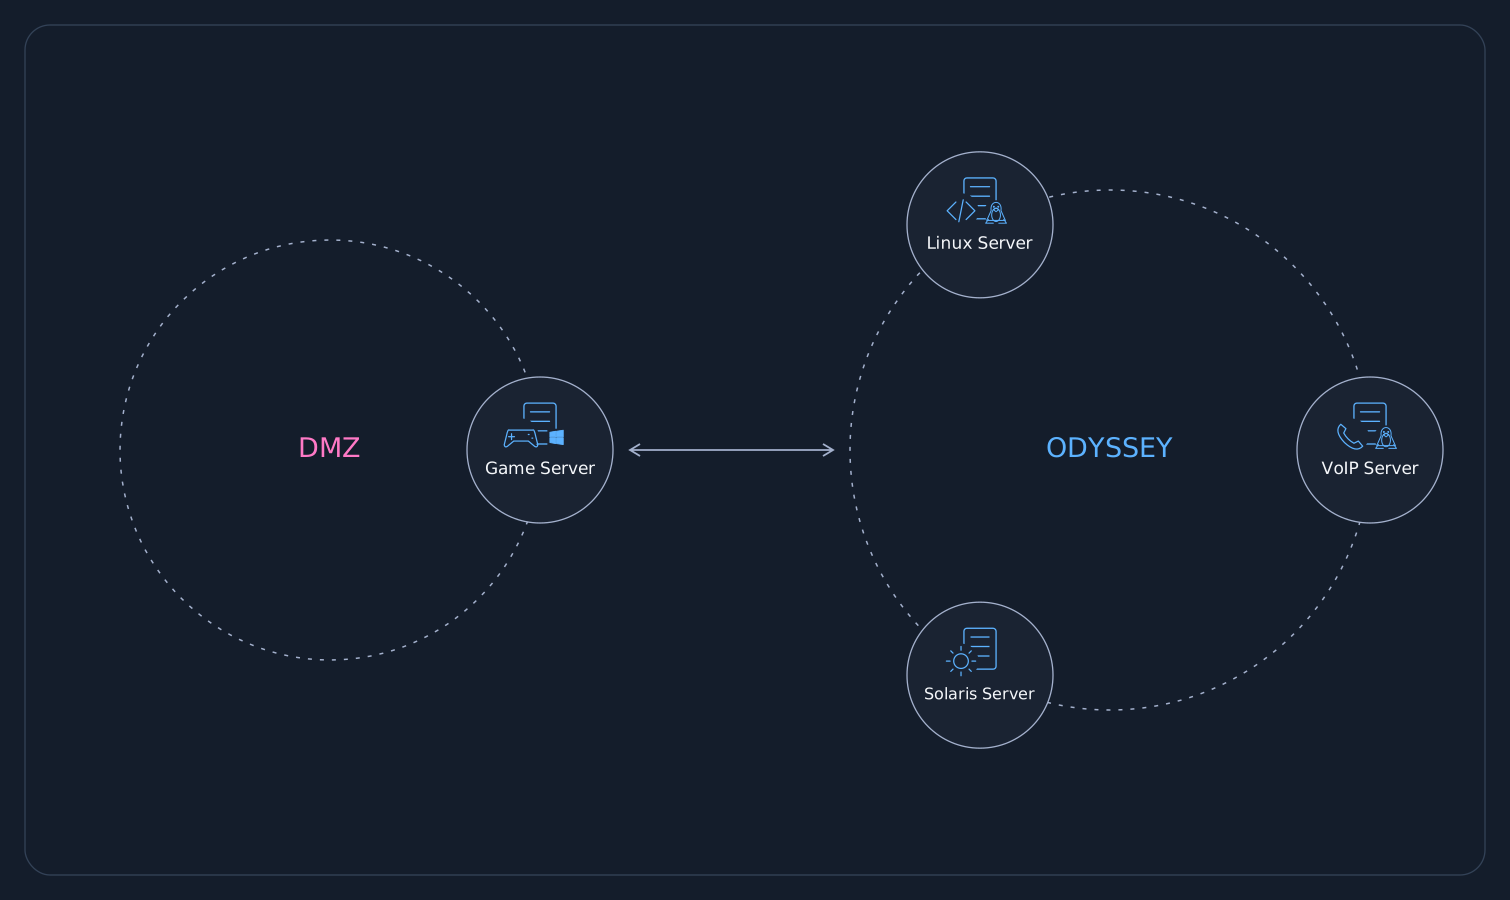
Odyssey is designed to test your skills in enumeration, reverse engineering, VoIP exploitation, and more. The goal is to gain a foothold on the internal network, escalate privileges, and compromise the gaming infrastructure while collecting several flags along the way.

THE SCENARIO

Odyssey Gaming is a fast-growing startup that has hired you to perform penetration testing on their infrastructure to safeguard against external threats.

Prerequisites

  • ✓Penetration testing tools
  • ✓Linux, Solaris, and Windows OS
  • ✓Programming knowledge
  • ✓VoIP and other custom technologies

Learning outcomes

  • ✓Enumeration
  • ✓Reverse engineering
  • ✓VoIP exploitation
  • ✓Phishing techniques
  • ✓Kubernetes exploitation
  • ✓Solaris OS exploitation
  • ✓Web application attacks
  • ✓Source code review
  • ✓Game server exploitation
Kaiju lab avatar
HTB MINI PRO LAB

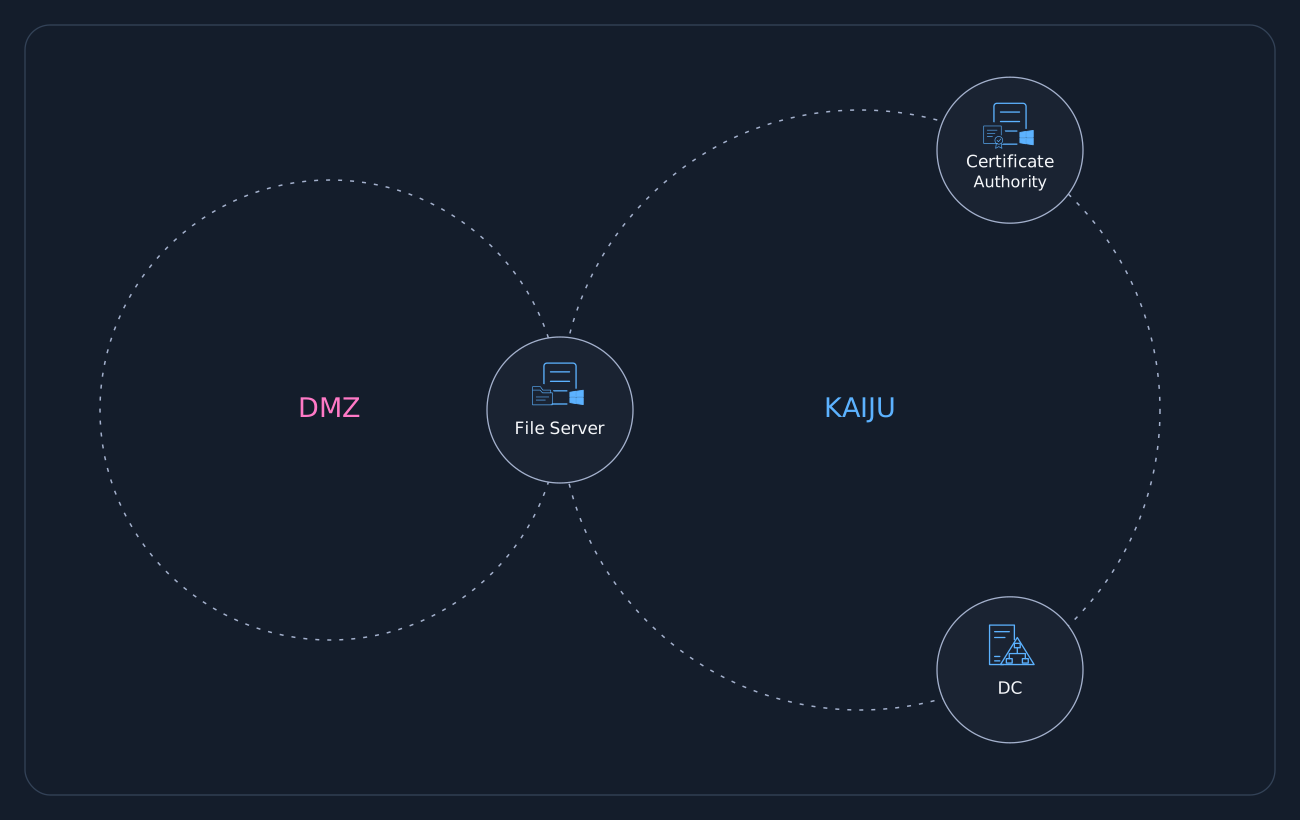
Kaiju

DIFFICULTY Hard
MACHINES 3
FLAGS 4
NETWORK TOPOLOGY LAB ENVIRONMENT
Kaiju lab network topology diagram
ABOUT THE LAB

Kaiju is a simulation set within a self-contained Active Directory environment. The goal is to gain an initial foothold by discovering and exploiting a series of service misconfigurations and ultimately achieving full domain compromise.

THE SCENARIO

You are tasked with performing a red team engagement on Kaiju Inc. Your goal is to assess the security posture of the environment by attempting to gain access to the internal network and escalate privileges within the domain.

Prerequisites

  • ✓Networking
  • ✓Penetration testing methods
  • ✓AD

Learning outcomes

  • ✓AD enumeration and attacks
  • ✓Abusing misconfigurations in common services
  • ✓DLL injections
  • ✓Networking pivoting
  • ✓Local privilege escalation
  • ✓ADCS Golden Certificate attacks
Push lab avatar
HTB MINI PRO LAB

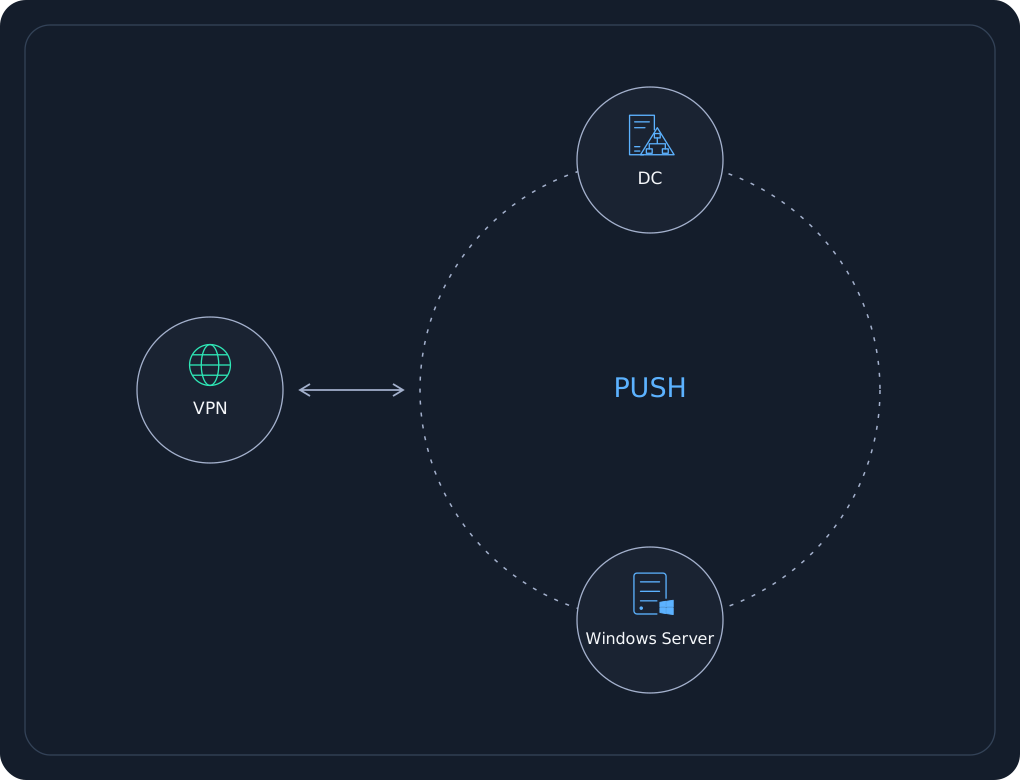
Push

DIFFICULTY Hard
MACHINES 2
FLAGS 3
NETWORK TOPOLOGY LAB ENVIRONMENT
Push lab network topology diagram
ABOUT THE LAB

Push is a compact AD lab consisting of a single domain controller and one member server. The scenario focuses on advanced attack techniques, including ClickOnce application exploitation, Microsoft Configuration Manager (SCCM) coercion, and Active Directory Certificate Services (AD CS) abuse leading to Golden Certificate attacks.

THE SCENARIO

You are tasked with performing a penetration test on Push, a small Windows AD environment. You will be required to exploit real-world applications and chain attack techniques using common services and management applications found in enterprise environments.

Prerequisites

  • ✓Windows/AD enumeration skills (LDAP, BloodHound)
  • ✓SMB, FTP & ISS reconnaissance
  • ✓ClickOnce application structure & signing bypass
  • ✓Certificate Services & PKI concepts
  • ✓Offensive SCCM techniques

Learning outcomes

  • ✓Crafting malicious ClickOnce deployments
  • ✓Coercing NTLM authentication with SCCM
  • ✓ADCS Golden Certificate attacks
  • ✓Advanced lateral movement techniques in Windows environments
  • ✓AD misconfigurations
Sidecar lab avatar
HTB MINI PRO LAB

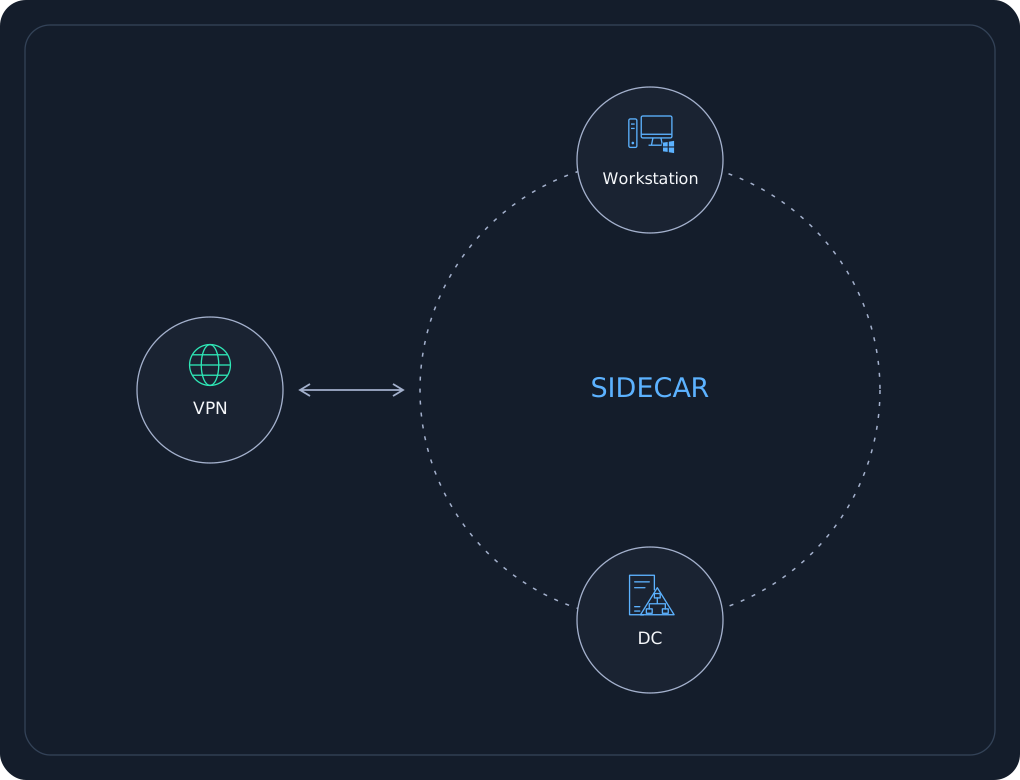
Sidecar

DIFFICULTY Hard
MACHINES 2
FLAGS 2
NETWORK TOPOLOGY LAB ENVIRONMENT
Sidecar lab network topology diagram
ABOUT THE LAB

Sidecar is a compact AD environment comprising two Windows systems. Despite its small size, the scenario is intended for practitioners with prior Active Directory penetration testing experience, as it requires a solid understanding of enumeration, privilege escalation, and attack path identification.

THE SCENARIO

You are tasked with performing a penetration test on Sidecar, involving a Windows-only Active Directory environment.

Prerequisites

  • ✓Penetration testing methods
  • ✓Kerberos ticket operations
  • ✓AD attacks
  • ✓Abusing SeTcbprivilege privilege
  • ✓Windows Lnk file abuses

Learning outcomes

  • ✓AD attacks
  • ✓Shadow credentials attacks
  • ✓Kerberos attacks
  • ✓Abusing SeTcbPrivilege privilege
  • ✓Lnk file abuses
Control lab avatar
HTB MINI PRO LAB

Control

DIFFICULTY Hard
MACHINES 2
FLAGS 3
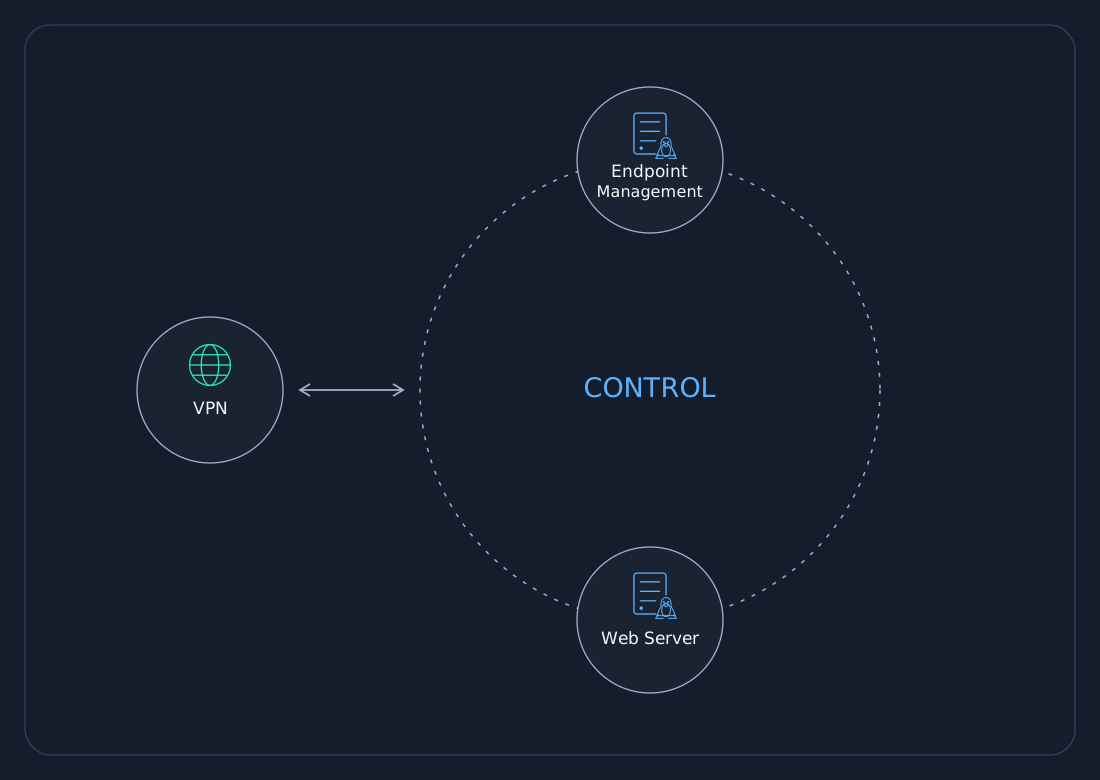
NETWORK TOPOLOGY LAB ENVIRONMENT
Control lab network topology diagram
ABOUT THE LAB

Control simulates a compact Linux-based environment that focuses on realistic post-exploitation techniques. The goal is to progress from an initial foothold to full root access across multiple hosts by exploiting web applications, abusing OSCTRL and osquery management tooling, and leveraging operational misconfigurations.

THE SCENARIO

You are tasked with performing a penetration test on Control, a small multi-host Linux environment that simulates a realistic internal network and endpoint-management infrastructure. The lab contains two primary hosts ((os.control.vl and intra.control.vl) and a variety of services (web apps, OSCTRL/osquery, SSH, nginx, Docker) that chain together to a full domain compromise.

Prerequisites

  • ✓Penetration testing methods
  • ✓Linux command line and SSH
  • ✓Web application reconnaissance & exploitation
  • ✓Osquery/endpoint management concepts (nice to have)
  • ✓SSH key auth and basic container/Docker concepts

Learning outcomes

  • ✓Web application reconnaissance and exploitation
  • ✓Privilege escalation
  • ✓Credential discovery and use
  • ✓Endpoint management abuse (OSCTRL/osquery)
  • ✓Lateral movement
  • ✓Remote code execution via insecure operational tooling
  • ✓Container escape and host compromise
Intercept lab avatar
HTB MINI PRO LAB

Intercept

DIFFICULTY Hard
MACHINES 2
FLAGS 2
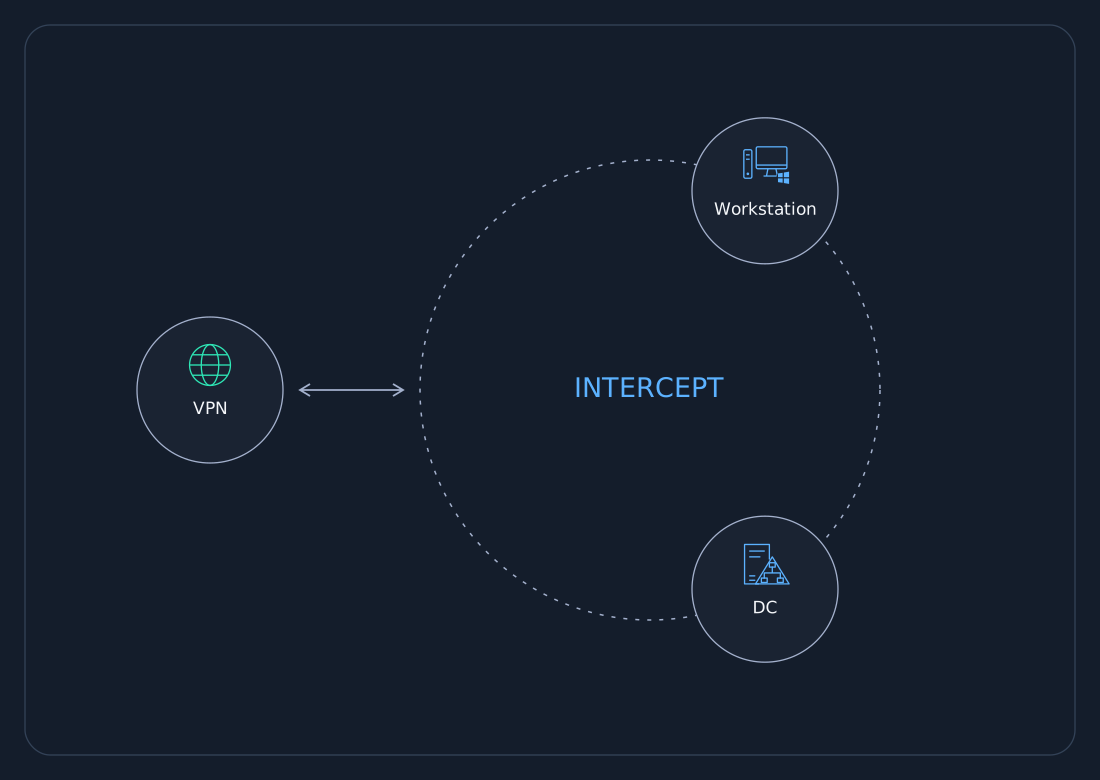
NETWORK TOPOLOGY LAB ENVIRONMENT
Intercept lab network topology diagram
ABOUT THE LAB

Intercept simulates a Windows-based enterprise environment containing a range of common AD vulnerabilities and misconfigurations. The goal is to compromise the domain from an unauthenticated starting point by performing thorough enumeration, exploiting authentication weaknesses, and abusing certificate services to achieve full domain administrator access.

THE SCENARIO

You are tasked with performing a red team engagement on Intercept involving a Windows only AD environment.

Prerequisites

  • ✓Penetration testing methods
  • ✓AD
  • ✓Networking knowledge

Learning outcomes

  • ✓AD enumeration and attacks
  • ✓Abusing NTLM relay attacks
  • ✓Abusing authentication coercion attacks
  • ✓Active Directory Certificate Service abuse