HTB PROFESSIONAL LABS

Professional Labs Directory

Explore HTB’s collection of Professional Labs, discover what each scenario offers, and find the right ones to develop and assess your team's cybersecurity skills.

Intermediate Professional Labs

Develop intermediate red teaming skills through advanced Active Directory attacks, lateral movement, persistence, and post-exploitation techniques. Designed for experienced enterprise penetration testers, these labs focus on realistic misconfigurations, living-off-the-land techniques, phishing, and custom exploitation in more security-mature environments.

Zephyr lab avatar
HTB PRO LAB

Zephyr

DIFFICULTY Intermediate
MACHINES 17
FLAGS 17
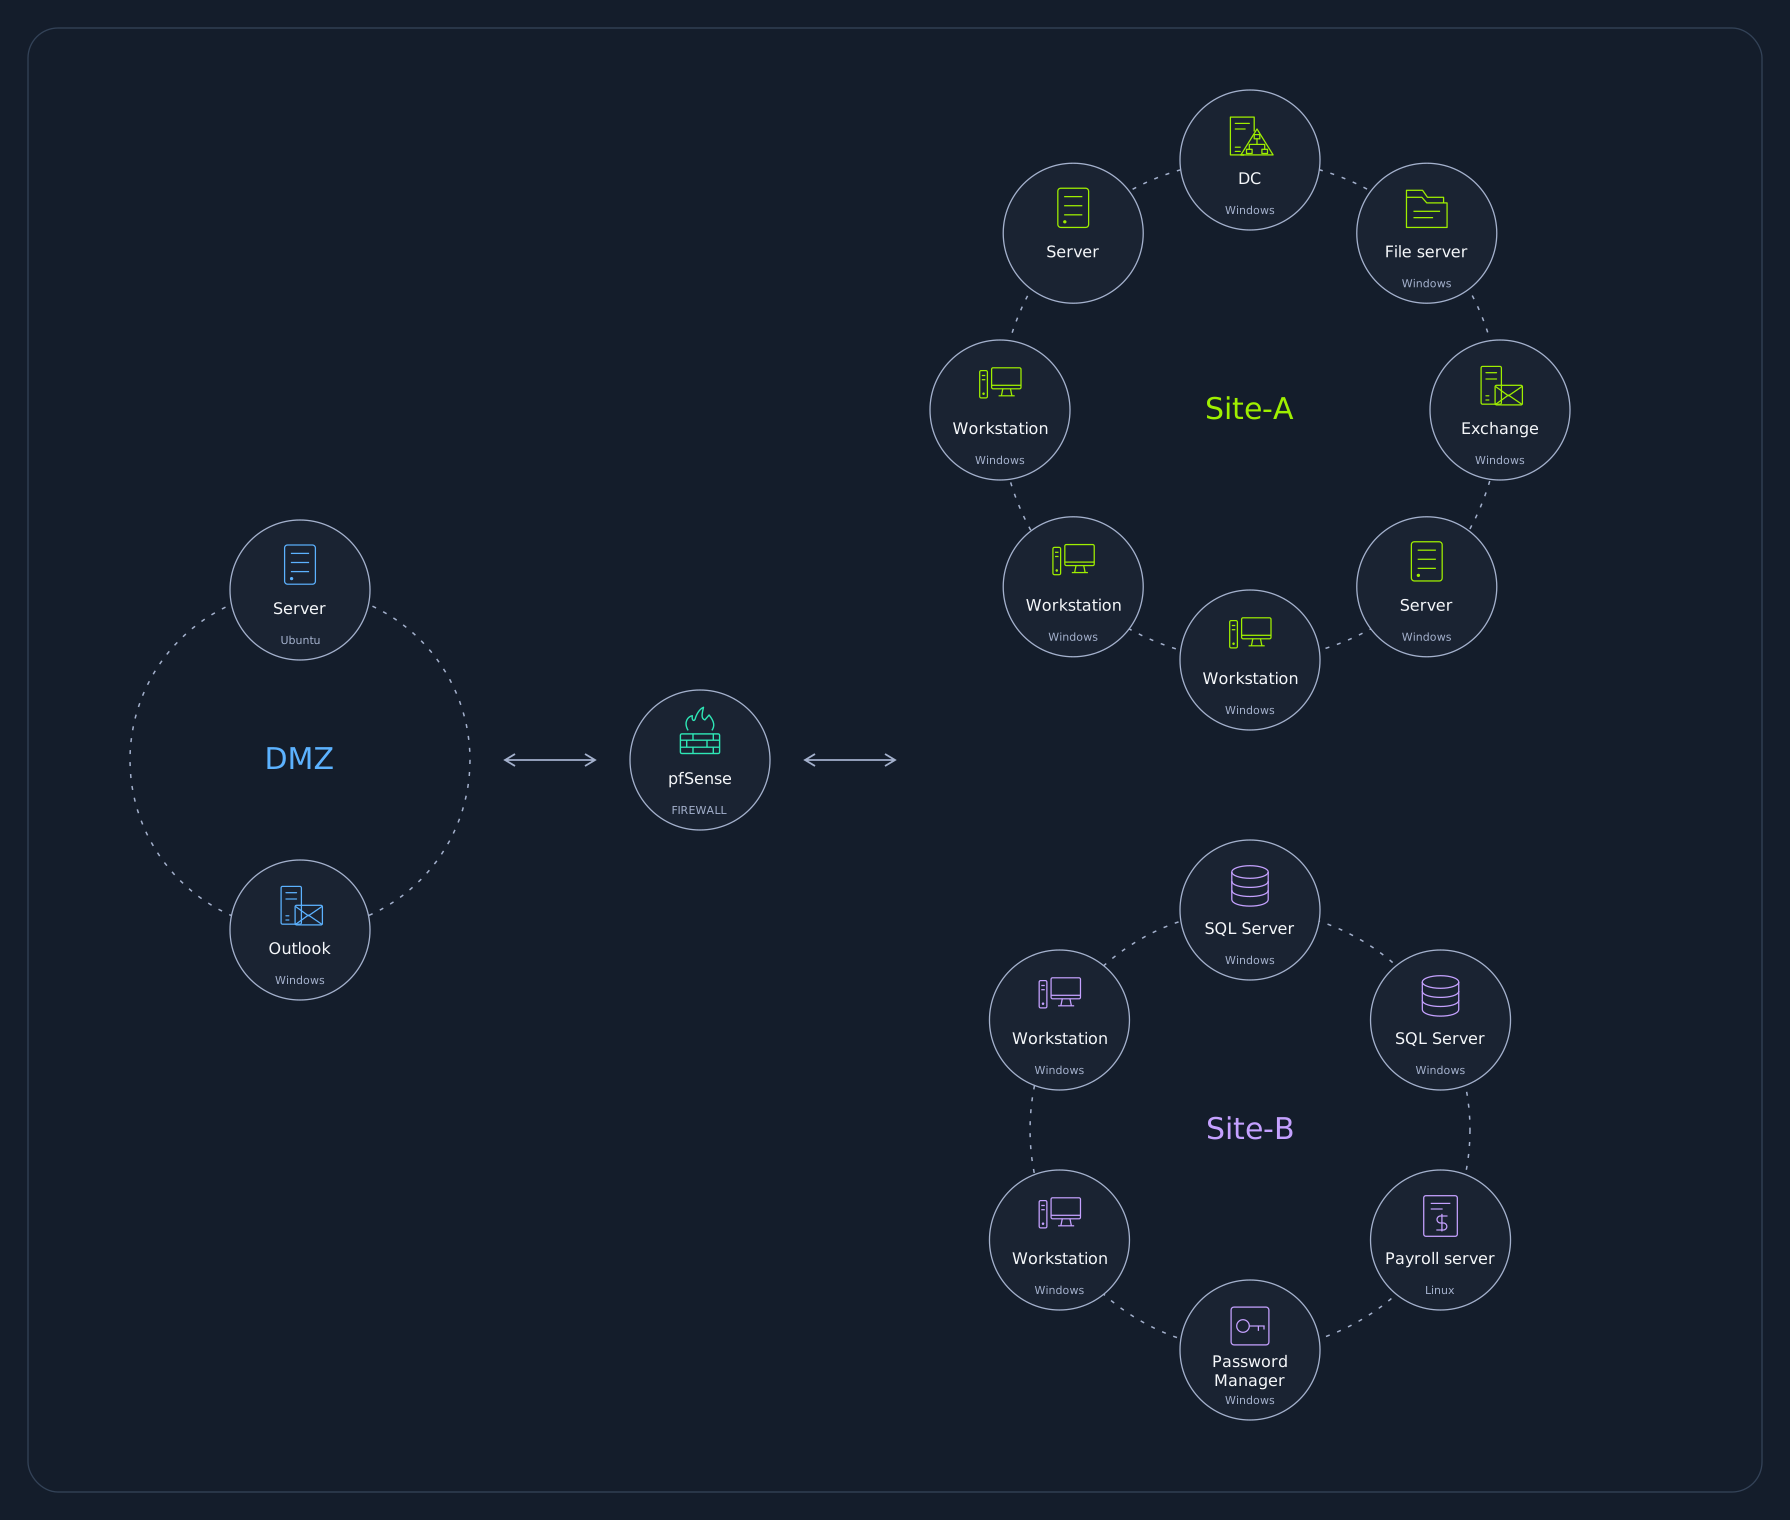
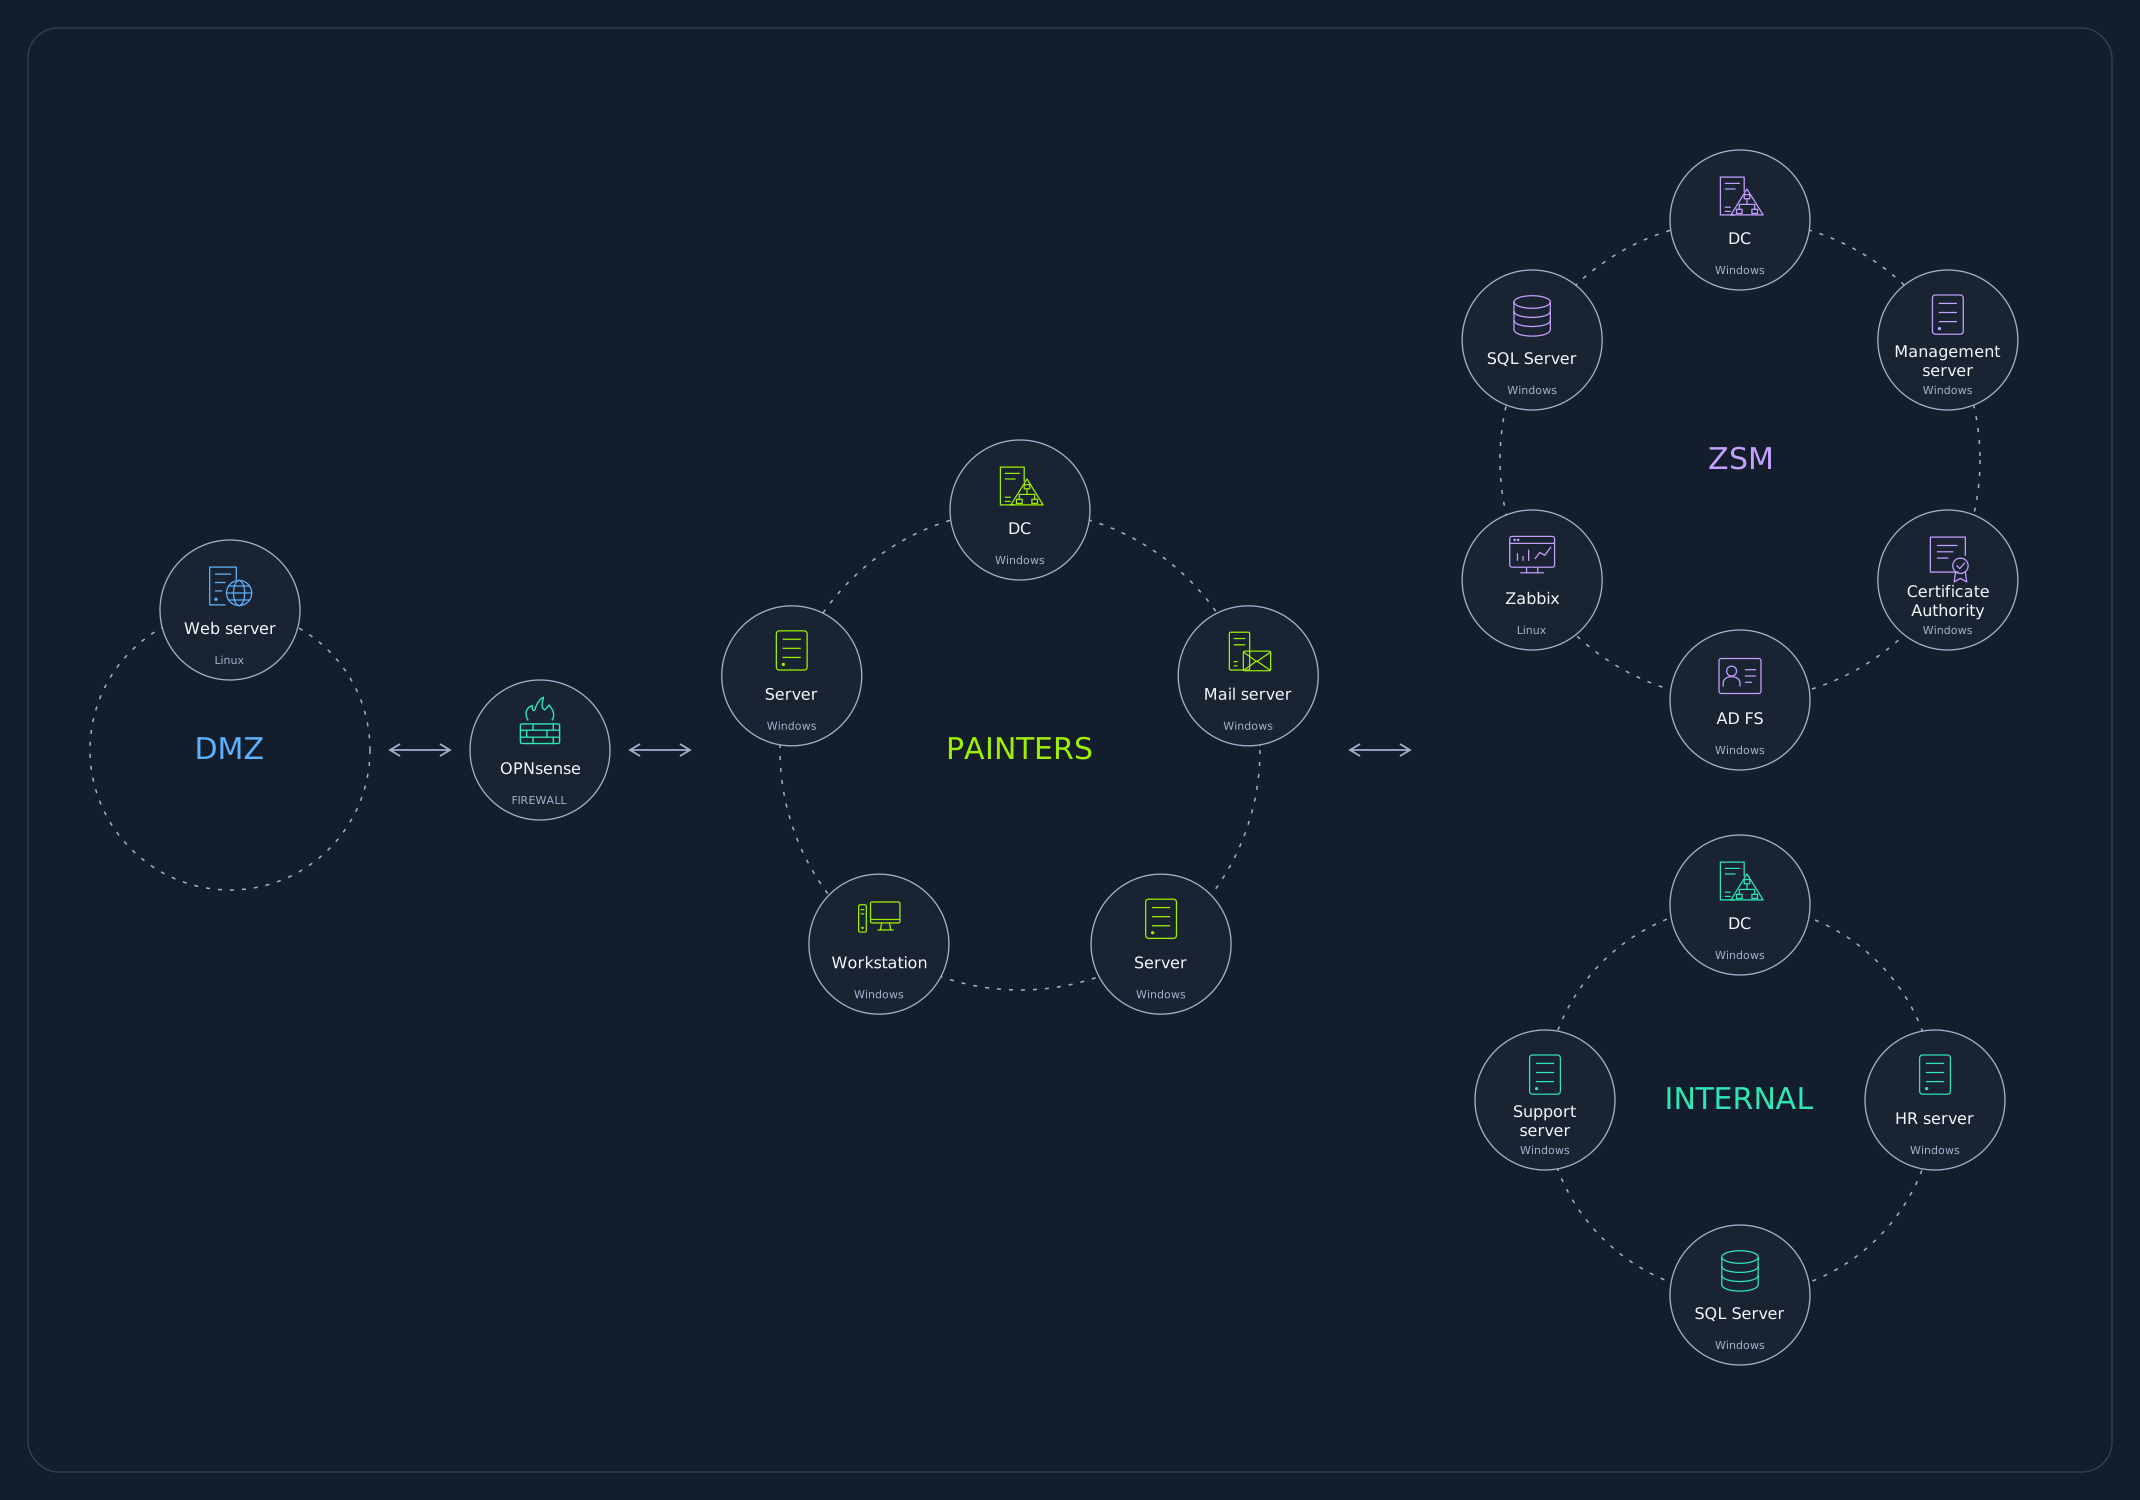
NETWORK TOPOLOGY LAB ENVIRONMENT
Zephyr lab network topology diagram
ABOUT THE LAB

Zephyr is an intermediate-level red team simulation environment, designed to be attacked as a means of learning and honing your engagement skills and improving your AD enumeration and exploitation skills. Zephyr includes a wide range of essential Active Directory flaws and misconfigurations to allow players to get a foothold in corporate environments.

THE SCENARIO

Zephyr Server Management have been hired by Painters organization to actively maintain their infrastructure as they continue to grow as a business. The organizations are mandated to have quarterly penetration tests and have employed you to actively seek any potential vulnerabilities that could lead to both the Painters and Zephyr Server Management networks being fully compromised. You have been assigned the task of testing the internal network and have been given access to a VPN to communicate with the network. You are tasked to explore the corporate environment, pivot across trust boundaries, and ultimately attempt to compromise all Painters and Zephyr Server Management entities.

Prerequisites

  • ✓Penetration testing tools
  • ✓Windows/Linux OS
  • ✓Windows AD
  • ✓Microsoft SQL servers
  • ✓Powershell
  • ✓Pivoting e.g Proxychains and Metasploit usage
  • ✓BloodHound usage

Learning outcomes

  • ✓Enumeration
  • ✓AD exploitation
  • ✓Relay attacks
  • ✓Lateral movement & crossing trust boundaries
  • ✓SQL attacks
  • ✓Password cracking
  • ✓Privilege escalation
  • ✓Pivoting
RastaLabs lab avatar
HTB PRO LAB

RastaLabs

DIFFICULTY Intermediate
MACHINES 15
FLAGS 22
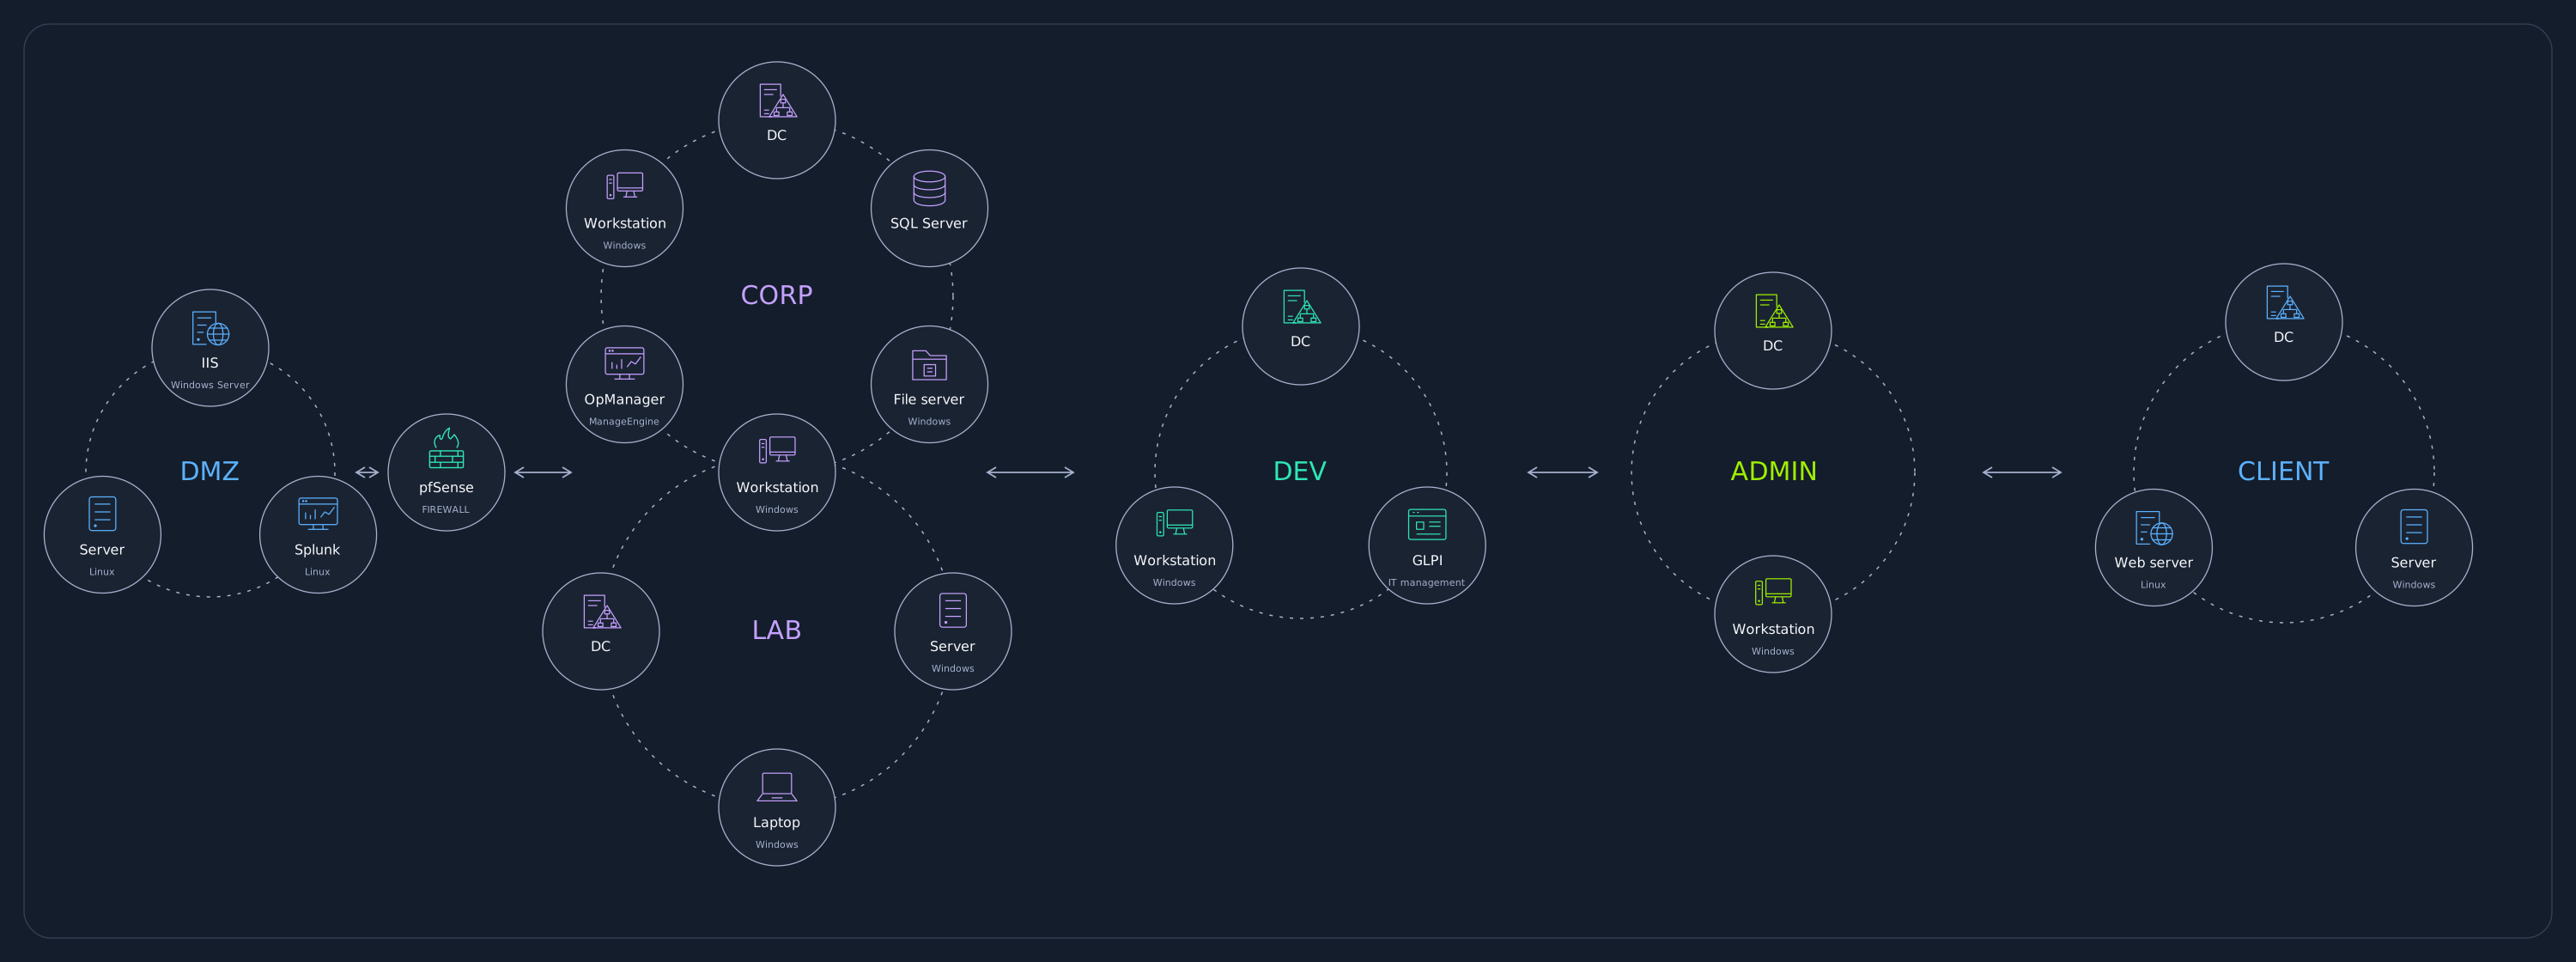
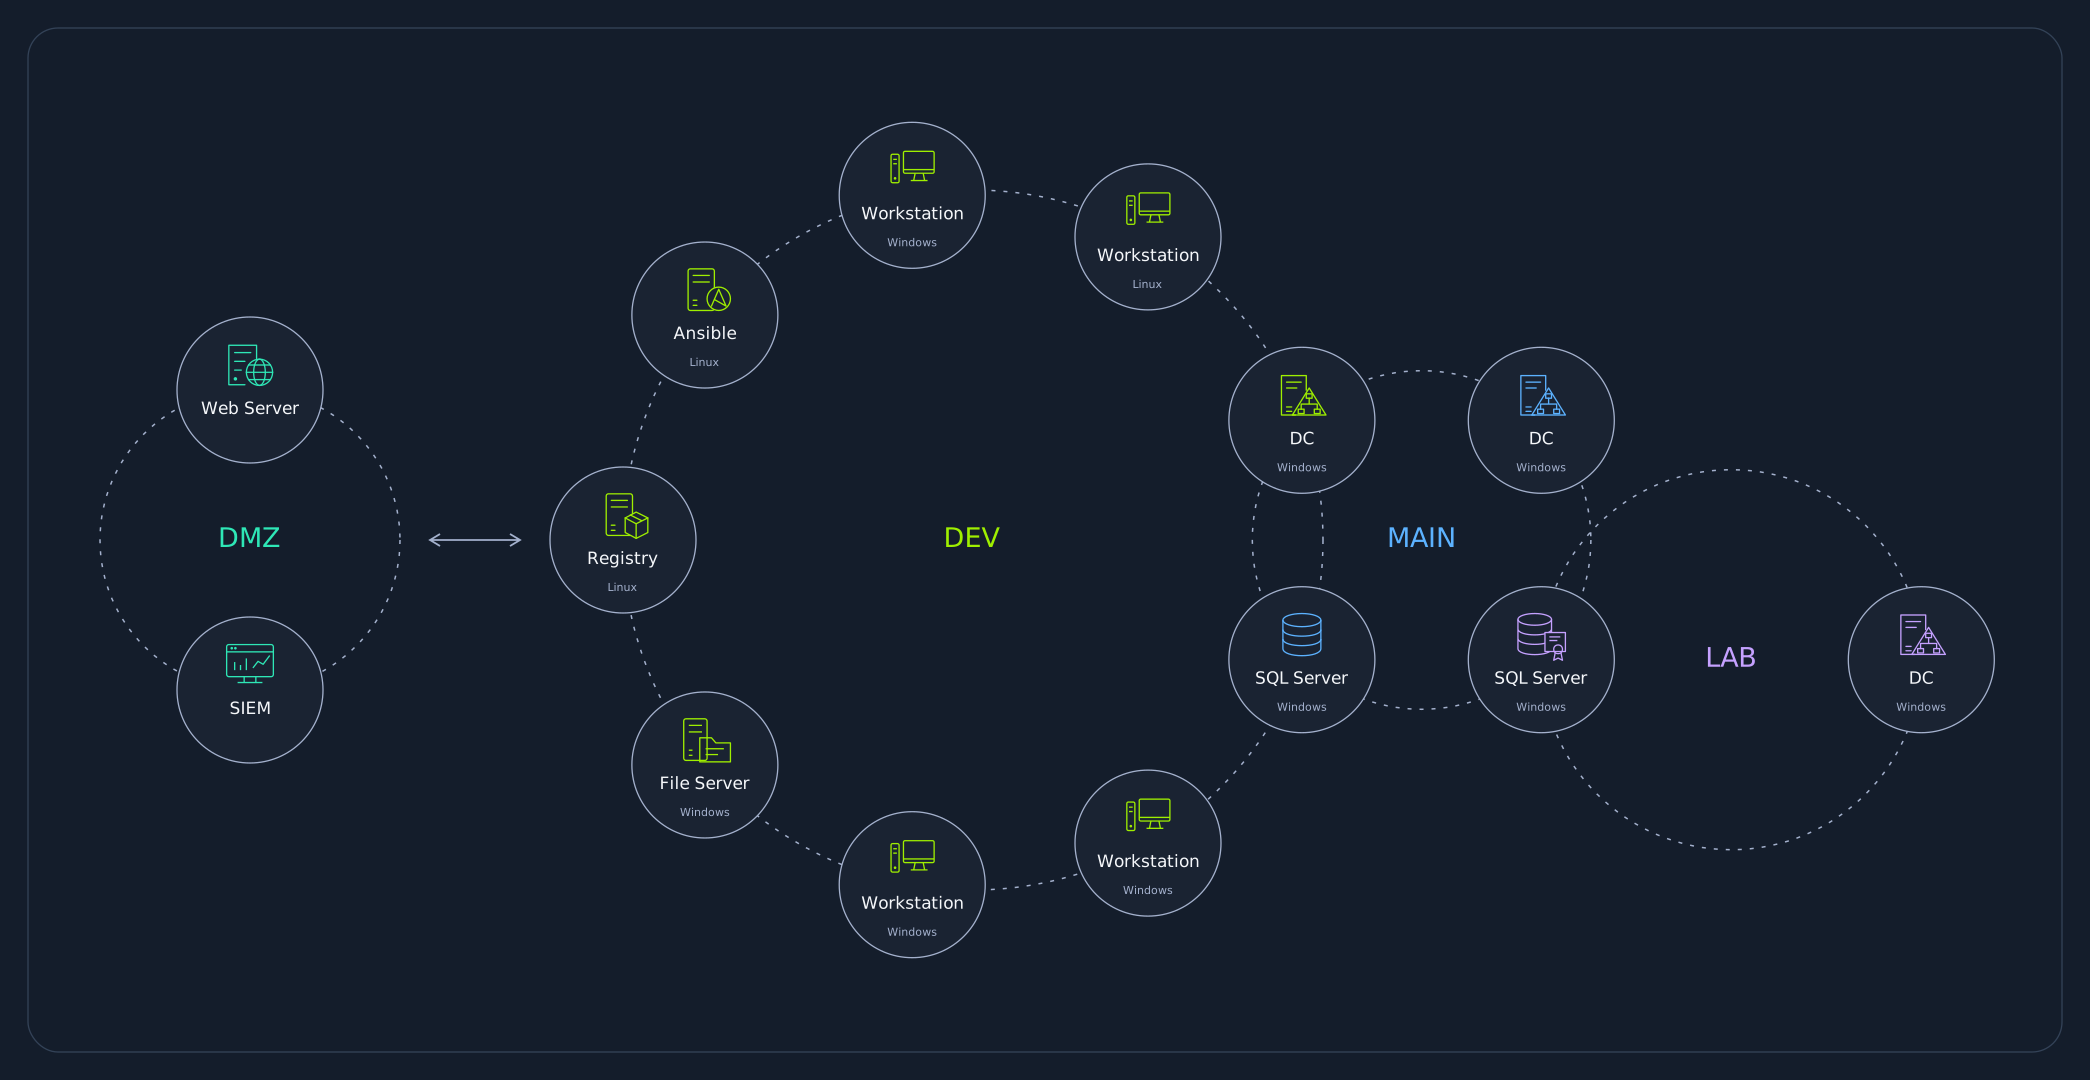
NETWORK TOPOLOGY LAB ENVIRONMENT
RastaLabs lab network topology diagram
ABOUT THE LAB

RastaLabs is designed to simulate a true-to-life corporate environment, based heavily on Microsoft Windows systems. Elements include AD (with a Server 2016 functional domain level), Exchange, Internet Information Services, and SQL Server. Machines are also segregated across multiple subnets.

THE SCENARIO

The company provides security and penetration testing services, offering expertise, flexibility and extensive support before, during and after each engagement. They have enlisted your services to perform a red team assessment of their secured AD environment. The goal is to gain a foothold, elevate privileges, establish persistence and move laterally, in order to reach the goal of domain admin.

Prerequisites

  • ✓AD enumeration
  • ✓Scripting / Programming
  • ✓Local escalation privilege
  • ✓Exploit development

Learning outcomes

  • ✓AD enumeration & exploitation
  • ✓Evading endpoint protections
  • ✓Lateral movement
  • ✓Local privilege escalation
  • ✓Phishing techniques
Offshore lab avatar
HTB PRO LAB

Offshore

DIFFICULTY Intermediate
MACHINES 21
FLAGS 38
NETWORK TOPOLOGY LAB ENVIRONMENT
Offshore lab network topology diagram
ABOUT THE LAB

Offshore is designed to mimic a large corporate AD network with a mix of Microsoft Windows operating system versions. The lab includes both Windows workstations and servers as well as components such as Internet Information Services (IIS), and Microsoft SQL Server (MSSQL), among others. The network consists of multiple domains and forests which only become reachable after compromising certain hosts. The lab also contains elements of a busy corporate network such as simulated users whose actions can be manipulated and leveraged to further access within the environment.

THE SCENARIO

Offshore Corp is mandated to have quarterly penetration tests per financial regulatory body compliance requirements, and is focused on patching. The company has completed several acquisitions, with the acquired entities being “plugged in” by means of domain trusts. If you are able to breach the perimeter and gain a foothold, you are tasked to explore the corporate environment, pivot across trust boundaries, and ultimately attempt to compromise all Offshore Corp entities. You are an agent tasked with exposing money laundering operations in an offshore international bank. Breach the DMZ and pivot through the internal network to locate the bank’s protected databases and a shocking list of international clients.

Prerequisites

  • ✓Penetration testing methods
  • ✓AD
  • ✓Web application attacks
  • ✓Linux & networking concepts such tunneling & pivoting

Learning outcomes

  • ✓AD enumeration & attacks
  • ✓Evading endpoint protections
  • ✓Lateral movement
  • ✓Local privilege escalation
  • ✓Tunnelling & pivoting
Alchemy lab avatar
HTB PRO LAB

Alchemy

DIFFICULTY Intermediate
MACHINES 16
FLAGS 21
NETWORK TOPOLOGY LAB ENVIRONMENT
Alchemy lab network topology diagram
ABOUT THE LAB

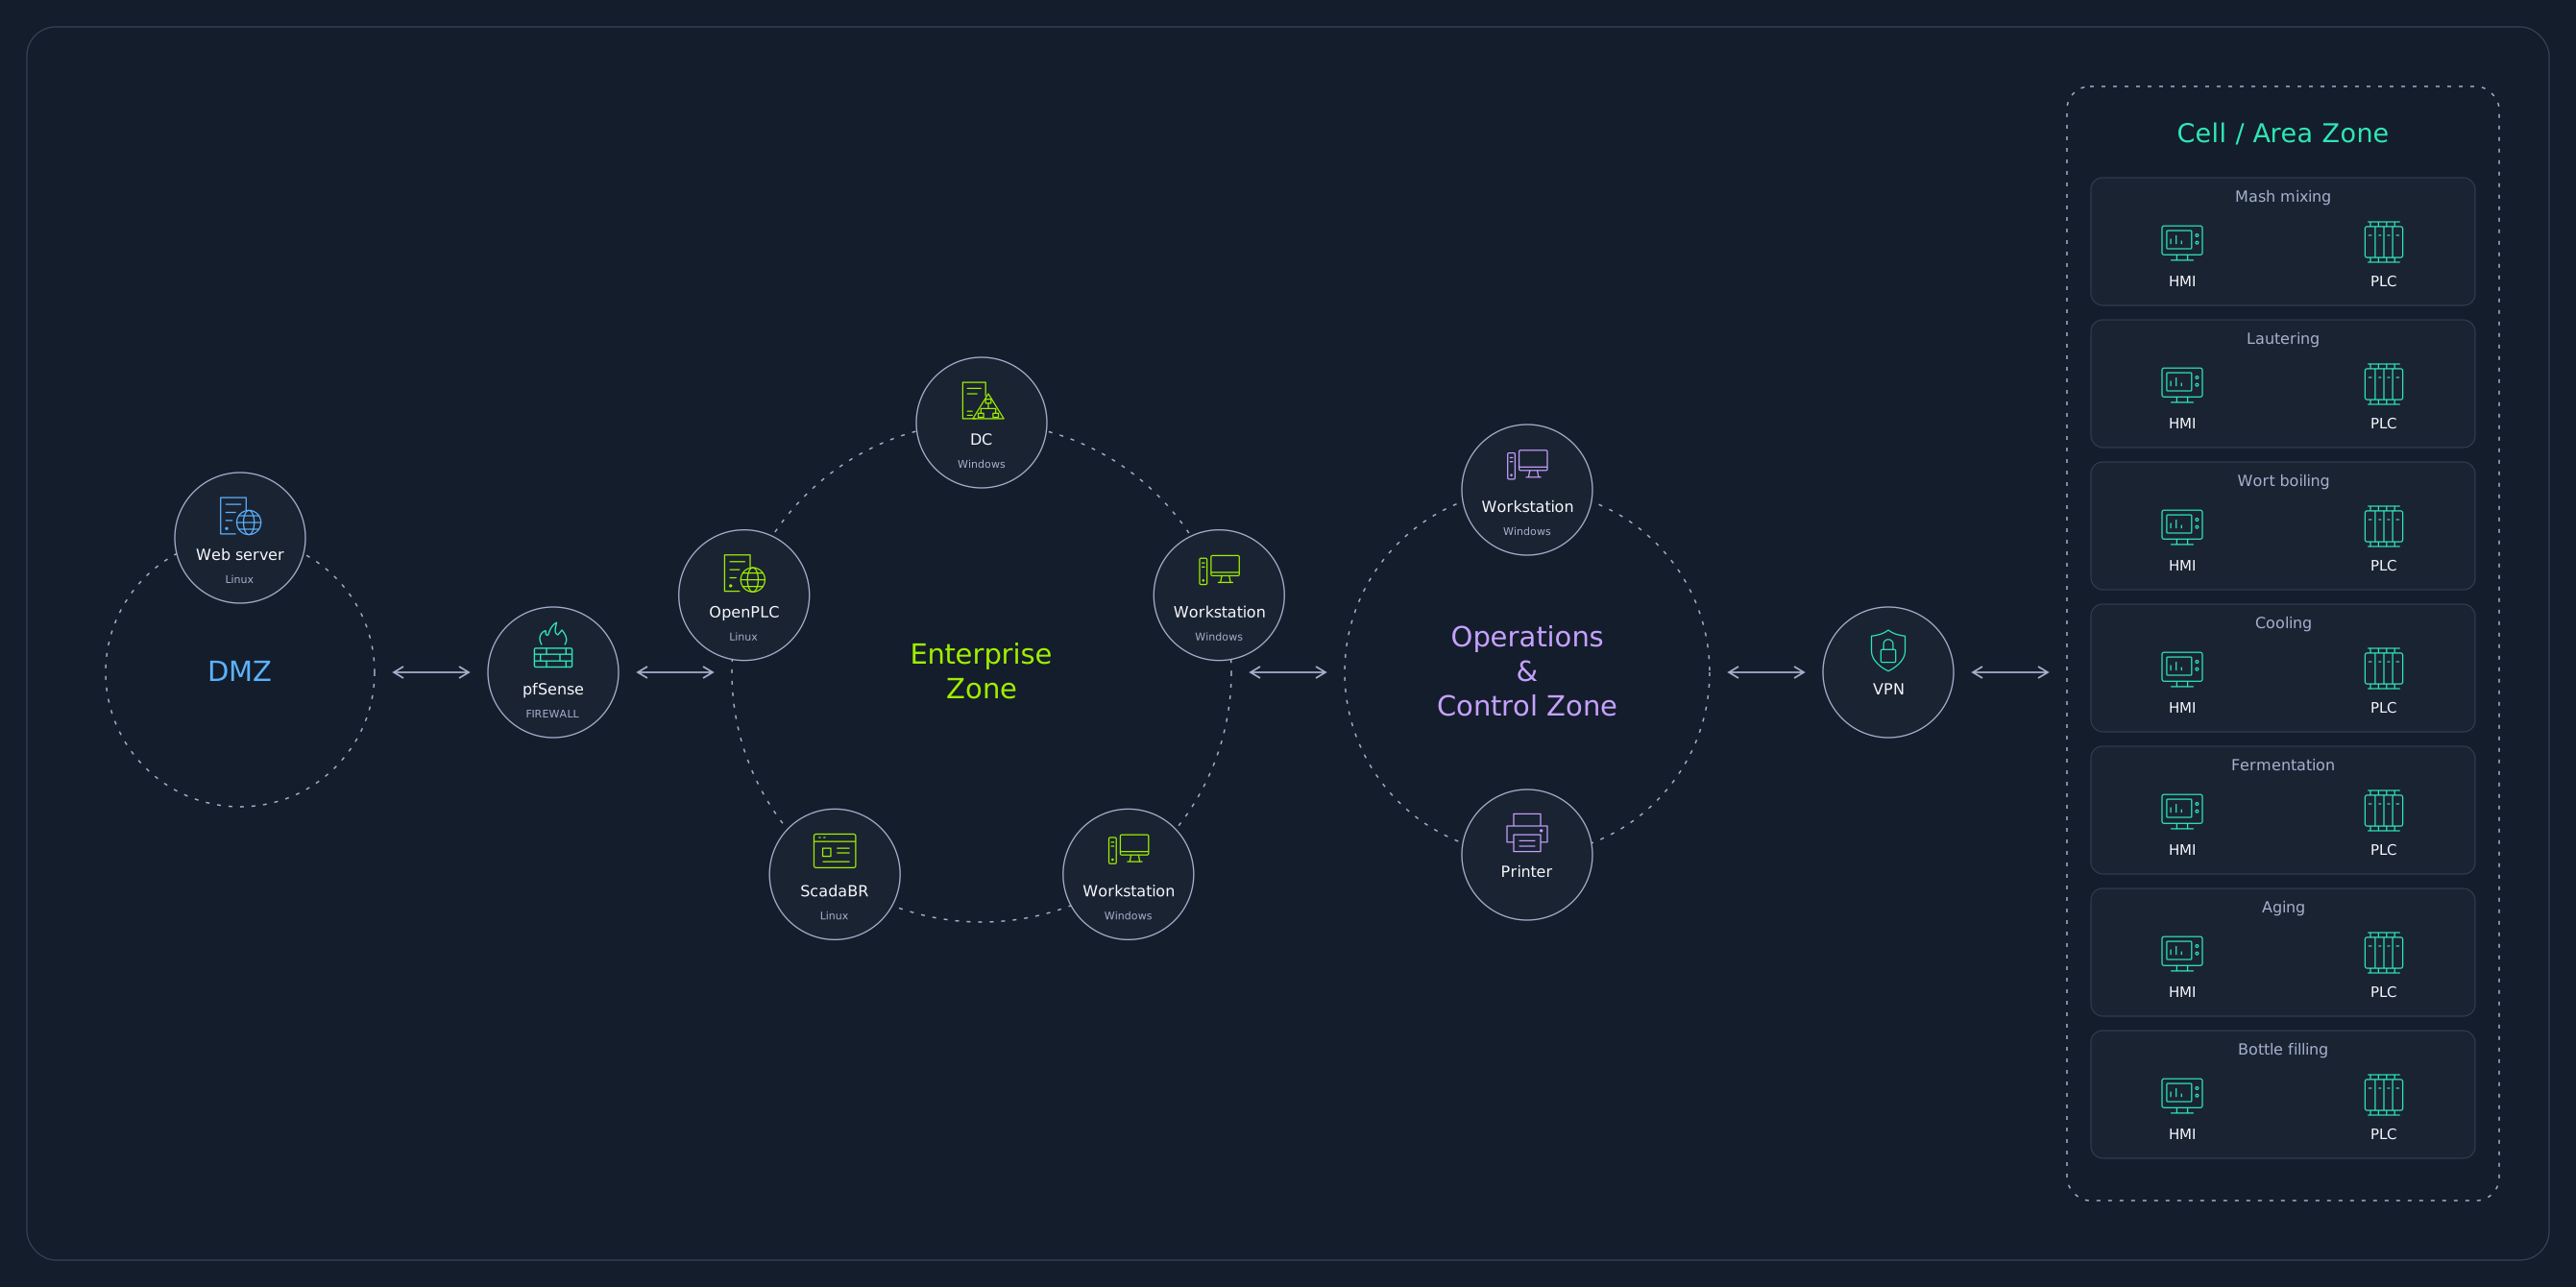
Alchemy is a medium-level Industrial Control Systems (ICS) scenario exposing members to production environments. As a blend of IT and medium-sized control system environments, Alchemy focuses on protocols, devices, and security measures based on Purdue model specifications. Engaging with Alchemy offers a solid foundation for understanding emerging threats in OT environments and highlights the significant impact of ICS security on business operations.

THE SCENARIO

You work at Industrial Alchemy LLC. and have been contracted to target Sogard Brewing Co. to enumerate and exploit their enterprise environment, steal Intellectual property (IP) such as recipes and plant specs, and attempt to disrupt their enterprise and industrial processes such as the bottling and brewing plant processes.

Prerequisites

  • ✓Penetration testing process
  • ✓Linux OS & package management
  • ✓Web exploitation knowledge
  • ✓AD enumerating & traversing

Learning outcomes

  • ✓Common ICS infrastructure (Purdue Model setup)
  • ✓Interpret & enumerate the Modbus protocol
  • ✓Interact with HMI’s and PLCs
  • ✓Common tools & software used to manage and attack ICS
Wanderer lab avatar
HTB PRO LAB

Wanderer

DIFFICULTY Intermediate
MACHINES 10
FLAGS 20
NETWORK TOPOLOGY LAB ENVIRONMENT
Wanderer lab network topology diagram
ABOUT THE LAB

Wanderer is an intermediate-level red team simulation designed to test how well-rounded your skills are. You may even find yourself having to perform some DFIR after exploiting a box in order to progress to the next step.

THE SCENARIO

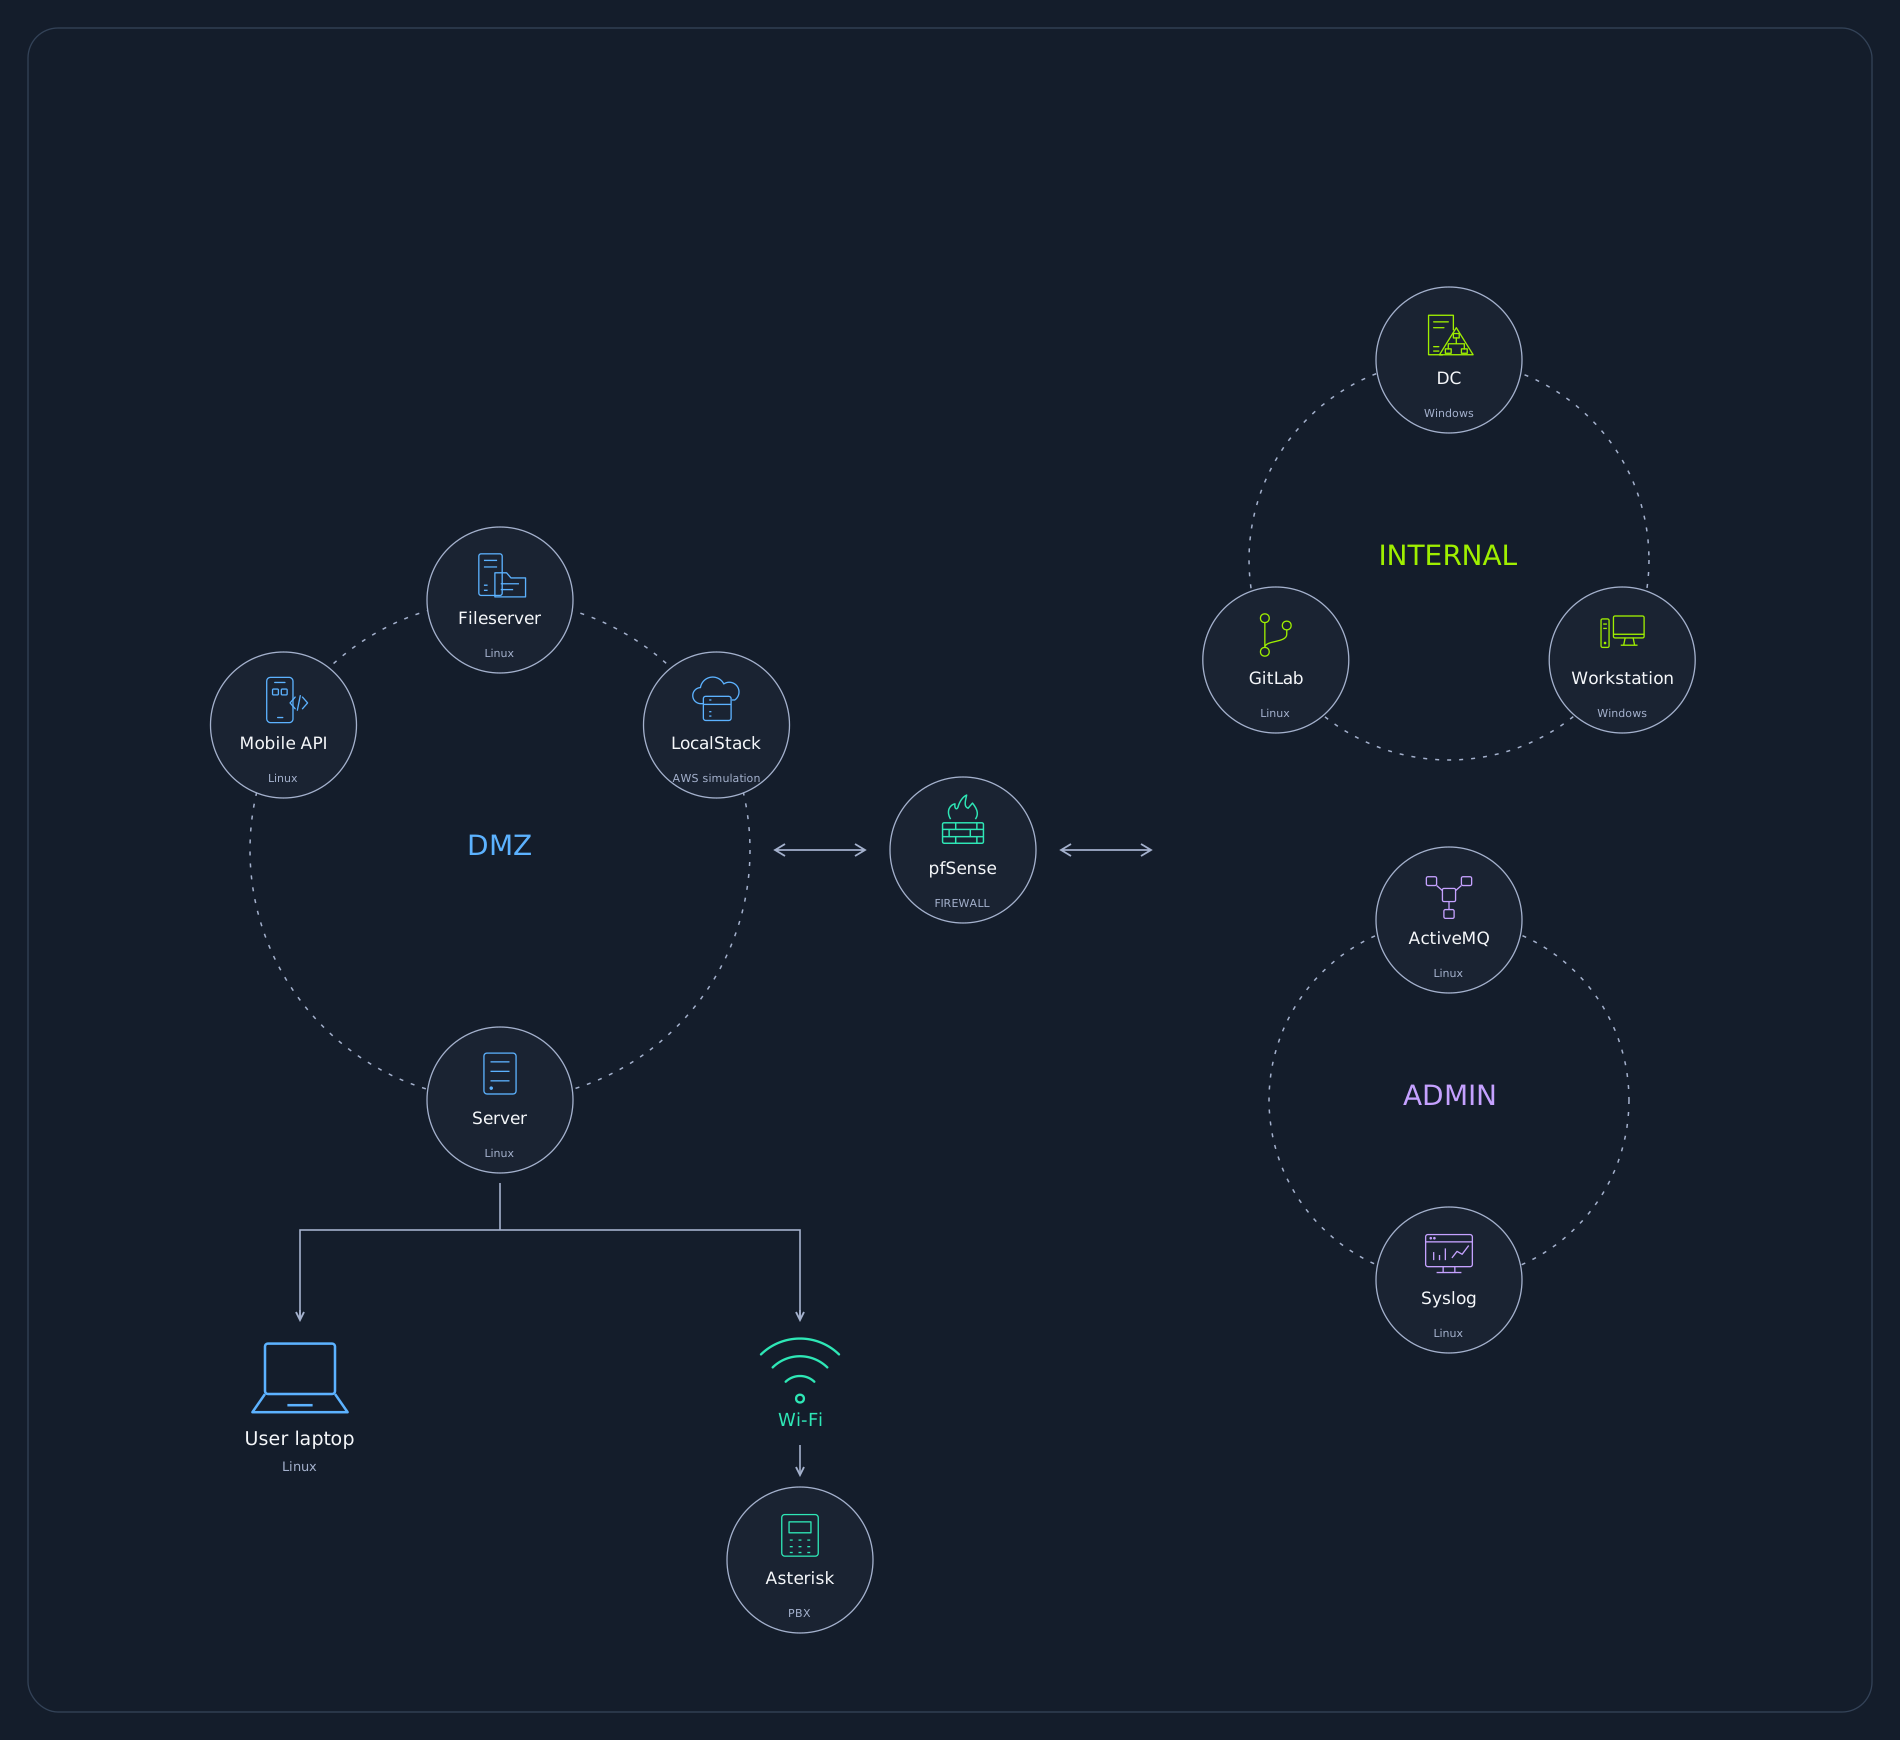
In a post-apocalyptic wasteland, there is not much left. One of the few core IT Systems left offers a mobile application to aid in calling the remaining survivors and uploading status reports to unknown leaders. It is believed that ZAX, who used to go by the pseudonym WOPR set this network up, but they went missing. You are tasked with wandering from machine to machine, collecting as much information as possible on the users who set this network up.

Prerequisites

  • ✓Penetration testing tools
  • ✓Windows OS
  • ✓Windows AD
  • ✓Web application attacks
  • ✓Networking

Learning outcomes

  • ✓Enumeration
  • ✓SQL injection and filter evasion
  • ✓Web application attacks
  • ✓Lateral movement
  • ✓Offensive forensics
  • ✓VoIP exploitation
  • ✓Basic mobile application analysis
  • ✓Basic WiFi attacks
  • ✓Asterisk attacks
Ifrit lab avatar
HTB PRO LAB

Ifrit

DIFFICULTY Intermediate
MACHINES 10
FLAGS 7
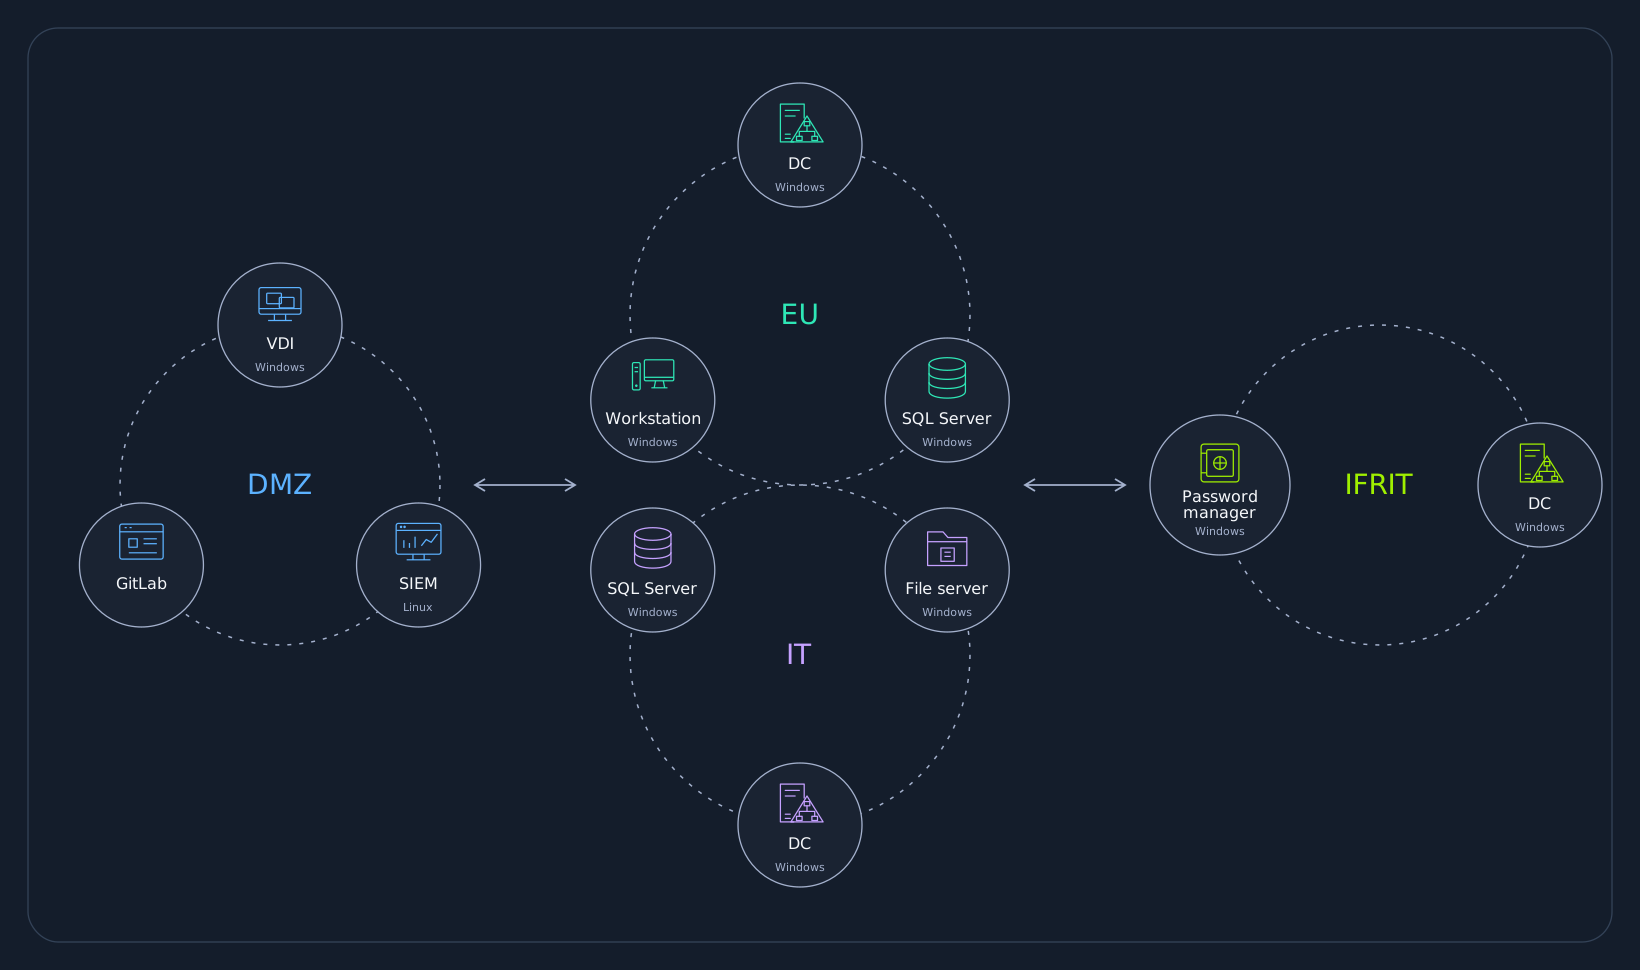
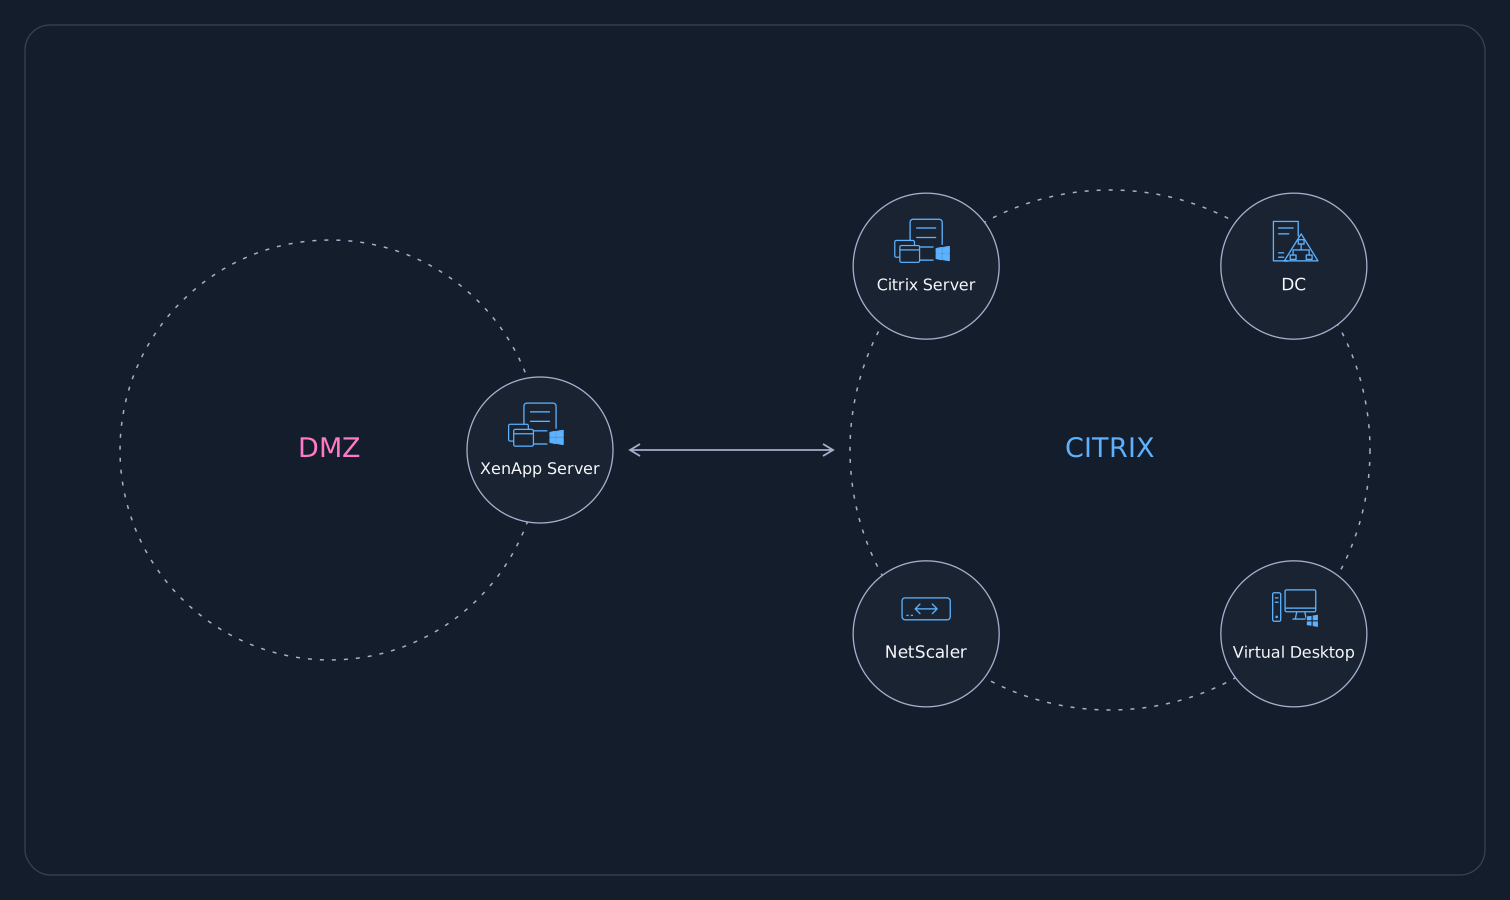
NETWORK TOPOLOGY LAB ENVIRONMENT
Ifrit lab network topology diagram
ABOUT THE LAB

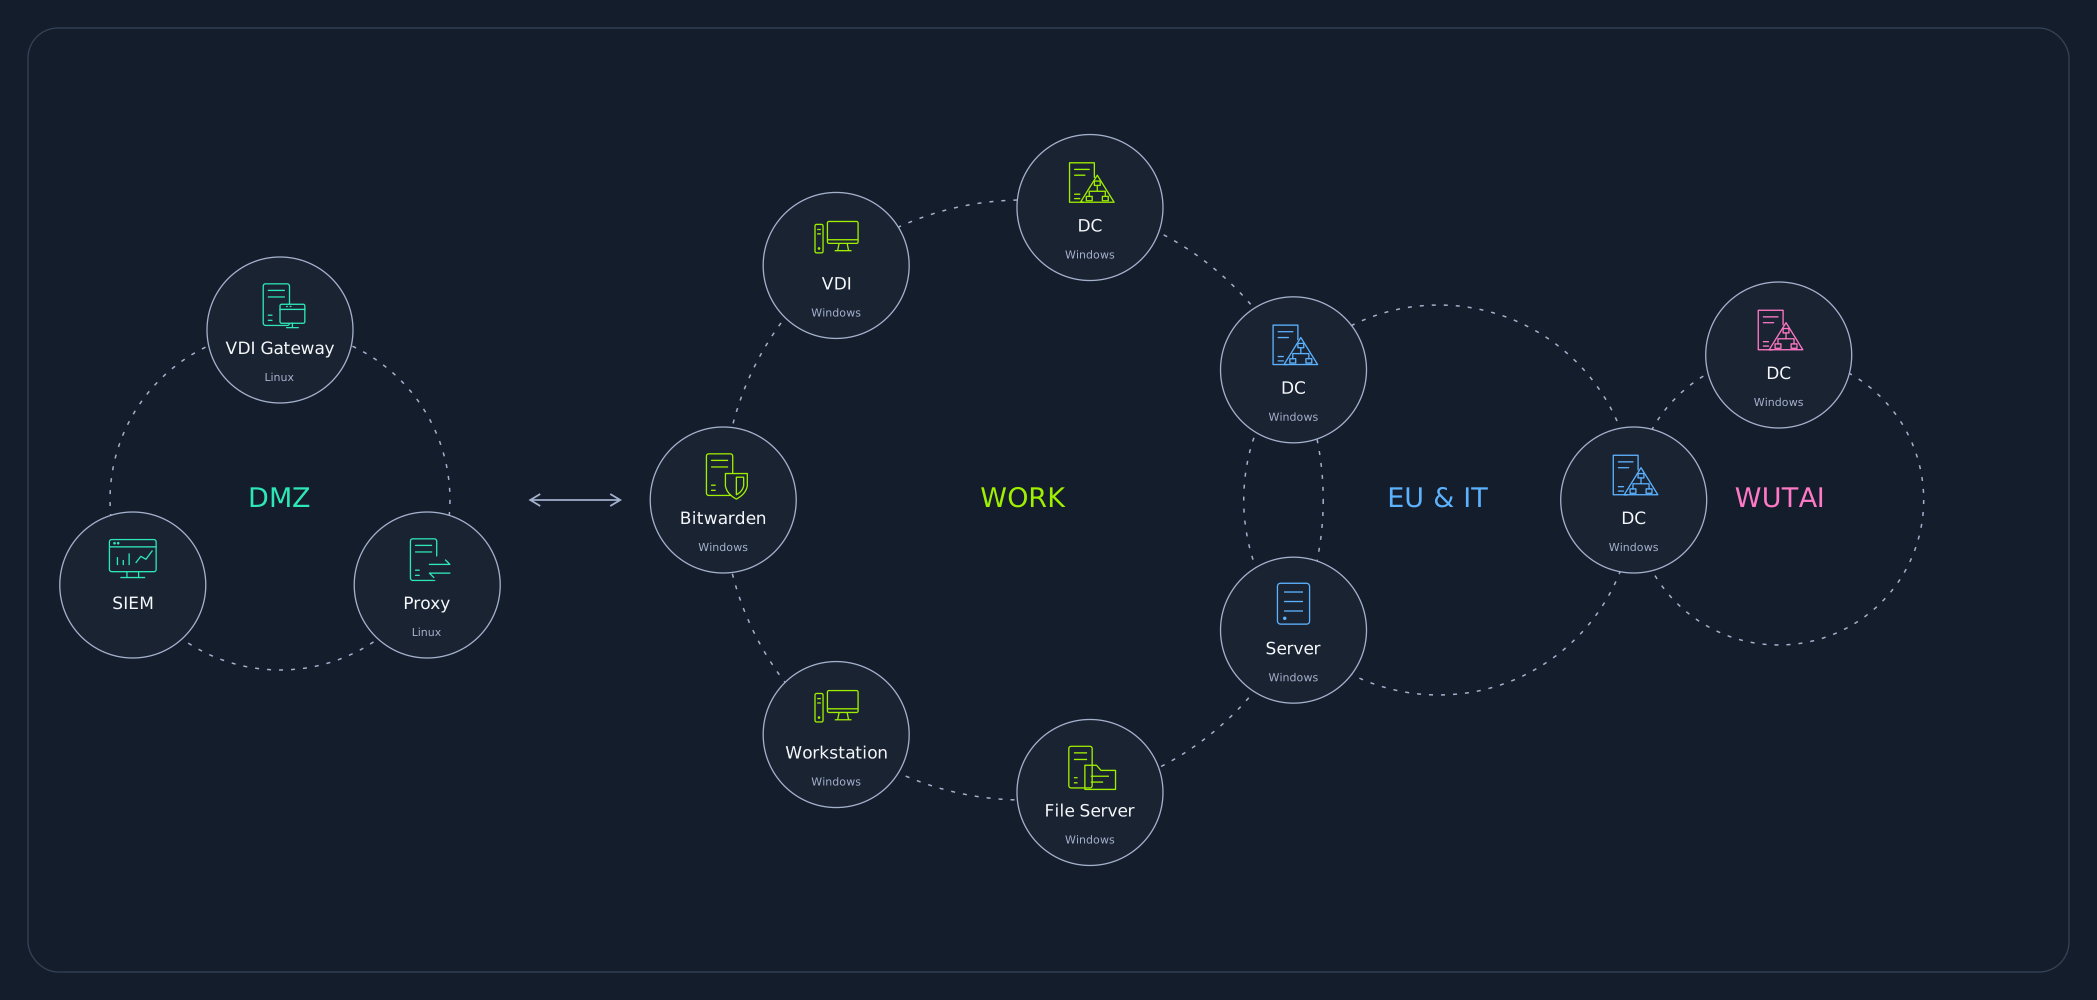
Ifrit is an intermediate red team lab that simulates an enterprise environment after a breach. The goal is to navigate a restricted virtual desktop environment and attempt to escalate privileges across a European corporate network. This lab is heavily monitored by Endpoint Detection and Response (EDR) tools, while read-only access to a Security Information and Event Management (SIEM) platform allows you to see which of your actions generate security alerts.

THE SCENARIO

Ifrit is an IT services company that introduced a new security baseline recently. To evaluate its effectiveness, you have been tasked with performing a red team engagement on Ifrit’s internal networks. In this case, the engagement will be performed as an assumed breach scenario and the company provided you with a list of users and passwords. To access the internal network, you will be able to log into a VDI environment.

Prerequisites

  • ✓Penetration testing methods
  • ✓AD

Learning outcomes

  • ✓Network and AD enumeration
  • ✓AD & custom exploitation
  • ✓AD Certificate Services
  • ✓Lateral movement across multiple Forests
  • ✓Bypassing EDR solutions
  • ✓Relay attacks
  • ✓Operating covertly
Shinra lab avatar
HTB PRO LAB

Shinra

DIFFICULTY Intermediate
MACHINES 14
FLAGS 12
NETWORK TOPOLOGY LAB ENVIRONMENT
Shinra lab network topology diagram
ABOUT THE LAB

Shinra simulates a realistic external breach scenario within a modern electric power company. The objective is to gain an initial foothold by compromising perimeter gateways before progressing through segmented enterprise networks. The environment is monitored by defensive security tools, and read- only SIEM access allows you to monitor the alerts generated by your actions, helping you adapt your approach to minimise detection throughout the engagement.

THE SCENARIO

You have been tasked with performing a red team engagement on Shinra Inc., an electric power company.

Prerequisites

  • ✓Penetration testing methods
  • ✓AD

Learning outcomes

  • ✓Network and AD enumeration
  • ✓AD & custom exploitation
  • ✓AD Certificate Services
  • ✓Lateral movement across multiple Forests
  • ✓Bypassing EDR solutions
  • ✓Relay attacks
  • ✓Operating covertly
  • ✓Phishing attacks
  • ✓Attacking CI/CD infrastructure
  • ✓Backdooring applications
Wutai lab avatar
HTB PRO LAB

Wutai

DIFFICULTY Intermediate
MACHINES 12
FLAGS 12
NETWORK TOPOLOGY LAB ENVIRONMENT
Wutai lab network topology diagram
ABOUT THE LAB

Wutai simulates a realistic enterprise environment consisting of a parent company and its subsidiary, both containing a variety of modern AD vulnerabilities. The goal is to compromise the corporate network from the perspective of an external threat actor. The lab is actively defended by a SOC, and read-only SIEM access enables you to review the alerts generated by your actions, providing insight into how attacker activity is detected and how operational security can be improved.

THE SCENARIO

The Wutai Group has tasked you with performing a penetration test on its networks. This includes the Wutai Parent Company & its subsidiary Junon. Wutai is concerned about its security posture since a leak of domain usernames was found online on pastebin. The goal of this test is to reach Enterprise Administrator in the wutai.vl domain. Wutai employs a small SOC but its blue team capabilities are still on a rather basic level.

Prerequisites

  • ✓Penetration testing methods
  • ✓AD

Learning outcomes

  • ✓Network & AD enumeration
  • ✓AD & custom exploitation
  • ✓AD Certificate Services
  • ✓Lateral movement across multiple Forests
  • ✓Bypassing EDR solutions
  • ✓Reverse engineering
  • ✓Operating covertly
Eldritch lab avatar
HTB MINI PRO LAB

Eldritch

DIFFICULTY Intermediate
MACHINES 5
FLAGS 5
NETWORK TOPOLOGY LAB ENVIRONMENT
Eldritch lab network topology diagram
ABOUT THE LAB

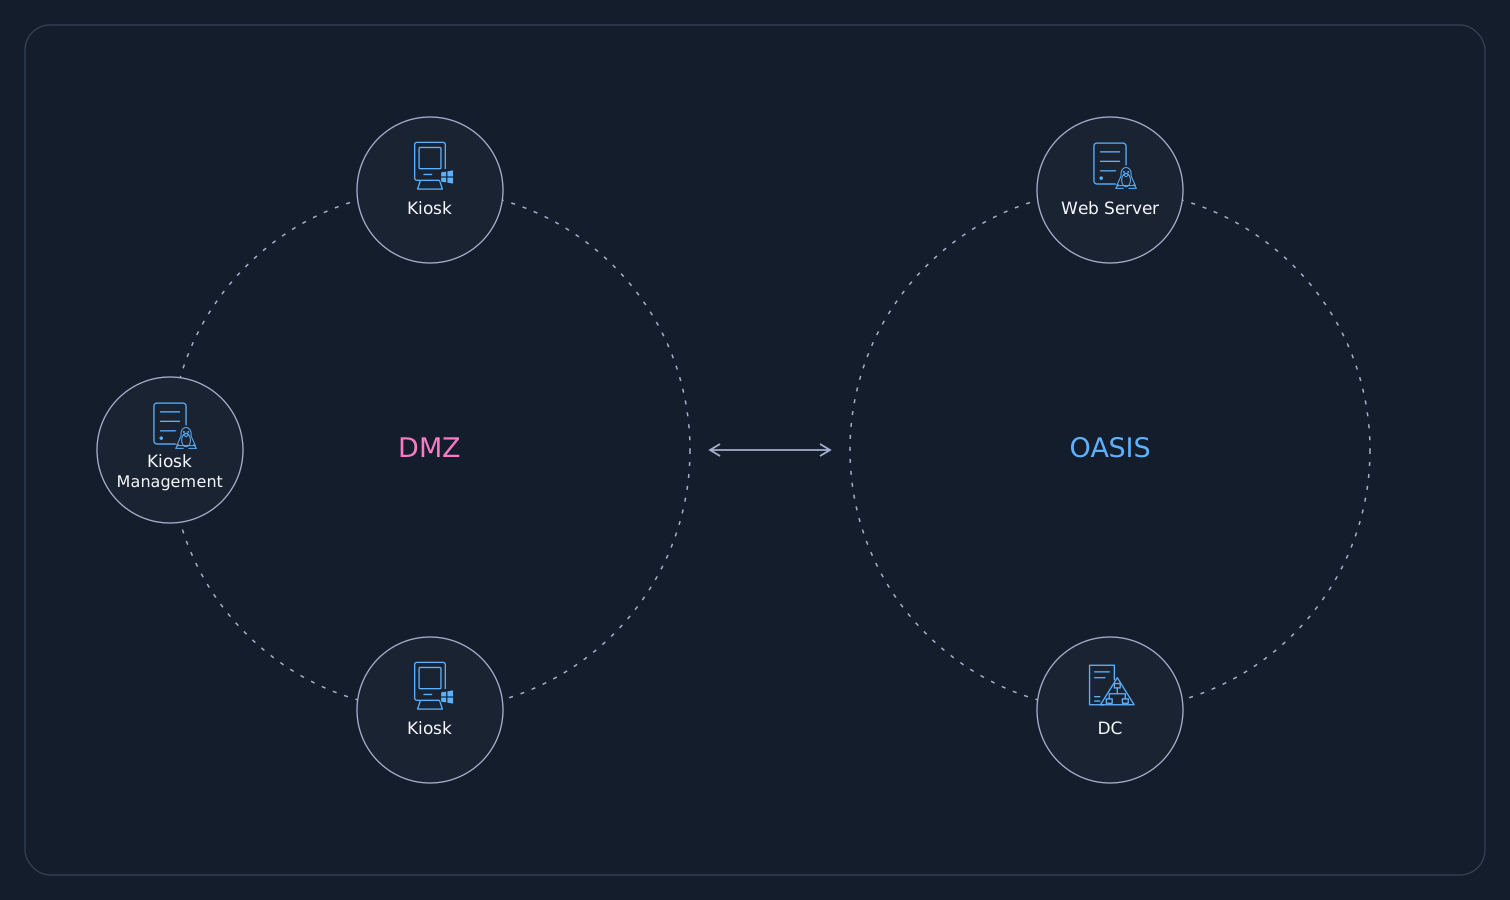
Eldritch is a small lab where the focus lies on web applications and kiosk systems. Users will be introduced to common kiosk breakout techniques within a small Active Directory network. While AD is not the primary focus, a good understanding of common attacks and pivoting methods will be required to obtain Domain Administrator access.

THE SCENARIO

OASIS (Organization for the Acquisition and Study of Incomprehensible Specimens) is a secret organization studying strange anomalies. You have been tasked with performing a penetration test to secure the inner network.

Prerequisites

  • ✓Penetration testing methods
  • ✓Linux/Windows OS
  • ✓AD
  • ✓Web application attacks

Learning outcomes

  • ✓Enumeration
  • ✓Kiosk breakout attacks
  • ✓Lateral movement in AD environments
  • ✓Network pivoting
  • ✓Web application attacks
FullHouse lab avatar
HTB MINI PRO LAB

FullHouse

DIFFICULTY Intermediate
MACHINES 4
FLAGS 7
NETWORK TOPOLOGY LAB ENVIRONMENT
FullHouse lab network topology diagram
ABOUT THE LAB

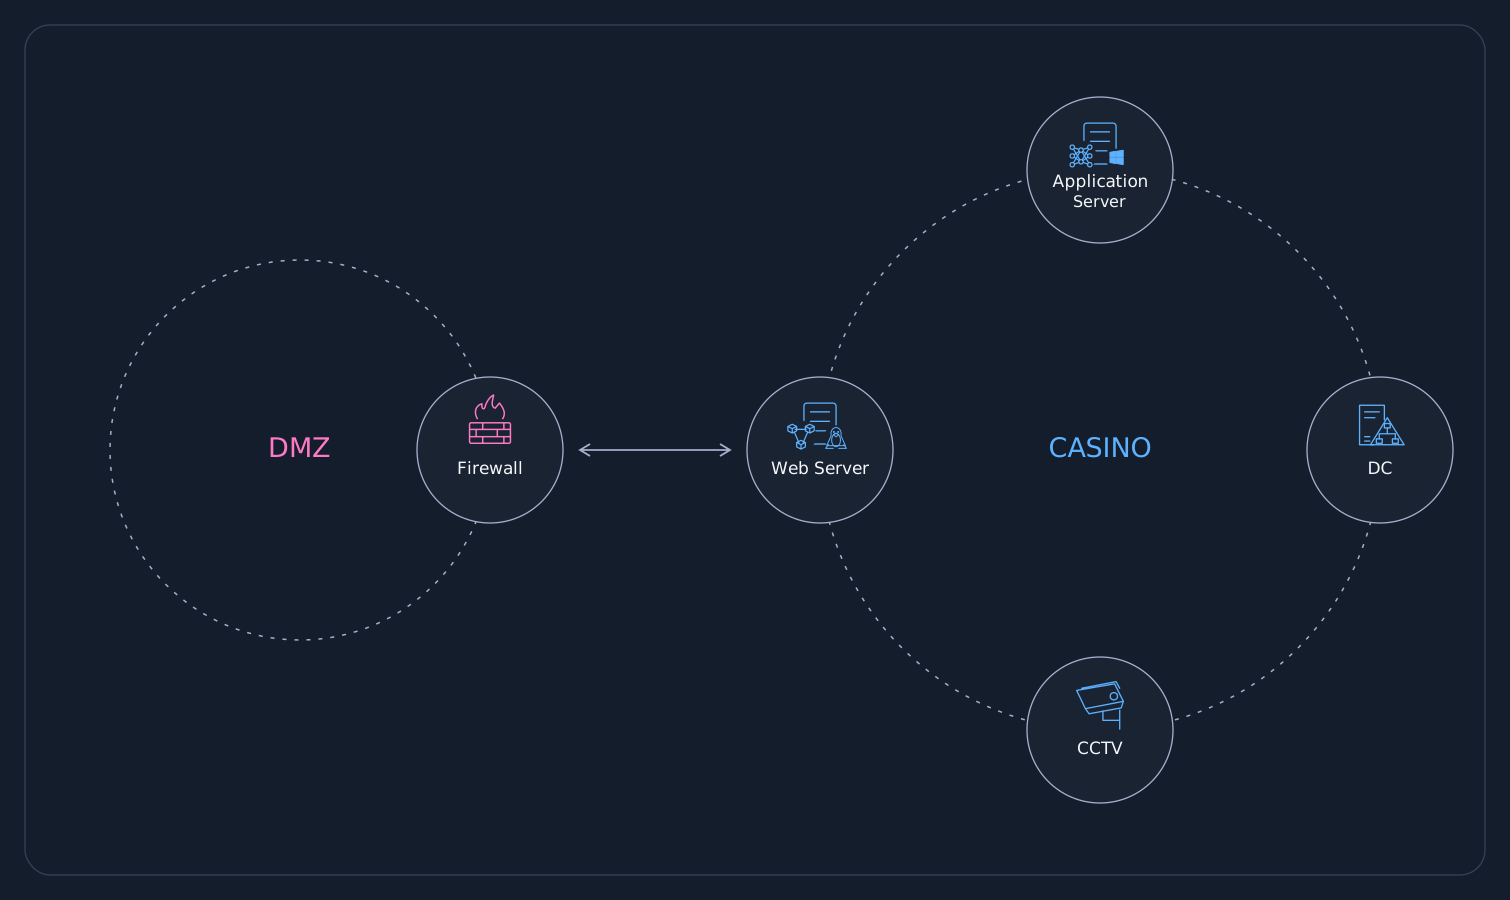
FullHouse is an intermediate-level condensed scenario introducing teams to new emerging threats such as Artificial Intelligence and Machine Learning. This network simulation benchmarks and develops members’ skills in Enumeration, Code Review, Pivoting, and Web Exploitation.

THE SCENARIO

FullHouse manages the HTBCasino and is strongly committed to ensuring the privacy and security of its players. Therefore, the casino has enlisted your expertise to identify and report potential vulnerabilities in both new and legacy components. The objective is to establish a foothold on the internal network, escalate privileges, and ultimately enhance the overall infrastructure security.

Prerequisites

  • ✓Penetration testing tools
  • ✓Linux/Windows OS
  • ✓Pivoting
  • ✓Scripting languages, Windows AD, and Powershell

Learning outcomes

  • ✓Source code review
  • ✓Web application attacks
  • ✓Reversing
  • ✓Windows exploitation
  • ✓AD exploitation
  • ✓Blockchain exploitation
  • ✓AI bypass/exploitation
XEN lab avatar
HTB MINI PRO LAB

XEN

DIFFICULTY Intermediate
MACHINES 6
FLAGS 6
NETWORK TOPOLOGY LAB ENVIRONMENT
XEN lab network topology diagram
ABOUT THE LAB

Xen is designed to test your skills in enumeration, breakout, lateral movement, and privilege escalation within a small Active Directory environment. The goal is to gain a foothold on the internal network, escalate privileges, and ultimately compromise the domain while collecting several flags along the way.

THE SCENARIO

Humongous Retail operates a nationwide chain of stores. The company has reacted to several recent skimming incidents by investing heavily in its POS systems. Keen to avoid any further negative publicity, it has engaged the services of a penetration testing company to assess the security of its perimeter and internal infrastructure.

Prerequisites

  • ✓Penetration testing tools
  • ✓Windows OS
  • ✓Networking
  • ✓AD

Learning outcomes

  • ✓Enumeration
  • ✓Lateral movement
  • ✓Privilege escalation
  • ✓Pivoting
  • ✓Phishing techniques
  • ✓AD enumeration and exploitation
Unintended lab avatar
HTB MINI PRO LAB

Unintended

DIFFICULTY Intermediate
MACHINES 3
FLAGS 4
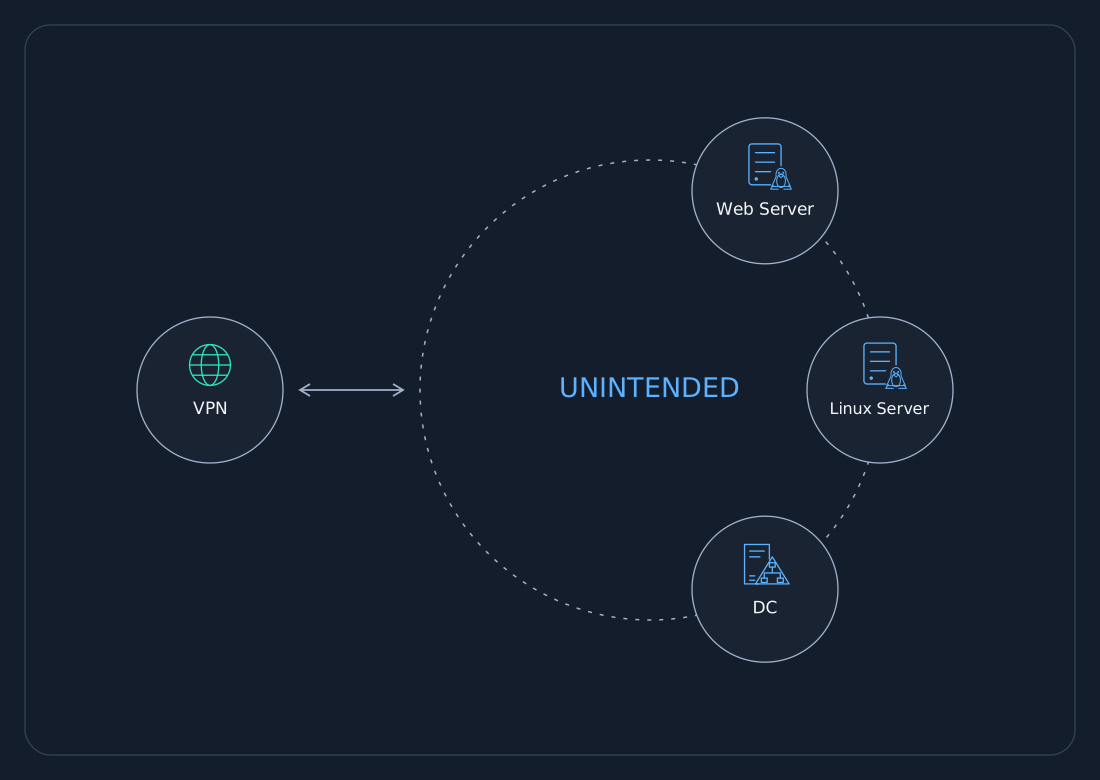
NETWORK TOPOLOGY LAB ENVIRONMENT
Unintended lab network topology diagram
ABOUT THE LAB

Unintended focuses on common missteps in Active Directory deployments, demonstrating how attackers can leverage Linux privilege escalation techniques alongside Active Directory attack paths to pivot between services and progressively escalate privileges within an enterprise environment.

THE SCENARIO

Unintended is a company that has recently migrated its infrastructure to Active Directory. Management is concerned that legacy practices and overlooked misconfigurations could expose the environment to external threats. Your firm has been contracted to conduct a penetration test, with the objective of determining whether an attacker can move from initial access to full control of the domain.

Prerequisites

  • ✓Networking
  • ✓AD
  • ✓Web application attacks
  • ✓Database enumeration

Learning outcomes

  • ✓AD backup enumeration
  • ✓Lateral movement
  • ✓Networking pivoting
  • ✓Linux privilege escalation
  • ✓Backup Forensics
  • ✓Web application attacks
Puppet lab avatar
HTB MINI PRO LAB

Puppet

DIFFICULTY Intermediate
MACHINES 3
FLAGS 4
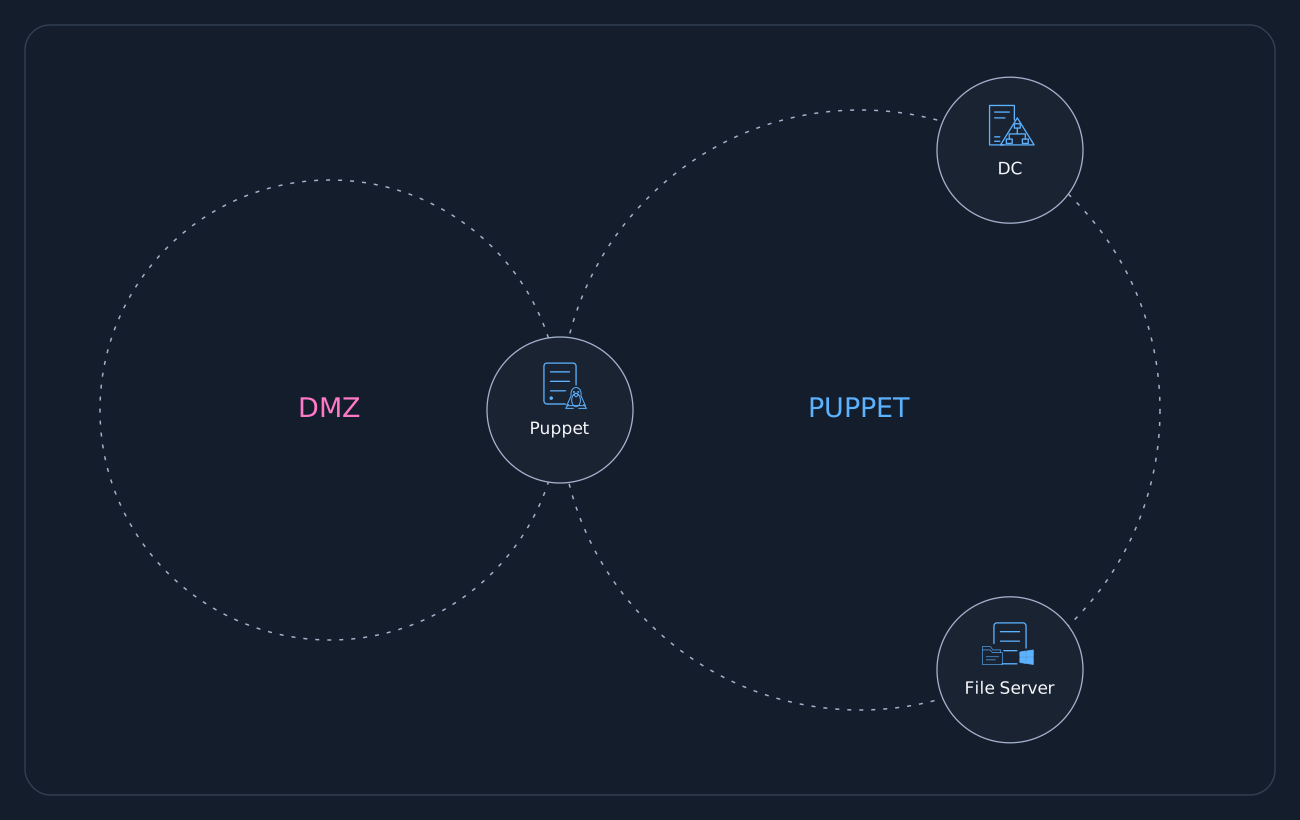
NETWORK TOPOLOGY LAB ENVIRONMENT
Puppet lab network topology diagram
ABOUT THE LAB

Puppet simulates a hybrid corporate infrastructure heavily managed by DevOps automation tools. Starting with an active Silver C2 beacon in a network that prohibits external egress, your goal is to bypass modern endpoint controls, discover misconfigurations, and ultimately hijacking the central server.

THE SCENARIO

You are tasked with performing a red team engagement on Puppet Inc. The company does not allow data to leave the internal network, so a C2 server has been set up internally and an employee executed a payload in order to simulate a successful social engineering attack.

Prerequisites

  • ✓Penetration testing methods
  • ✓AD
  • ✓C2

Learning outcomes

  • ✓Enumeration
  • ✓AD enumeration and attacks
  • ✓Exploiting DevOps infrastructure
  • ✓Lateral movement
  • ✓Local privilege escalation
  • ✓C2 operations
Heron lab avatar
HTB MINI PRO LAB

Heron

DIFFICULTY Intermediate
MACHINES 2
FLAGS 3
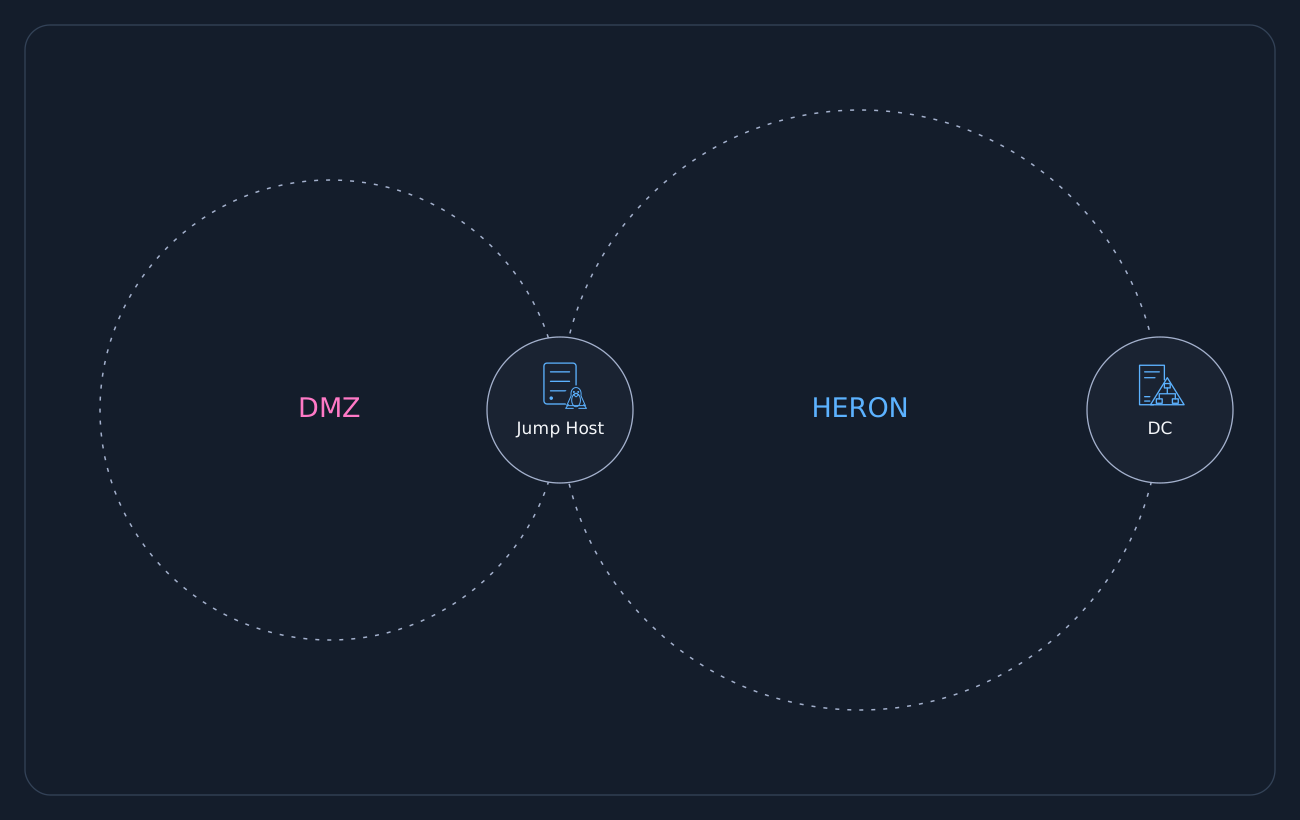
NETWORK TOPOLOGY LAB ENVIRONMENT
Heron lab network topology diagram
ABOUT THE LAB

Heron simulates a realistic corporate Active Directory environment in which you have to pivot through the network, enumerate the domain, and chain together a series of misconfigurations to progressively escalate privileges and ultimately achieve full domain compromise.

THE SCENARIO

You are tasked with performing a penetration test on Heron, starting with the credentials of an employee in an assumed breach scenario.

Prerequisites

  • ✓Penetration testing methods
  • ✓AD

Learning outcomes

  • ✓Enumeration
  • ✓AD enumeration and attacks
  • ✓Lateral movement
  • ✓Local privilege escalation
Tengu lab avatar
HTB MINI PRO LAB

Tengu

DIFFICULTY Intermediate
MACHINES 3
FLAGS 3
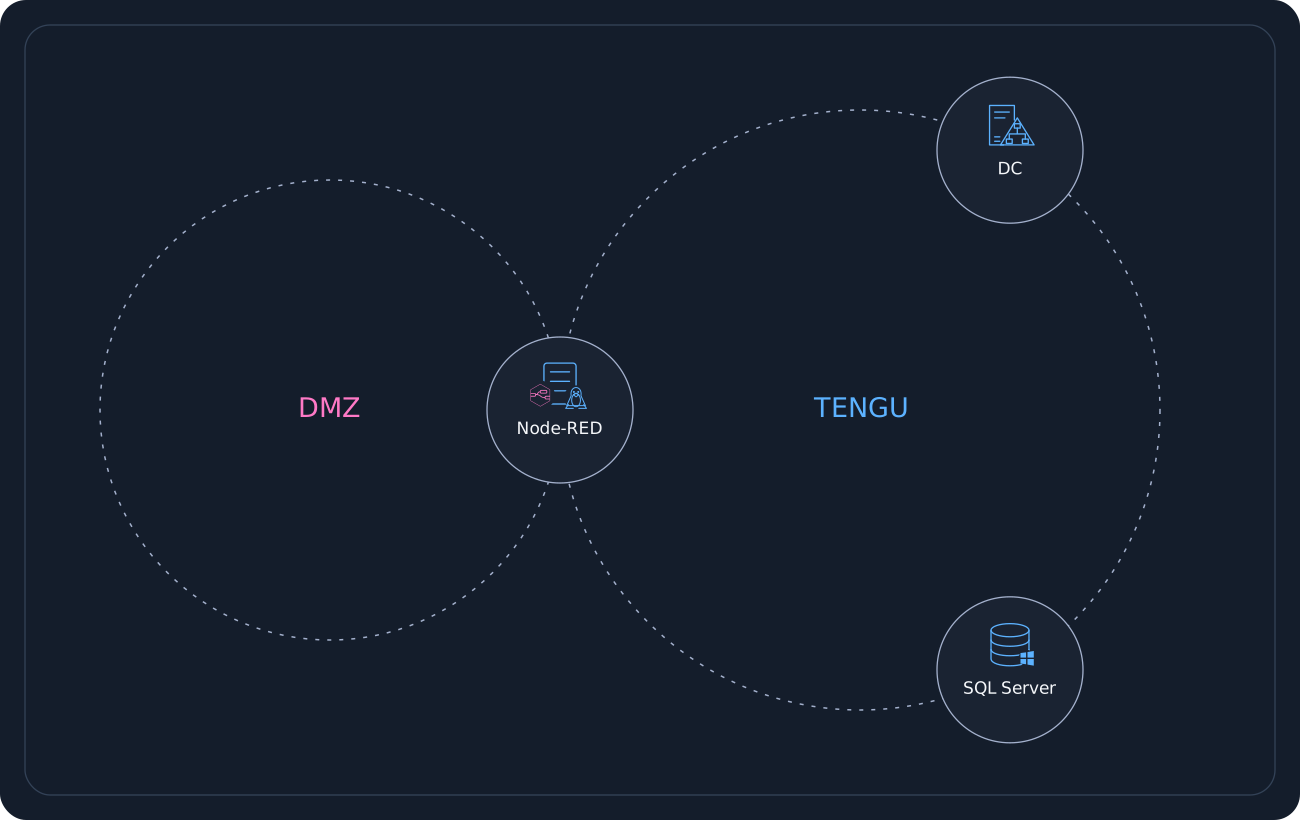
NETWORK TOPOLOGY LAB ENVIRONMENT
Tengu lab network topology diagram
ABOUT THE LAB

Tengu is a small Active Directory scenario that involves typical vulnerabilities found in real-world company environments.

THE SCENARIO

You are tasked with performing a penetration test on Tengu, involving a mixed Active Directory environment.

Prerequisites

  • ✓Penetration testing methods
  • ✓AD
  • ✓Pivoting to internal networks
  • ✓Linux

Learning outcomes

  • ✓AD attacks
  • ✓Pivoting to internal networks
  • ✓MSSQL attacks
  • ✓Kerberos attacks
  • ✓DPAPI operations
Tea lab avatar
HTB MINI PRO LAB

Tea

DIFFICULTY Intermediate
MACHINES 2
FLAGS 3
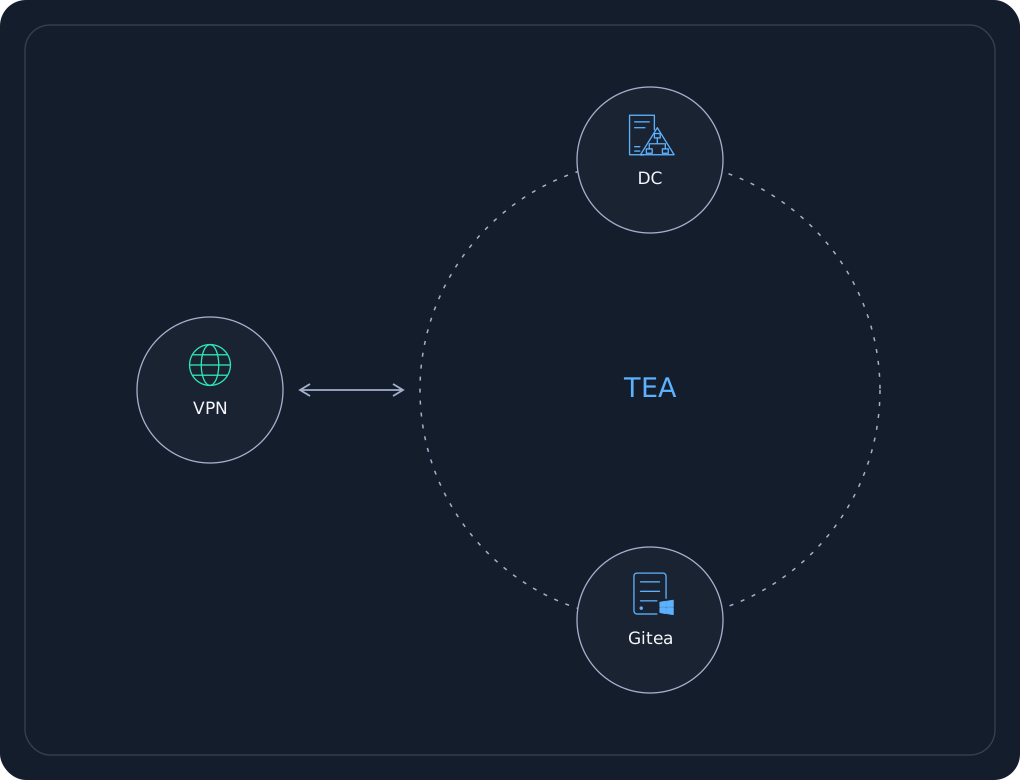
NETWORK TOPOLOGY LAB ENVIRONMENT
Tea lab network topology diagram
ABOUT THE LAB

Tea simulates an AD environment incorporating modern DevOps and enterprise update management infrastructure. The goal is to gain an initial foothold without valid credentials, leverage development and management services to escalate privileges, and ultimately compromise the domain controller.

THE SCENARIO

You are tasked with performing a red team engagement on Tea Inc. You are provided access to the internal network with no credentials, and your goal is to assess the security posture of the AD environment.

Prerequisites

  • ✓Penetration testing methods
  • ✓AD
  • ✓Networking
  • ✓Git and Gitea knowledge

Learning outcomes

  • ✓AD enumeration & attacks
  • ✓Abusing misconfigurations in common services
  • ✓Gitea actions
  • ✓Windows technologies like LAPS and WSUS
Lustrous lab avatar
HTB MINI PRO LAB

Lustrous

DIFFICULTY Intermediate
MACHINES 2
FLAGS 2
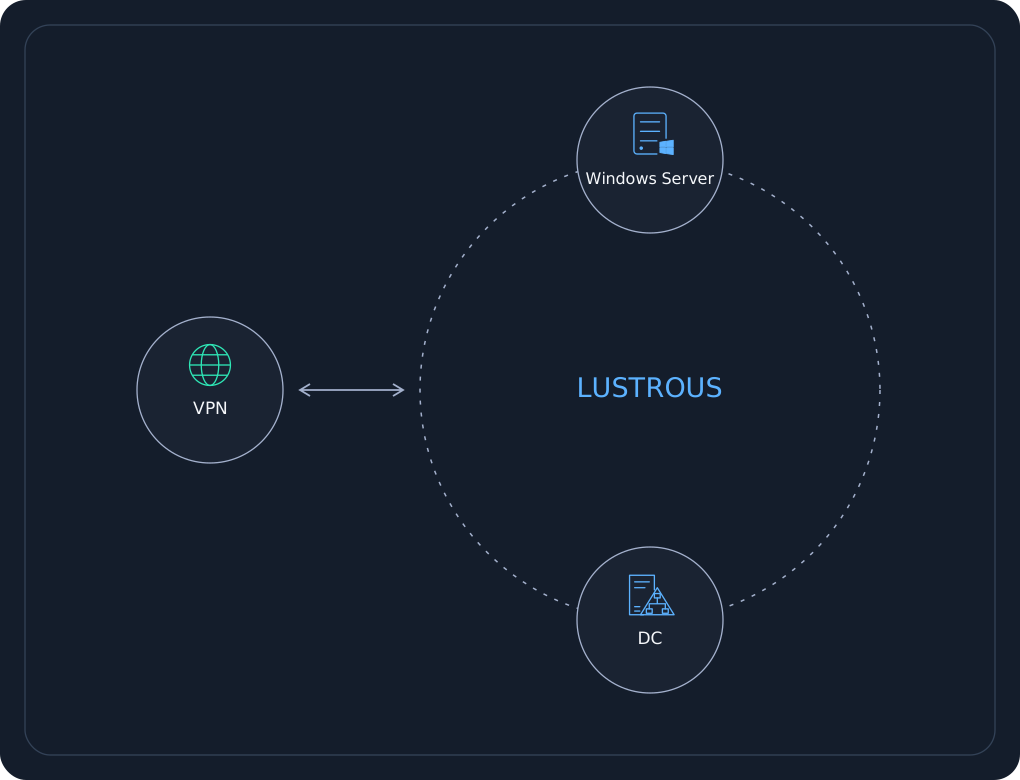
NETWORK TOPOLOGY LAB ENVIRONMENT
Lustrous lab network topology diagram
ABOUT THE LAB

Lustrous simulates a medium-to-advanced AD environment within a Windows-based enterprise network. The goal is to enumerate exposed services, obtain initial access to the domain, and progressively escalate privileges by identifying and exploiting misconfigurations in authentication, credential management, and delegated permissions, ultimately achieving full domain compromise.

THE SCENARIO

The Lustrous scenario simulates a security assessment of a corporate AD environment, challenging participants to identify weaknesses in authentication, access controls, and privilege management across interconnected domain system within a realistic enterprise infrastructure.

Prerequisites

  • ✓Penetration testing methods & attack lifecycle
  • ✓AD architecture and security concerns
  • ✓Kerberos authentication and ticket abuse techniques
  • ✓Credential attacks (AS-REP roasting, Kerberoasting, NTLM)
  • ✓Windows authentication (SMB, WinRM, RDP)
  • ✓Windows privilege escalation and built-in privilege groups
  • ✓Credential storage (SAM, SYSTEM, DPAPI, SecureString)
  • ✓Analyze AD attack paths using tools like BloodHound

Learning outcomes

  • ✓AD enumeration and attacks
  • ✓Kerberos exploitation techniques
  • ✓Credential access and abuse
  • ✓Lateral movement
  • ✓Privilege escalation (Local & Domain)
  • ✓Service & infrastructure abuse
Neural lab avatar
HTB MINI PRO LAB

Neural

DIFFICULTY Intermediate
MACHINES 5
FLAGS 4
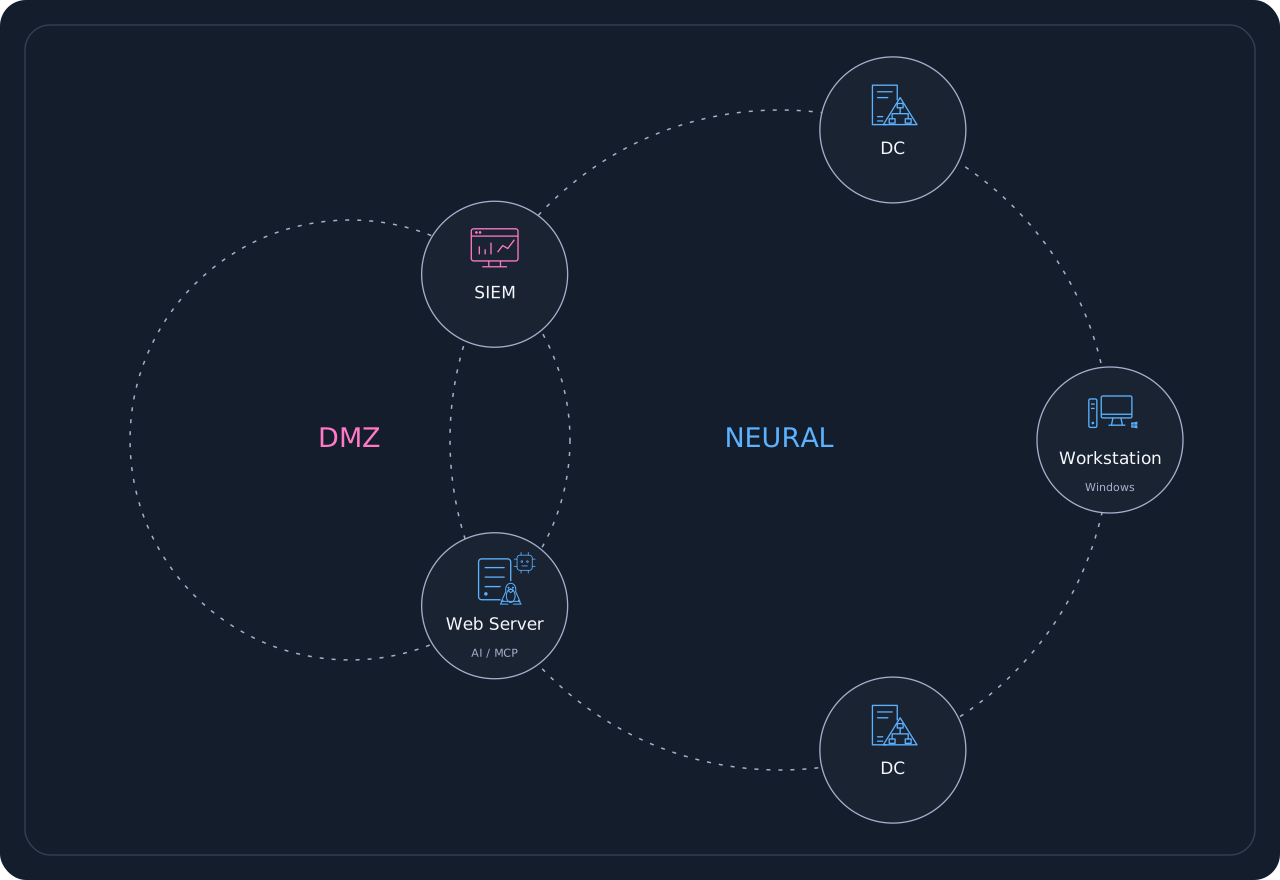
NETWORK TOPOLOGY LAB ENVIRONMENT
Neural lab network topology diagram
ABOUT THE LAB

Neural is an intermediate-level AI and AD hybrid environment designed for players who want to improve their enumeration and exploitation skills on AI agents and AD environments. With a range of AD flaws and misconfigurations as well as introductory AI workflows and agent-based attack vectors, players will be able to get a foothold in corporate environments.

THE SCENARIO

Neural is a tech consultancy specializing in integrating AI-driven automation into business workflows. As Neural scales, so does the complexity of their infrastructure. The goal is to compromise both external and internal infrastructure by identifying weaknesses, gaining initial access, and pivoting across trust boundaries.

Prerequisites

  • ✓Penetration testing tools
  • ✓Windows/Linux OS
  • ✓Windows AD
  • ✓Microsoft SQL servers
  • ✓LLMs and AI agents
  • ✓Prompt injection techniques
  • ✓RAG
  • ✓BloodHound usage

Learning outcomes

  • ✓Enumeration
  • ✓Prompt injection attacks
  • ✓RAG poisoning and context manipulation
  • ✓MCP server exploitation
  • ✓AI agent abuse & workflow exploitation
  • ✓Lateral movement and crossing trust boundaries
  • ✓Privilege escalation
  • ✓Cross-forest abuse
Reflection lab avatar
HTB mini PRO LAB

Reflection

DIFFICULTY Intermediate
MACHINES 3
FLAGS 3
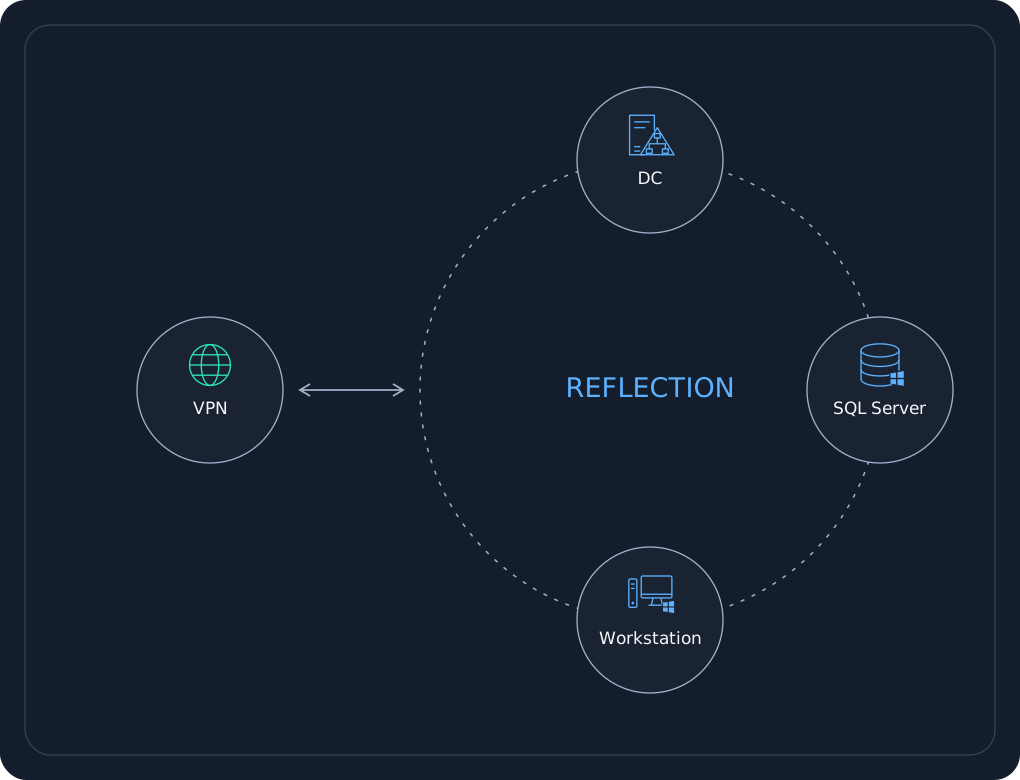
NETWORK TOPOLOGY LAB ENVIRONMENT
Reflection lab network topology diagram
ABOUT THE LAB

Reflection is a medium-difficulty Active Directory scenario that simulates a vulnerable enterprise environment and challenges you to progress from limited access to Domain Administrator.

THE SCENARIO

You are tasked with performing a penetration test on Reflection, an Active Directory environment that simulates a realistic multi-host Windows infrastructure.

Prerequisites

  • ✓Penetration testing methods
  • ✓AD
  • ✓Networking

Learning outcomes

  • ✓MSSQL enumeration and credentials discovery
  • ✓NTLM hash relay attacks
  • ✓AD enumeration with BloodHound
  • ✓Local Administrator Password Solution (LAPS) abuse
  • ✓Resource-Based Constrained Delegation (RBCD)
  • ✓Credential harvesting and lateral movement